By clicking “Accept”, you agree to the storing of cookies on your device to enhance site navigation, analyze site usage, and assist in our marketing efforts. View our Privacy Policy for more information.
Why teams leave Panorays, how 8 Panorays competitors compare on evidence and fit, plus dated review scores and a renewal checklist
Risk Ledger
|
Company
October 27, 2026
|
30
mins read
Share
Updated 27th October 2026: added Black Kite, rebuilt the comparison table, and added sections on evidence sources, nth-party visibility, cost, reviewer scores, public sector fit and switching at renewal.
Quick answer
Panorays is a third-party risk platform that combines supplier questionnaires with external attack-surface scanning. The right alternative depends on which part of that job you want to improve, whether that's external visibility, assessment workflow, GRC breadth, or how much evidence your team has to collect again for every supplier.
Closest like-for-like swap. UpGuard, which combines external scanning, questionnaires and remediation tracking in one platform.
Outside-in ratings across a large supplier base. Bitsight, SecurityScorecard or Black Kite, which score suppliers without needing them to respond.
Questionnaire and workflow depth. Mitratech Prevalent or ProcessUnity, both built around configurable assessments.
Third-party risk inside a wider GRC programme. OneTrust Third-Party Management.
Less chasing for answers suppliers have already given. Risk Ledger, where suppliers maintain one profile that each connected customer reviews against its own requirements.
Most teams comparing Panorays alternatives aren’t short of tools that can produce a score, they’re short of time. A security team of one or two people has to do three jobs at once. They have to chase suppliers for answers already given to other customers, and defend external findings to the board. They also have to notice what changed after the contract was signed. One public sector security lead summed up the capacity problem to us in five words: “there are not three of me”.
Thats why below we've looked at where each platform’s evidence comes from, and how much of the collection work your team still carries for every supplier. Panorays combines automated questionnaires with external scanning in one dashboard. That’s why it appears in searches for both ratings tools and assessment platforms.
The 8 Panorays competitors and alternatives covered in this guide
UpGuard: best for scanning, questionnaires and remediation in one tool, the closest like-for-like swap
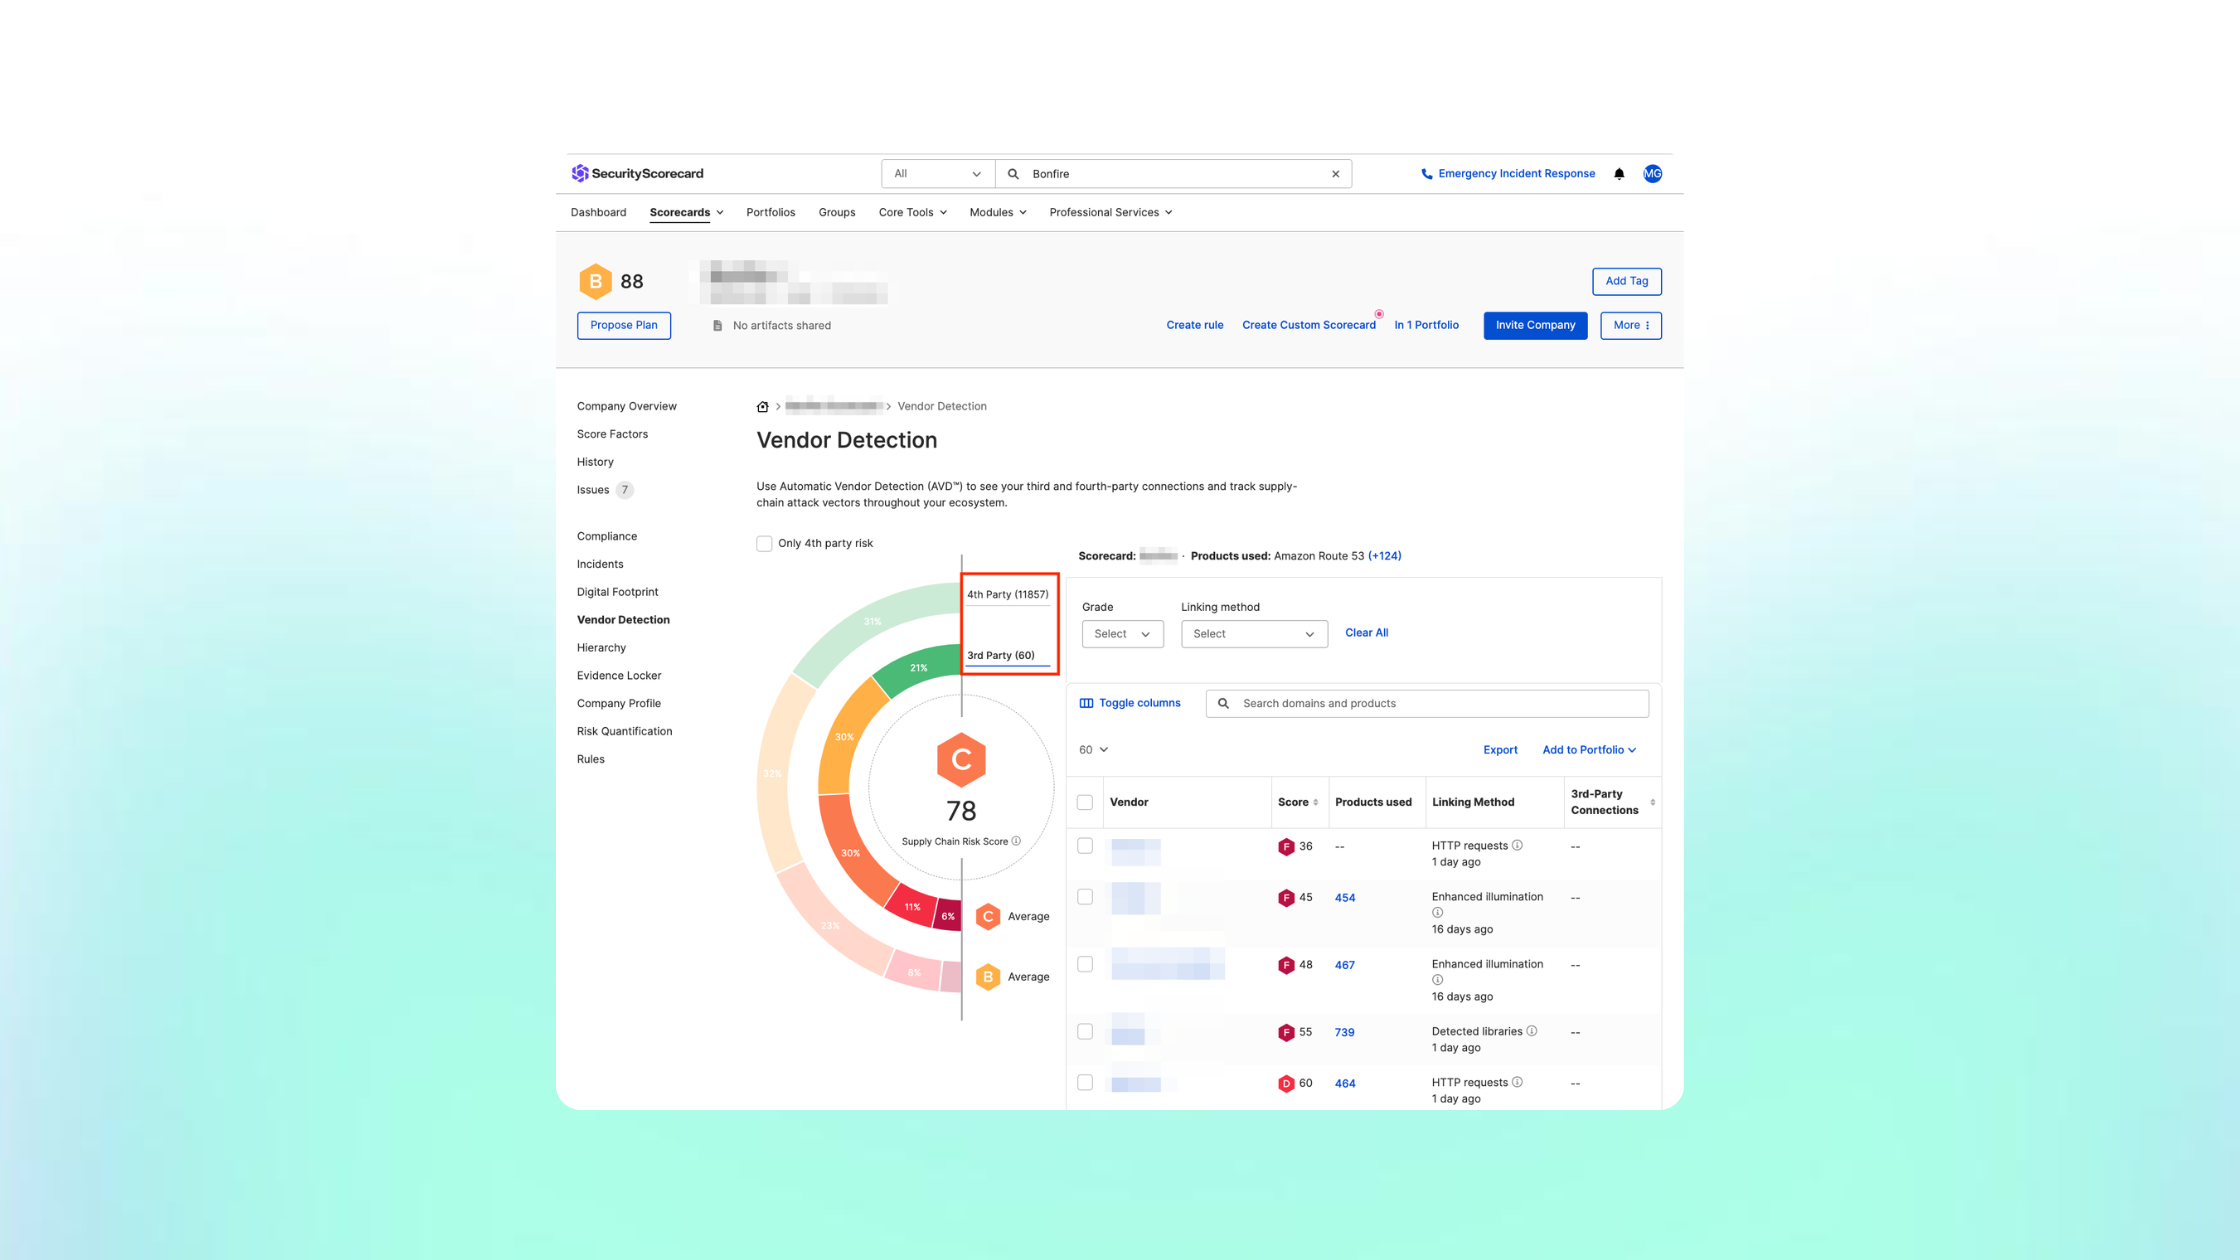
SecurityScorecard: best for ratings combined with peer benchmarking and threat intelligence
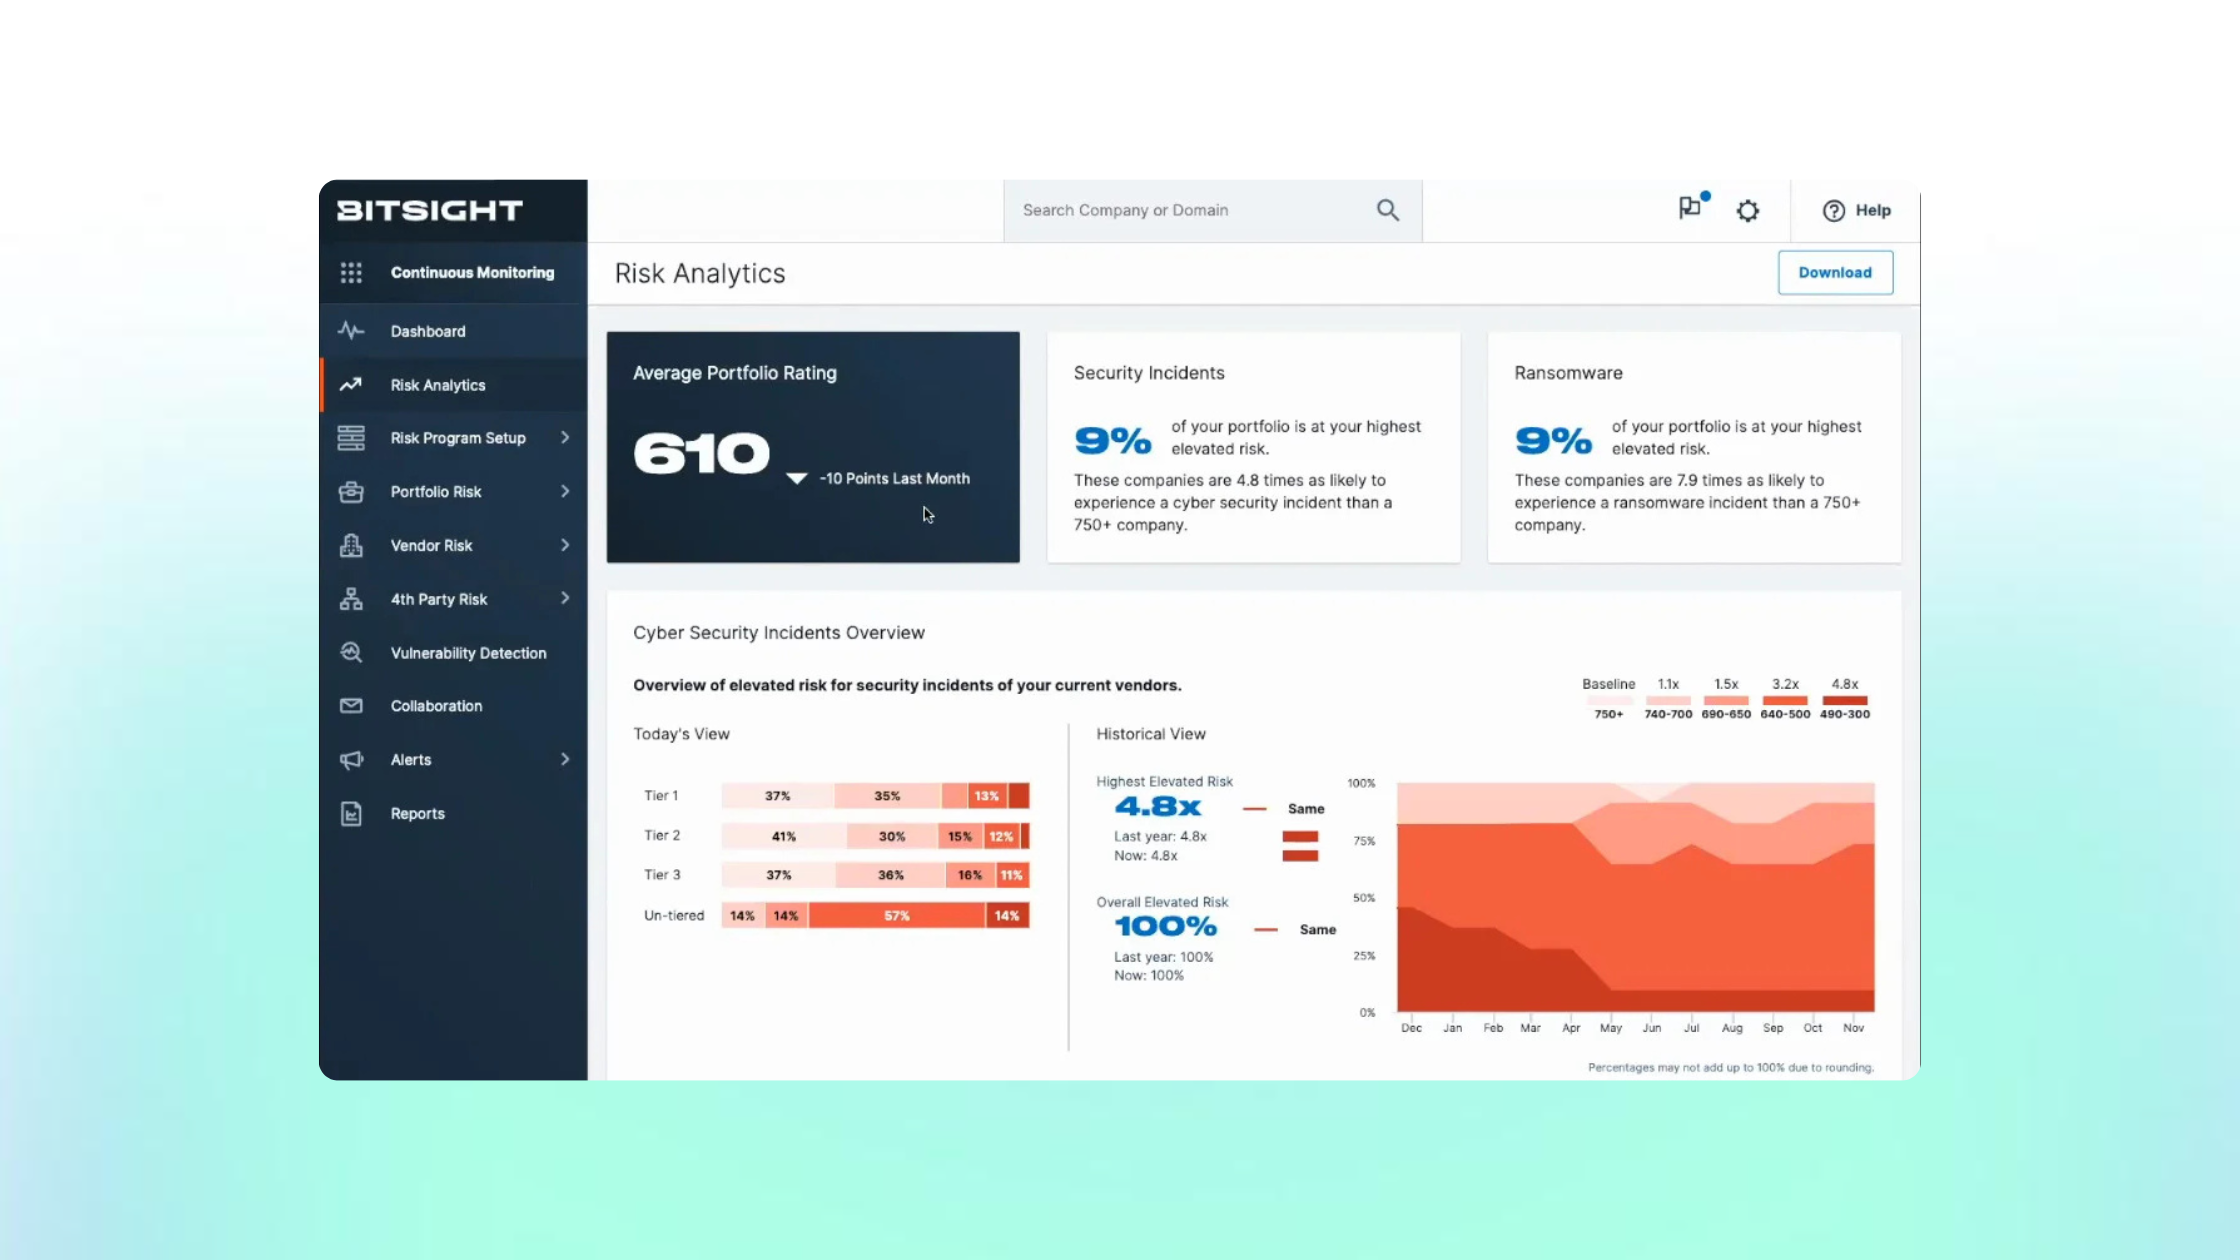
Bitsight: best for portfolio-level security ratings at scale
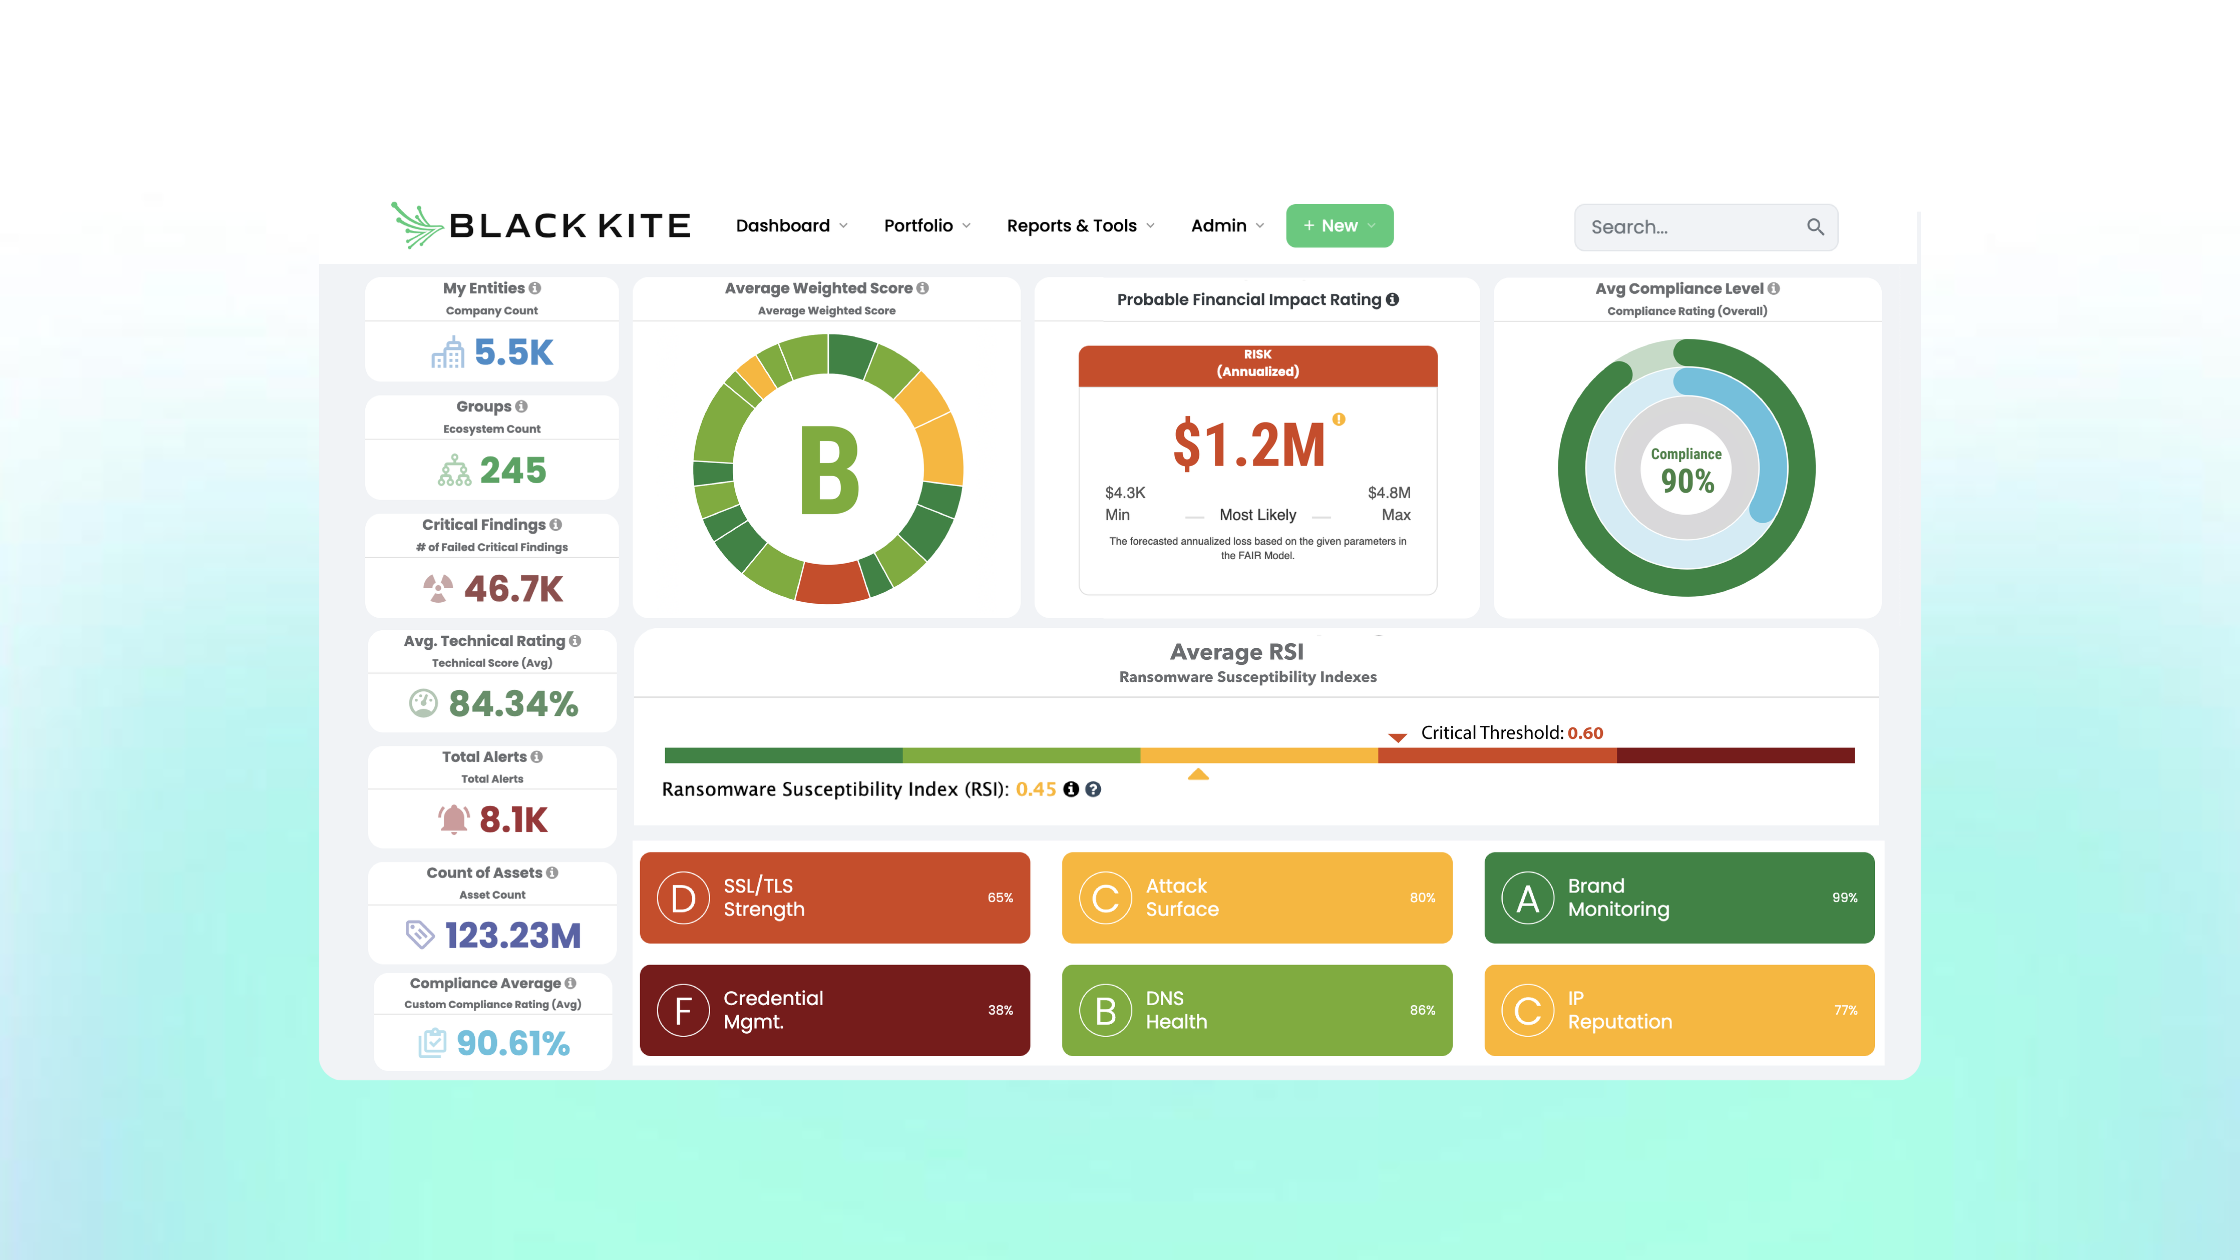
Black Kite: best for outside-in ratings with fourth-party mapping
Mitratech Prevalent: best for configurable assessment workflows, with a managed service option
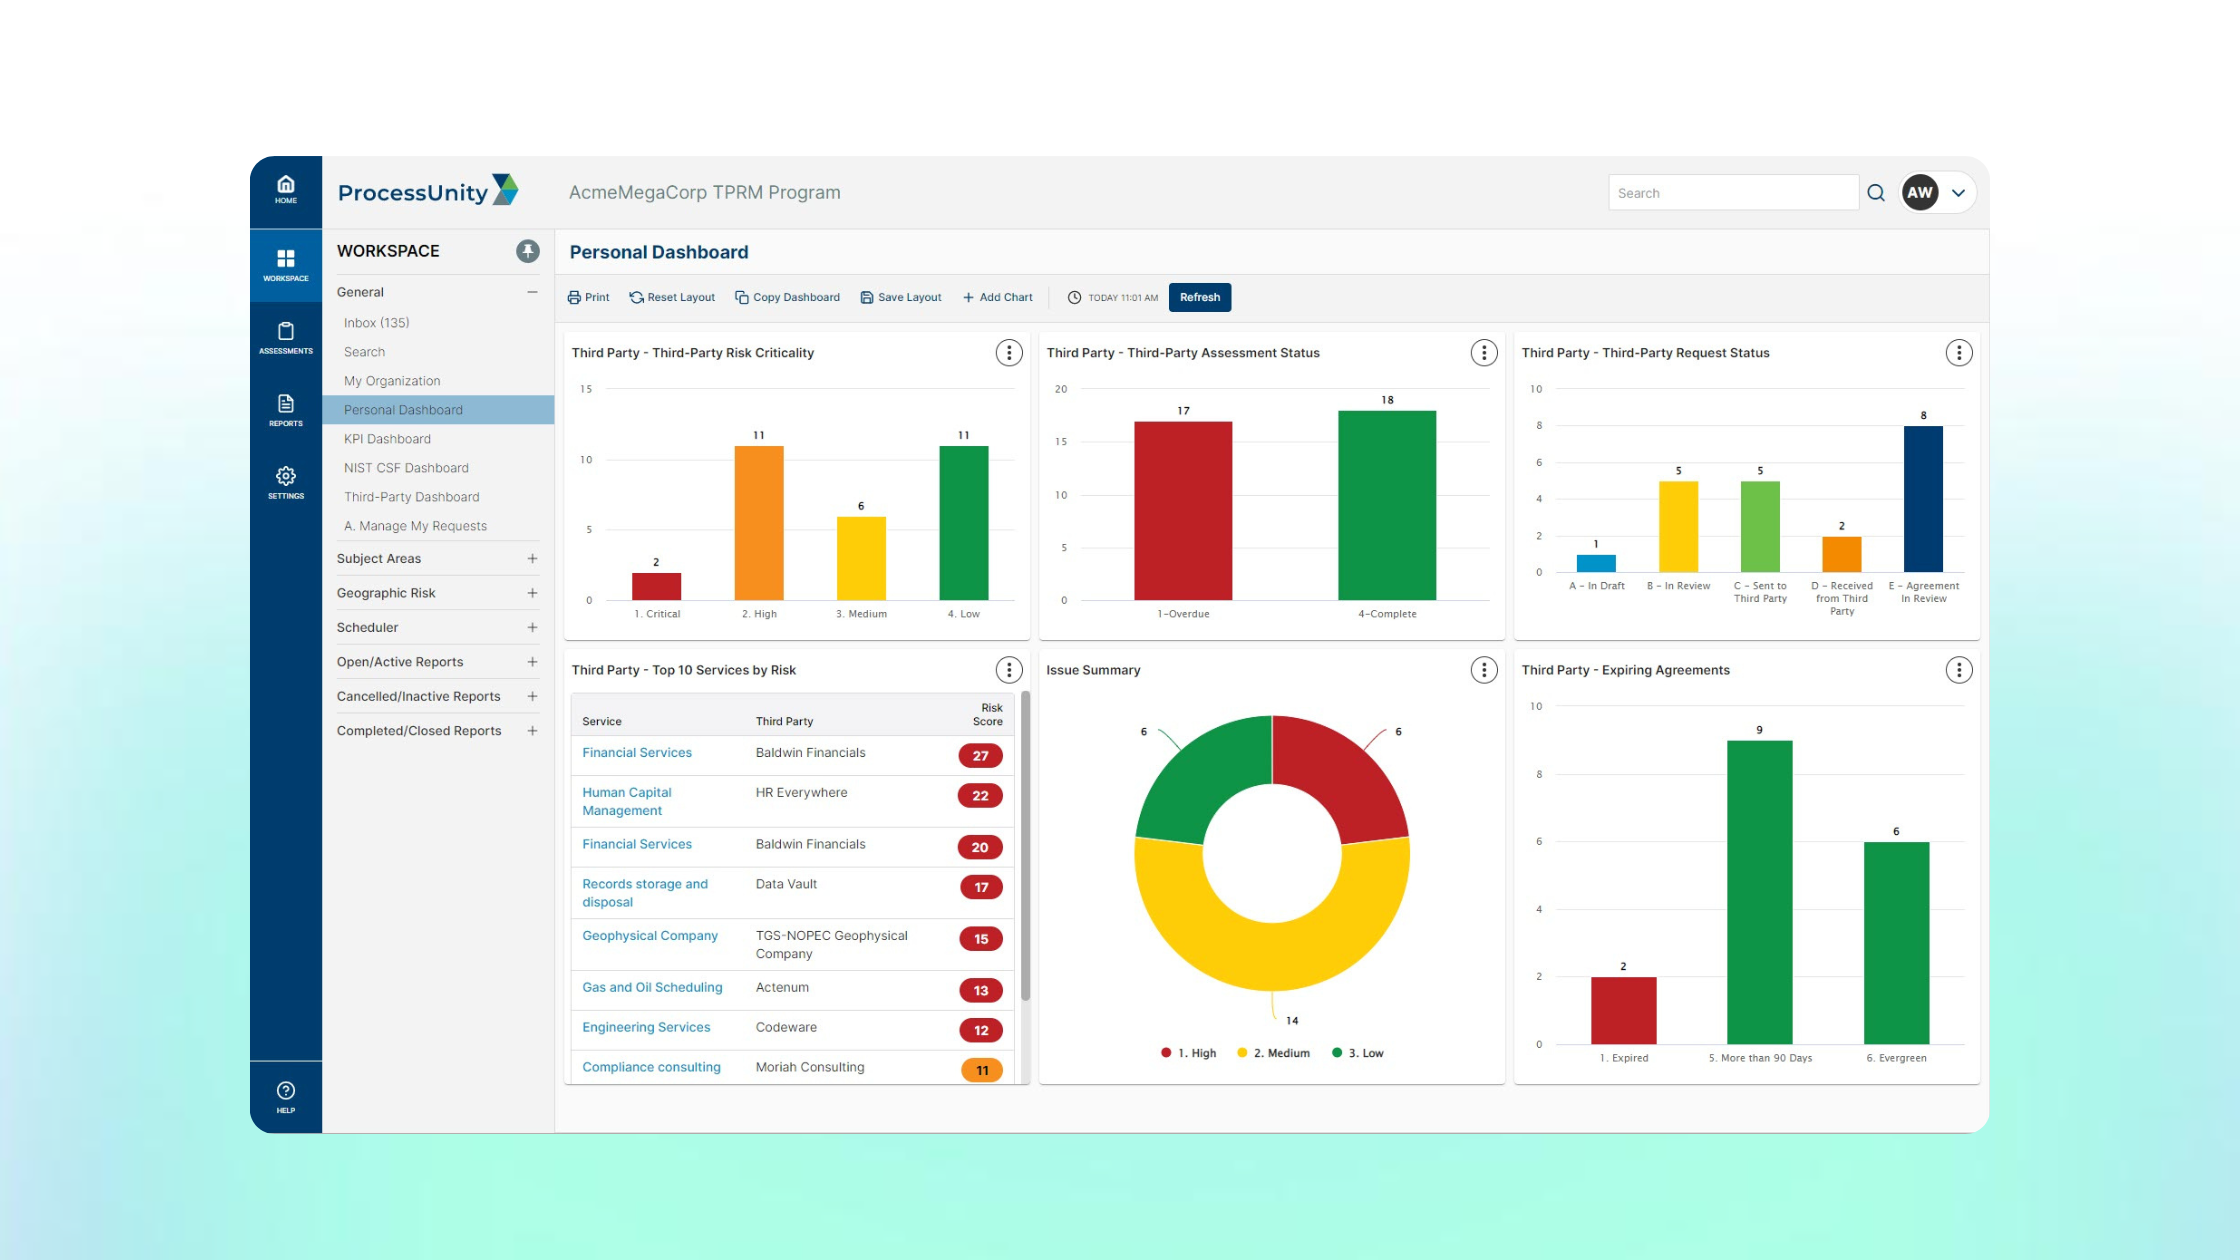
ProcessUnity: best for highly configurable enterprise TPRM, now including the former CyberGRX exchange
OneTrust: best for third-party risk inside a broad GRC programme
Risk Ledger: best for teams that want suppliers to share one maintained profile instead of answering every customer separately
This isn’t a universal ranking. The order reflects how closely each platform overlaps with Panorays, and we’ve put ourselves last.
We group the platforms four ways throughout the guide.
Security ratings platforms (UpGuard, SecurityScorecard, Bitsight, Black Kite) start from what they can observe about a supplier externally, and most add questionnaires on top.
Vendor risk workflow tools (Mitratech Prevalent, ProcessUnity) centre on assessments, workflow and remediation.
Broad GRC suites (OneTrust) place third-party risk inside a wider compliance programme.
Supplier networks (Risk Ledger) have suppliers maintain one security profile, which each connected customer reviews against its own requirements.
How we compared: this guide draws on G2, Gartner Peer Insights, TrustRadius and PeerSpot reviews for each platform, on vendors’ own product documentation for capability claims, and on themes from our conversations with teams reviewing Panorays.
Why do security teams leave Panorays?
Security teams usually leave Panorays for operational reasons rather than because the platform falls short. Reviewers rate it well overall, but they raise setup effort, limited reporting customisation, coarse role controls and an API that updates whole supplier records. In sales conversations, the larger theme is the workload of running every supplier relationship one to one.
From public reviews
What reviewers raise
Setup takes effort. Reviewers describe initial setup and onboarding as demanding, partly because there is so much to configure.
Reporting is hard to tailor. Limited customisation of reports and dashboards is a recurring complaint.
Role controls are coarse. Larger teams want finer control over what different user groups can view or change.
The API updates whole records. Some changes require updating the entire supplier entity rather than a single field, which adds integration friction.
Scan findings need checking. Reviewers mention false positives in external scans and occasional delays in data updates.
From our conversations
What teams reviewing Panorays tell us
Every relationship starts from scratch. Each supplier is assessed in isolation, so the same questions go out again for every customer that asks.
Suppliers don't always respond. Requests sit unanswered, and pushing back on an answer is a slow process.
Scores lack business context. A generic score says little about how a supplier is actually used or how much it matters.
Costs rise at renewal. Long-standing customers question value as licence costs go up year on year.
These are directional themes from a small number of sales conversations, not survey results. Test each one against your own supplier sample.
The one-to-one model is the pattern we hear most often from teams reviewing Panorays.
Each supplier relationship runs on its own. A questionnaire goes out from your account, the supplier answers it for you, and the next customer to ask that supplier starts again from a blank form.
That has two costs: your team spends time chasing responses, and some suppliers stop engaging with yet another portal. One Panorays user told us the model creates significant manual work. A G2 reviewer offered blunter advice to anyone buying, which was to make sure the team is big enough to absorb the extra workload.
Neither cost is specific to Panorays. Any platform that collects evidence relationship by relationship carries some version of it, so it belongs in the evaluation criteria for every alternative in this guide, ours included.
Renewal is when most of these reviews happen. Teams describe licence costs rising while the collection workload stays the same, and they use the renewal window to see what else exists. If you’re mid-contract, a side-by-side trial on a small supplier sample tests an alternative with far less risk than a straight switch.
When Panorays is still the right choice
Panorays is still the right choice for teams that want questionnaires and external scanning in one easy-to-use tool, that work mainly one to one with a modest supplier base, and that need DORA reporting built in. If that describes your programme, changing platforms may cost more in disruption than it saves.
Four strengths come up consistently, and any alternative should be tested against them:
Combined workflow: Reviewers describe Panorays as bringing ratings, tailored questionnaires and continuous monitoring together, which is why several teams moved to it from separate tools.
Ease of use: It’s the strength G2 reviewers mention most often, and it matters more than feature depth for a team of one or two.
Visibility beyond direct suppliers: Panorays says its supply chain discovery detects third to nth parties and flags concentration risk.
DORA: Panorays generates the Register of Information as a ready-to-submit report and provides DORA questionnaires mapped to it. For an EU-regulated financial entity, that replaces a heavy spreadsheet exercise.
Stay
Panorays is likely still a good fit if
You want scanning and questionnaires in one tool, and the team finds it easy to use.
Your supplier base is modest and most relationships run one to one without much chasing.
DORA Register of Information reporting is a hard requirement and the built-in report works for you.
Your main complaints are about reporting, role controls or the API.
Look elsewhere
An alternative is worth testing if
Collecting and chasing supplier answers takes most of the team's time.
Critical suppliers regularly ignore or delay assessment requests.
You can't explain how a supplier's score relates to the service it provides you.
Renewal costs are rising while the collection workload stays the same.
Practical decision rule
If your complaints are about features, negotiate them at renewal. If they're about the one-to-one workload, test a different model on five real suppliers before you renew.
Panorays alternatives compared
Panorays alternatives differ less on features than on where their evidence starts. Ratings platforms start from external scanning, and workflow tools start from configurable questionnaires. GRC suites start from a wider compliance programme, and supplier networks start from profiles that suppliers maintain themselves. Most now combine several sources, so the table compares each platform’s starting point rather than its feature list.
Panorays alternatives comparison
Panorays and 8 alternatives, side by side
Compare where each platform's evidence comes from, how it monitors suppliers, how far it sees into the supply chain and what suppliers are asked to do.
How we compared: capability details come from each vendor's own product, pricing and help pages.
Panorays
Assessments and scanning
Panorays comparison
Best for
Teams that want questionnaires and external scanning in one tool
Primary approach
Customisable questionnaires combined with external attack-surface assessment in one platform.
Supplier evidence
Questionnaire answers are checked against the supplier's external documents and cyber posture, with gaps highlighted for review.
Monitoring
Continuous monitoring of each supplier's external security posture alongside questionnaire data.
Supply chain visibility
Supply chain discovery detects third to nth parties and flags concentration risk.
Supplier participation
Suppliers answer customer-sent questionnaires, and can share a Security Passport self-assessment with prospective customers.
Key consideration
DORA Register of Information reporting is built in, which matters for EU-regulated financial entities.
UpGuard
Security ratings
UpGuard comparison
Best for
Ratings, questionnaires and remediation in one platform
Primary approach
Security ratings from external scanning, combined with questionnaires, evidence requests and remediation workflows.
Supplier evidence
A library of pre-built questionnaires covering frameworks such as NIST, ISO and SIG, plus documents and trust pages suppliers choose to share.
Monitoring
Ratings update multiple times a day from daily scanning.
Supply chain visibility
Fourth-party risk from external data, included in UpGuard's upper pricing tiers.
Supplier participation
Suppliers respond through a free Trust Exchange account, which lets them reuse answers across requests and control which customers see their information.
Key consideration
Entry pricing is published, so check which tier includes fourth-party risk before comparing quotes.
SecurityScorecard
Security ratings
SecurityScorecard comparison
Best for
Ratings combined with threat intelligence and automated vendor response
Primary approach
Outside-in security ratings with threat intelligence, plus questionnaire management and vendor response workflows.
Supplier evidence
External signals scored into a rating, with pre-built questionnaires in the Core package and custom questionnaires in Premium.
Monitoring
Continuous monitoring with alerts when a supplier's score changes.
Supply chain visibility
Automated identification of third and fourth parties, included in the Premium package.
Supplier participation
Suppliers can claim a free scorecard for their own domain, work through open issues and respond to questionnaires.
Key consideration
Fourth-party discovery and custom questionnaires sit in Premium rather than Core, so confirm the package before comparing prices.
Bitsight
Security ratings
Bitsight comparison
Best for
Portfolio-level ratings and monitoring at enterprise scale
Primary approach
Daily security ratings from external data, with a vendor risk management module for assessments.
Supplier evidence
AI-assisted assessments mapped to frameworks such as SIG Lite, NIST CSF 2.0 and ISO 27001, with responses validated against external data.
Monitoring
Daily insight into vendors and their vendors through Bitsight Continuous Monitoring.
Supply chain visibility
Fourth-party dependencies and concentration risk mapped from Bitsight's supply chain dataset.
Supplier participation
Pre-populated profiles from a vendor network of more than 75,000 companies speed up onboarding.
Key consideration
Strongest where the priority is external data at scale, with supplier context coming through the separate assessment workflow.
Black Kite
Security ratings
Black Kite comparison
Best for
Outside-in risk intelligence with ransomware susceptibility and financial impact scoring
Primary approach
Non-intrusive cyber ratings built from open-source intelligence and translated into standardised risk assessments.
Supplier evidence
AI automates vendor assessments, questionnaires and gap analysis alongside external findings.
Monitoring
Continuous monitoring, with FocusTags linking a specific threat to the suppliers exposed to it.
Supply chain visibility
Exposure and high-risk signals traced across the supplier ecosystem out to nth parties.
Supplier participation
Supplier outreach runs through Black Kite Bridge, used alongside FocusTags when responding to disruptive events.
Key consideration
Includes cyber risk quantification, which helps where the board wants third-party exposure expressed in financial terms.
Mitratech Prevalent
Vendor risk workflow
Mitratech Prevalent comparison
Best for
Configurable assessment workflows, with managed services to take on the work
Primary approach
Standardised and custom questionnaires across the third-party lifecycle, correlated with external threat data.
Supplier evidence
Assessment responses and evidence, plus on-demand access to completed, standardised risk reports through vendor intelligence networks.
Monitoring
Continuous cyber and business monitoring integrated with assessment results.
Supply chain visibility
Relationship mapping to identify connections beyond direct vendors.
Supplier participation
Vendors complete assessments in the platform, and managed services can run onboarding, assessments and remediation tracking on your behalf.
Key consideration
Now part of Mitratech's wider legal, risk and compliance portfolio following the 2024 acquisition.
ProcessUnity
Vendor risk workflow
ProcessUnity comparison
Best for
Highly configurable enterprise TPRM programmes
Primary approach
No-code configurable workflows combined with a third-party risk data exchange and AI.
Supplier evidence
Configurable assessments, plus completed assessments available through the Global Risk Exchange, which absorbed CyberGRX in 2023.
Monitoring
Vendor monitoring tools tied to the assessment engine, supporting due diligence after the contract is signed.
Supply chain visibility
Fourth- and nth-party coverage built through assessments, contract requirements and programme automation.
Supplier participation
Suppliers can share completed exchange assessments rather than answering each customer from scratch.
Key consideration
Configurability suits mature programmes with dedicated resource to manage it.
OneTrust
Broad GRC suite
OneTrust comparison
Best for
Third-party risk inside a wider privacy, risk and compliance programme
Primary approach
A central vendor inventory and configurable assessment workflows inside the broader OneTrust platform.
Supplier evidence
Assessments mapped to the laws and frameworks you choose, with answers suppliers have shared through the Third-Party Risk Exchange.
Monitoring
Ratings from partners such as SecurityScorecard, Bitsight and RiskRecon can be linked to your inventory to trigger alerts or reassessments.
Supply chain visibility
Draws on connected ratings and data partners, so test how far the mapping goes for your critical suppliers.
Supplier participation
Suppliers can share assessment answers through the exchange with one click.
Key consideration
Fits best when third-party risk needs to sit alongside privacy, ethics and compliance in one system.
Risk Ledger
Supplier network
Risk Ledger comparison
Best for
Security-led teams that want suppliers to maintain one profile instead of answering every customer separately
Primary approach
Suppliers maintain one security profile with supporting evidence, and each connected customer reviews it against its own policies.
Supplier evidence
Control information and evidence maintained by the supplier, with each customer's policies overlaid to highlight what matters for that relationship.
Monitoring
Reassessment requests run automatically in the background, and customers are notified when an emerging threat affects suppliers in their network.
Supply chain visibility
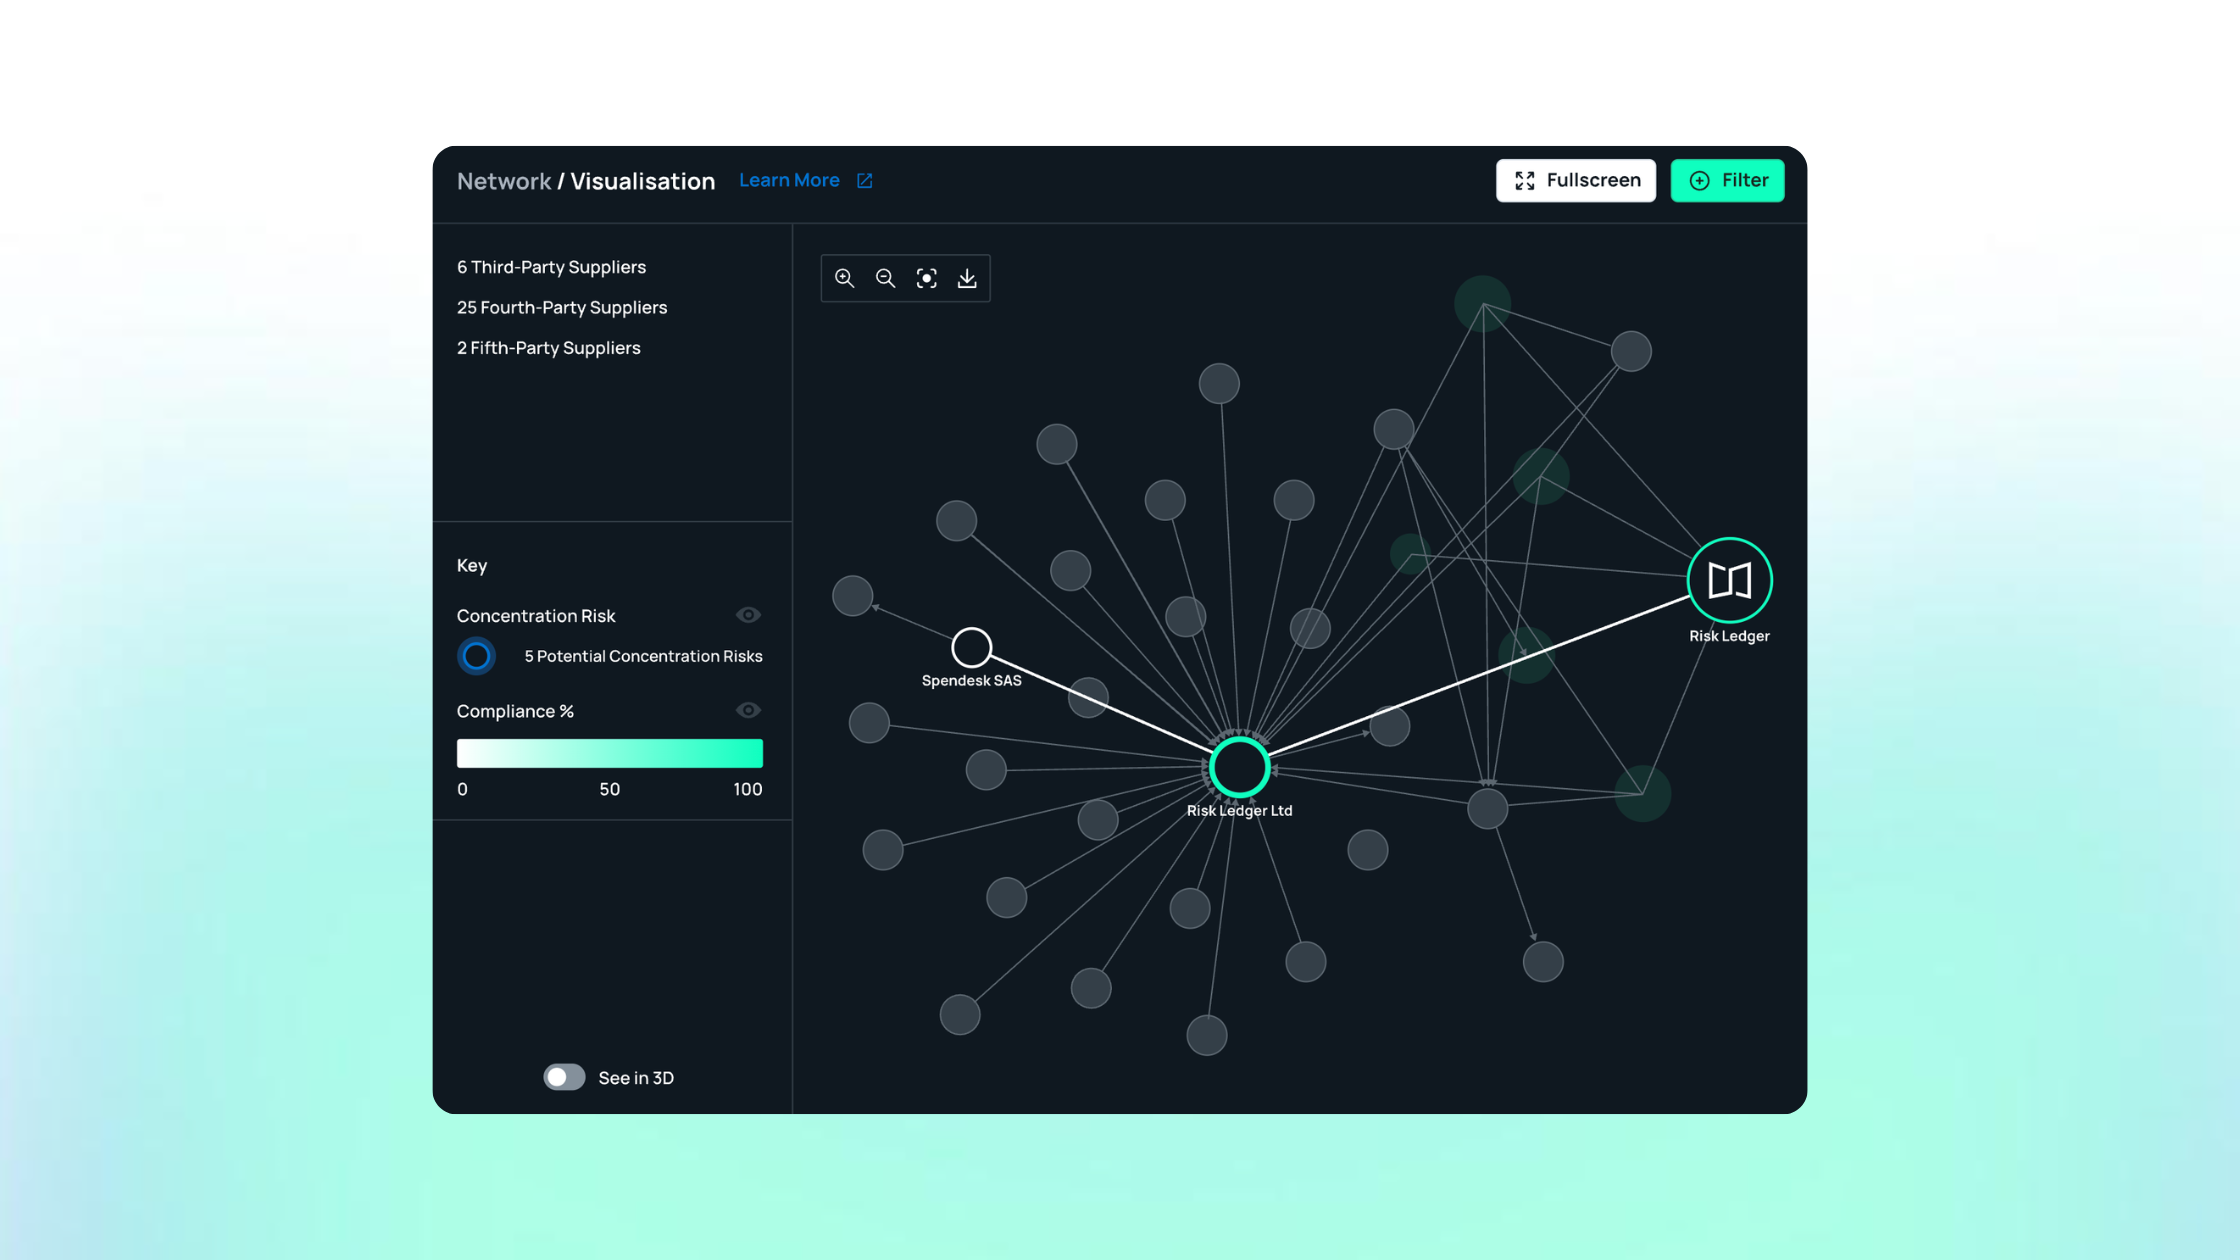
Suppliers declare their own dependencies, building a network map that shows concentration risk and shared providers at fourth and fifth party.
Supplier participation
Free for suppliers, who share one profile with as many customers as they choose.
Key consideration
The time saved depends on how many of your suppliers are already on the network, and it is not a broad GRC suite.
Practical test
Pick three of your critical suppliers and ask each shortlisted vendor to show, for those three only, where every row above comes from and when it was last updated.
Which Panorays alternative is closest on scanning, questionnaires and remediation?
UpGuard is the closest Panorays alternative on features, combining external scanning, questionnaires and remediation tracking in one product. But closest on features isn’t the same as fixing the problem. Like Panorays, UpGuard collects supplier evidence through questionnaires your team sends and chases, and so do SecurityScorecard, Bitsight and Black Kite.
SecurityScorecard, Bitsight and Black Kite now cover the same three jobs while leading with their ratings. Mitratech Prevalent and ProcessUnity come at it from the other direction, starting with the assessment and adding external data.
A like-for-like swap makes sense when your problem with Panorays is specific. If reporting is too rigid or role controls are too coarse, a platform with the same shape and a better version of that feature fixes it without moving suppliers onto a new process. It does less when the problem is workload.
Every platform above starts each assessment with a request from your team, and most offer suppliers some way to reuse answers to soften that. If most of your week goes on chasing responses, the useful comparison is how many of your current suppliers already have usable, current information on each platform, rather than how closely the feature lists match. That figure is specific to your supplier base, and no feature list will tell you what it is.
Teams who like having questionnaires and scanning in one place often ask us how Risk Ledger compares. We start from the other end. Suppliers maintain their own security profile and evidence, you connect to it and review it against your own policy, and changes they make reach you without a new questionnaire. External Monitoring complements that profile with scheduled scans of suppliers’ public domains, so you can review observed assets and findings alongside supplier-maintained evidence.
Panorays: questionnaires and scanning in one tool (the baseline)
Panorays is a third-party cyber risk platform that combines customisable security questionnaires with external attack-surface assessment, adding supply chain discovery and built-in DORA reporting. It’s the baseline for this comparison. Every alternative below either does more of one of these jobs, or approaches the work from a different starting point.
Strengths
Questionnaires and external scanning in one platform, the main reason teams choose it.
Questionnaire answers are checked against the supplier’s external documents and cyber posture, with gaps highlighted for review.
Supply chain discovery detects third to nth parties and flags concentration risk.
A one-click DORA Register of Information report, plus DORA questionnaires mapped to it.
Ease of use is the strength G2 reviewers mention most often.
Drawbacks
Assessments run relationship by relationship, so the work of sending, chasing and reviewing grows with every supplier you add.
The view beyond direct suppliers comes from discovery rather than dependencies suppliers declare, so check how discovered links map to the services you rely on.
Pricing isn’t published.
Best use case
Teams that want one combined tool, work mainly one to one with a modest supplier base, and need DORA reporting built in.
UpGuard: UpGuard: best for scanning, questionnaires and remediation in one tool
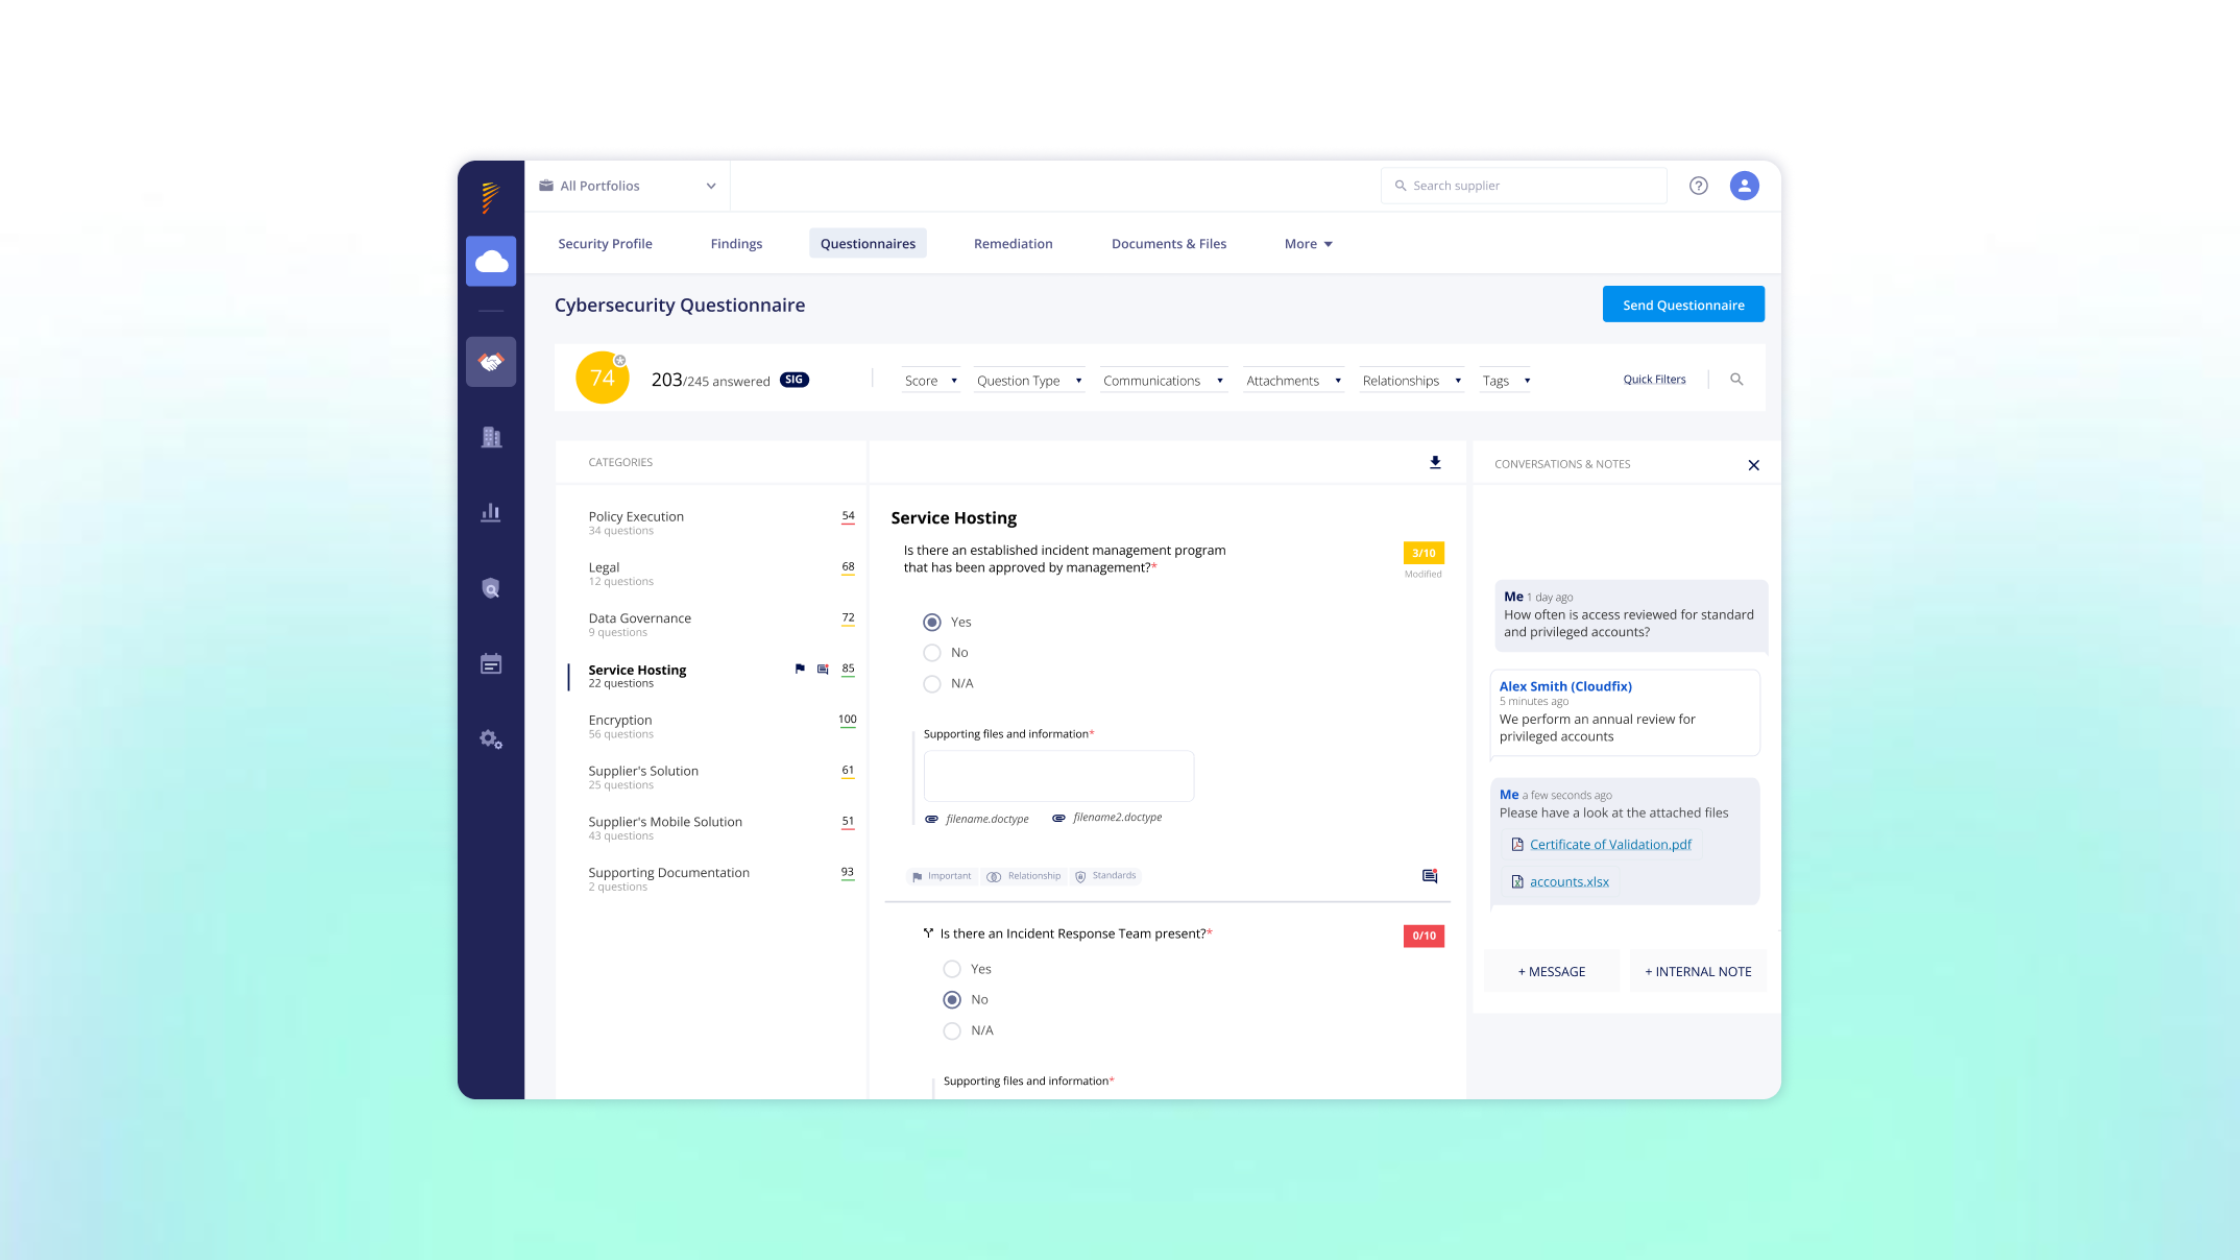
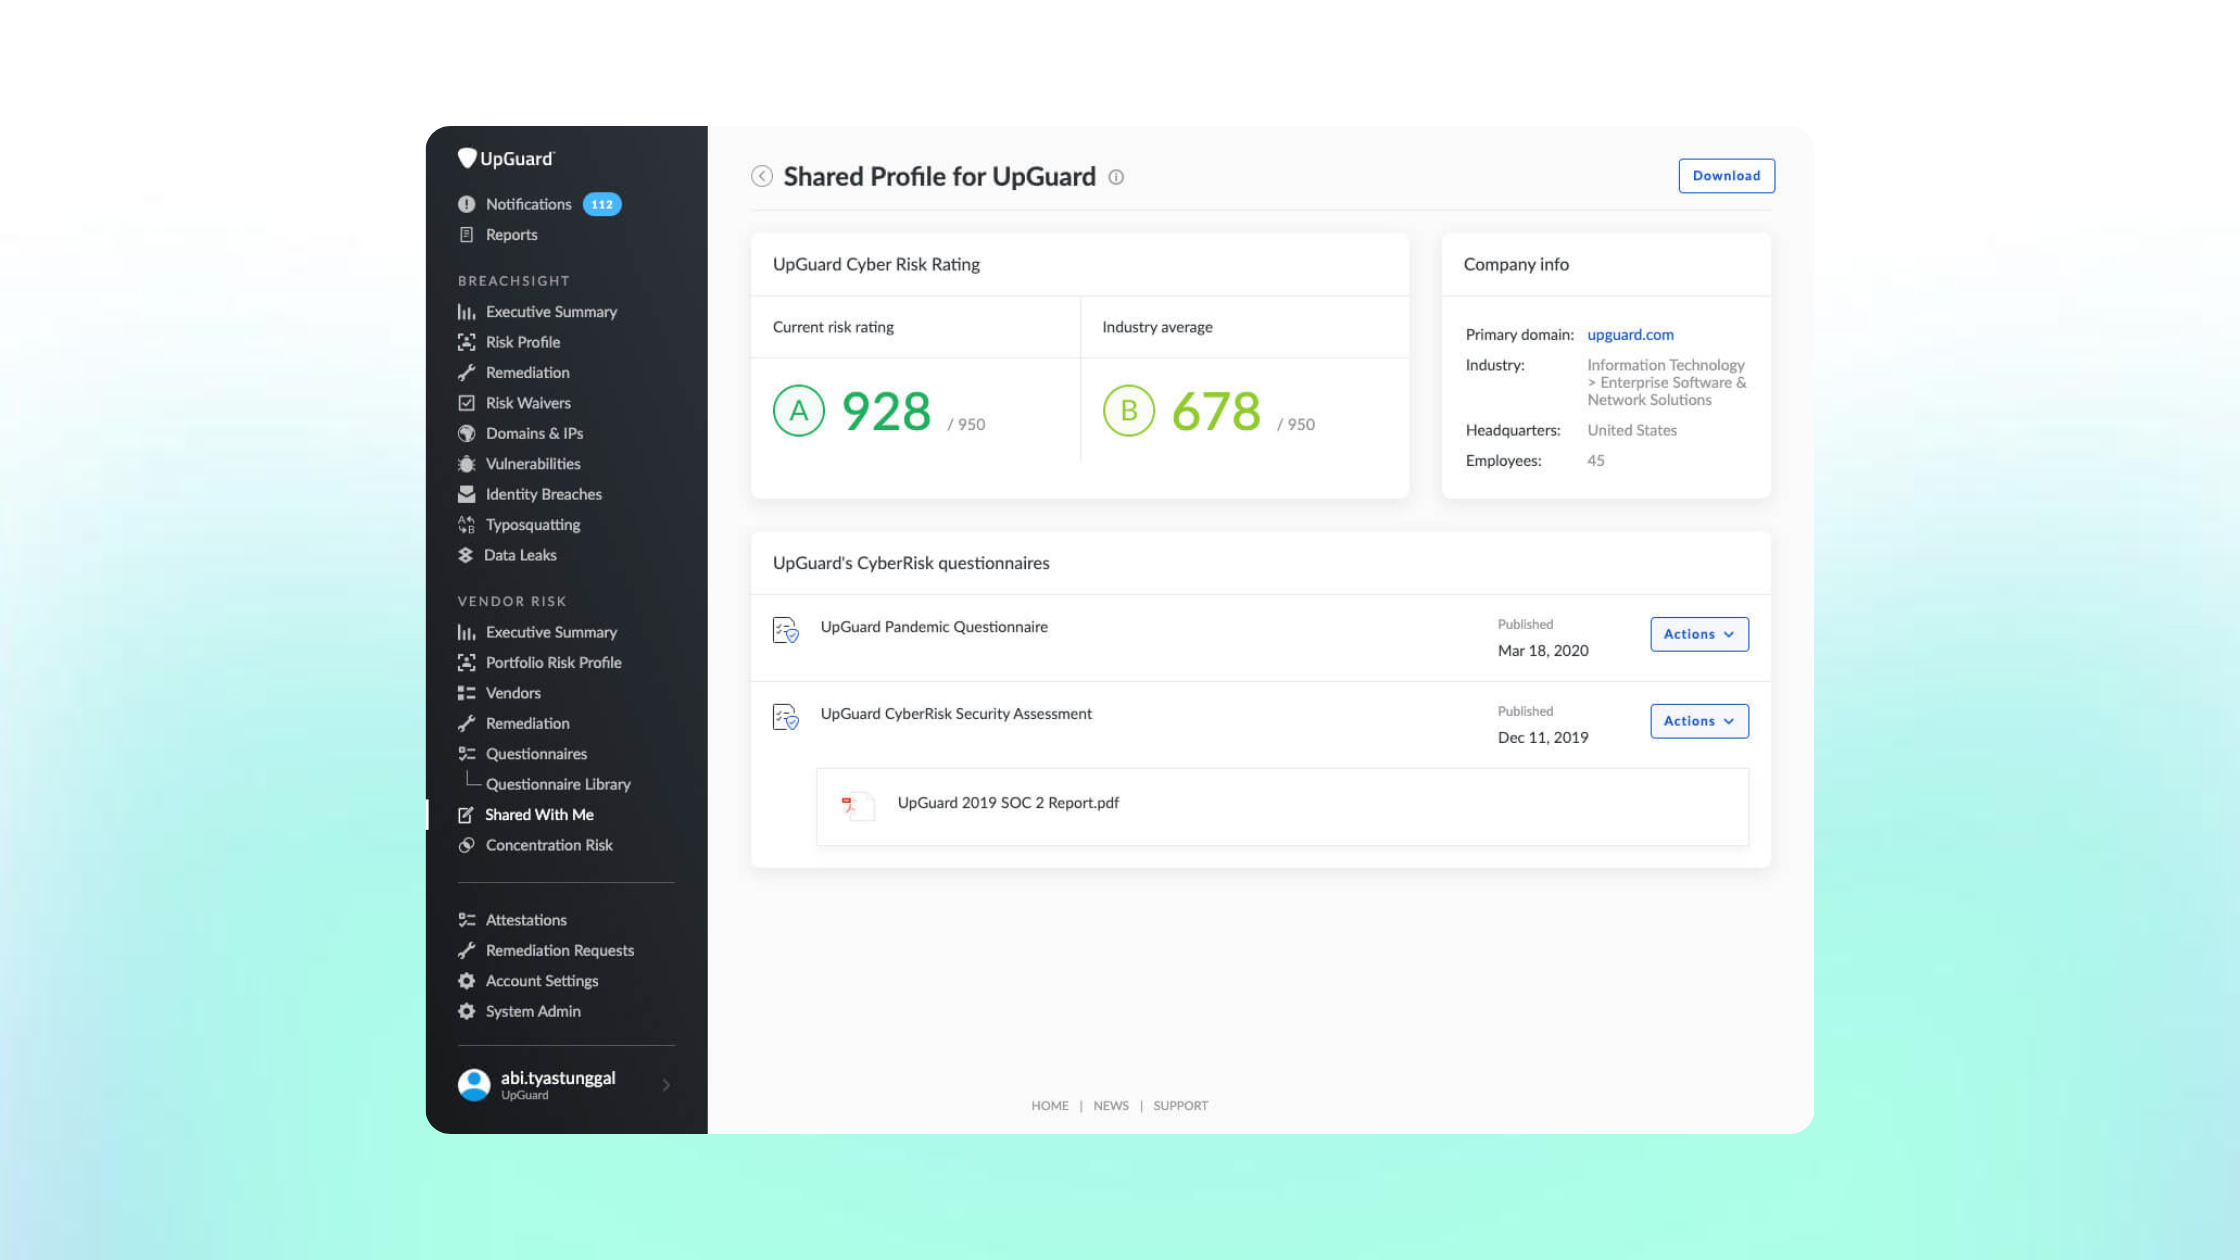
UpGuard is a vendor risk platform that pairs continuous external scanning with questionnaires and remediation workflows, which makes it the closest peer to Panorays on core features. The main differences are packaging and how suppliers respond. UpGuard publishes its entry pricing, and suppliers answer through a free Trust Exchange account that lets them reuse responses across requests.
Strengths
Ratings update multiple times a day from daily scanning.
Pre-built questionnaires cover frameworks including NIST, ISO and SIG.
Published entry pricing makes early cost comparison easier.
Suppliers get a free Trust Exchange account with response reuse and control over which customers see their information.
Drawbacks
Fourth-party risk is only included in the upper tiers.
Evidence collection still starts with a questionnaire your team sends, so chasing stays part of the workload.
Scan-based findings depend on assets being attributed to the right supplier, so test attribution against domains you know.
Best use case
Teams that want a like-for-like replacement for Panorays with transparent entry pricing.
Panorays vs UpGuard
Panorays has two specific advantages: DORA Register of Information reporting built into the product, and supply chain discovery that reaches beyond fourth parties. UpGuard’s advantages are a published price list and ratings that refresh several times a day. Both build their fourth-party view through discovery rather than from dependencies suppliers declare, so if visibility beyond direct suppliers is part of why you’re switching, test that directly with both. See UpGuard alternatives compared for the wider picture.
SecurityScorecard: best for ratings combined with threat intelligence
SecurityScorecard is a security ratings platform that scores suppliers from outside-in signals and adds threat intelligence, questionnaire management and automated vendor response workflows. Compared with Panorays, it leads with the rating rather than the assessment. Fourth-party discovery and custom questionnaires sit in its Premium package, so the package you buy decides how close the two products are.
Strengths
A to F grades are easy to explain in board and insurance conversations.
Alerts trigger when a supplier’s score changes.
Suppliers can claim a free scorecard for their own domain and respond to questionnaires at no cost.
The Premium package adds automated vendor discovery and AI agents.
Drawbacks
The Core package excludes automated vendor discovery and custom questionnaires, and SecurityScorecard positions it for programmes based on point-in-time assessments.
Pricing is on quote beyond the free plan.
Ratings infer risk from external signals, so findings still need supplier context before you can act on them.
Best use case
Teams that want ratings-led monitoring with threat intelligence, particularly where scores feed board or insurance reporting.
Panorays vs SecurityScorecard
Panorays weights the questionnaire and the scan equally. SecurityScorecard starts from the rating and adds questionnaires around it. If fourth-party discovery is a reason you chose Panorays, compare it against SecurityScorecard’s Premium package, not Core. For the full ratings discussion, see SecurityScorecard alternatives in more depth.
Bitsight: best for portfolio-level ratings at scale
Bitsight is a security ratings platform that scores organisations daily from external data and adds a vendor risk management module for assessments. Compared with Panorays, its strength is the size of its dataset. Bitsight monitors more than 40 million companies and offers pre-populated profiles from a vendor network of more than 75,000. Supplier context comes through its separate assessment workflow.
Strengths
Daily ratings cover a very large number of companies.
AI-assisted assessments are mapped to frameworks including SIG Lite, NIST CSF 2.0, ISO 27001 and HECVAT.
Bitsight AI can summarise SOC 2 reports.
Fourth-party dependencies and concentration risk are mapped from Bitsight’s supply chain data.
Drawbacks
Pricing isn’t published.
Evidence starts from what Bitsight observes externally, so a finding says little about how you use that supplier until you add the context yourself.
Fourth-party relationships come from external data, so check how they map to the services you actually depend on.
Best use case
Enterprises monitoring large supplier portfolios where external data at scale matters more than supplier-provided detail.
Panorays vs Bitsight
Both combine external monitoring with assessments. Bitsight brings a far larger monitored dataset and a pre-populated vendor network, while Panorays gives the questionnaire equal weight and builds DORA reporting into the product. See Bitsight alternatives for more on ratings platforms.
Black Kite: best for risk intelligence out to nth parties
Black Kite is a third-party cyber risk intelligence platform that builds non-intrusive ratings from open-source intelligence and adds ransomware susceptibility scoring and financial risk quantification. Compared with Panorays, it puts more weight on threat intelligence and less on the questionnaire, though it now uses AI to automate assessments and gap analysis. Both trace exposure beyond direct suppliers.
Strengths
The Ransomware Susceptibility Index, Adversary Susceptibility Index and Data Breach Index each score a specific type of threat.
FocusTags connect a particular threat or vulnerability to the suppliers exposed to it.
Cyber risk quantification using Open FAIR expresses exposure in financial terms.
AI automates vendor assessments, questionnaires and gap analysis.
Drawbacks
Pricing is tiered by vendor count, with add-on modules for extended functionality.
Findings come from non-intrusive external sources, so they need supplier confirmation before they support a risk decision.
The nth-party view is built from external signals rather than dependencies suppliers declare.
Best use case
Teams that need to answer “which of our suppliers is exposed to this threat?” quickly, and report that exposure in financial terms.
Panorays vs Black Kite
Both see beyond direct suppliers using discovery. Black Kite goes further on threat intelligence and financial quantification, while Panorays gives more weight to the supplier questionnaire and includes DORA reporting.
Mitratech Prevalent: best for configurable workflows with managed services
Mitratech Prevalent is a third-party risk management platform built around standardised and custom assessments, correlated with external threat data and backed by managed services. Compared with Panorays, it starts from the questionnaire and adds monitoring, where Panorays treats scanning and questionnaires as equal parts of one workflow. Mitratech acquired Prevalent in October 2024.
Strengths
Standardised and custom questionnaires cover the full third-party lifecycle, from onboarding to offboarding.
Vendor intelligence networks give on-demand access to completed, standardised risk reports on thousands of companies.
Managed services can take on onboarding, assessments and remediation tracking, and teams can move between managed and self-run.
Relationship mapping identifies connections beyond direct vendors.
Drawbacks
Assessments still begin with a request to the supplier, so chasing remains part of a self-run programme.
A completed report from the intelligence network reflects the supplier at the time it was finished, so check its date before relying on it.
Product direction now sits within Mitratech’s wider legal, risk and compliance portfolio, so teams that only need security assurance should check what they’ll actually use.
Best use case
Teams that want configurable assessment workflows and the option to outsource some of the assessment work.
Panorays vs Prevalent
Choose Panorays if you want scanning and questionnaires weighted equally in one tool. Choose Mitratech Prevalent if questionnaire depth and managed assessment support matter more to you than outside-in scanning. If you’re looking for alternatives to Prevalent itself, see Prevalent alternatives.
ProcessUnity: best for configurable enterprise TPRM, including CyberGRX
ProcessUnity is a third-party risk management platform that combines no-code configurable workflows with a third-party risk data exchange and AI. Compared with Panorays, it’s built for programmes that need to model complex policies and processes, rather than run a standard workflow of assessments and scans. ProcessUnity merged CyberGRX into its platform in July 2023.
Strengths
No-code configuration adapts workflows to complex regulatory and policy requirements.
The library covers more than 250 frameworks, regulations and standards, and more than 1,000 controls.
The Global Risk Exchange, which absorbed CyberGRX, gives access to completed assessments before you send your own. At the time of the merger, it held more than 14,000 attested and validated assessments.
Vendor monitoring supports due diligence after the contract is signed.
Drawbacks
Configurability takes planning and dedicated resource to manage well.
Exchange assessments reflect the supplier at the point they were completed, so check how current each one is.
Public material describes fourth- and nth-party management through assessments and contract requirements, so ask to see how dependencies are mapped in practice.
Best use case
Mature enterprise programmes with the resource to run a highly configurable system.
Panorays vs CyberGRX
CyberGRX is now part of ProcessUnity, so this is really a comparison with ProcessUnity. Panorays gives you scanning and questionnaires in a ready-made workflow. ProcessUnity gives you an exchange of completed assessments and far more room to configure, which also means more administration.
OneTrust: best for third-party risk inside a broad GRC programme
OneTrust is a governance, risk and compliance platform whose Third-Party Management module places vendor risk inside a wider privacy, ethics and compliance programme. Compared with Panorays, it’s built for breadth across risk domains rather than depth in supplier security. For external monitoring, it draws on ratings from partners such as SecurityScorecard, Bitsight and RiskRecon rather than leading with scanning of its own.
Strengths
A central vendor inventory sits alongside privacy, compliance and enterprise risk in one system.
Assessments map to the laws, standards and frameworks you choose, from a library covering hundreds.
Suppliers can share assessment answers with one click through the Third-Party Risk Exchange.
Partner ratings linked to your inventory can trigger alerts and reassessments automatically.
Drawbacks
The platform’s breadth adds setup and administration for teams that only need supplier security assurance.
External monitoring depends on connected partners, so check whether those ratings are included in your agreement.
Visibility beyond direct suppliers depends on the partner data you connect, so test how far it reaches for your critical suppliers.
Best use case
Organisations that want third-party risk managed in the same system as privacy, compliance and enterprise risk.
Panorays vs OneTrust
Choose Panorays if supplier security is the job and you want scanning and questionnaires built in. Choose OneTrust if third-party risk has to sit inside a wider GRC programme, and you’re comfortable bringing external ratings in from partners. See OneTrust alternatives for a wider comparison.
Risk Ledger: best for security-led supplier assurance and supply chain visibility
Risk Ledger is a supplier assurance platform built around a connected network, where each supplier maintains one security profile that every connected customer reviews against its own policies. Compared with the other platforms here, evidence starts with the supplier rather than with a questionnaire or a scan. Suppliers also declare their own dependencies, which builds visibility beyond direct suppliers across the network.
Strengths
Free for suppliers, who share one profile with as many customers as they choose.
Each customer overlays its own policies, so the same evidence is judged against your requirements for that relationship.
Discussions and formal remediation requests happen with the supplier’s security team in the platform.
Reassessment requests run in the background, and customers are notified when an emerging threat affects suppliers in their network.
Supplier-declared dependencies build a network map showing concentration risk and shared providers at fourth and fifth party.
Domain Review Agent flags gaps in supplier assessments and suggests next steps, with your team making the final decision.
Drawbacks
Being free for suppliers lowers the barrier, but it doesn’t guarantee a critical supplier will engage.
It isn’t a broad GRC suite for teams consolidating privacy, audit and enterprise risk.
The time saved depends on how many of your suppliers are already on the network. Suppliers new to it need to complete a profile first.
Best use case
Security-led teams that spend too much time collecting the same evidence, and want visibility into the providers their suppliers depend on.
Risk Ledger vs Panorays: one-to-one assessments or a supplier network
Risk Ledger and Panorays start from different places. Panorays sends each supplier a questionnaire and scans its external attack surface, relationship by relationship. Risk Ledger connects you to a security profile the supplier already maintains, which you review against your own policies. That means less repeated collection, evidence that stays current between reviews, and visibility of the providers your suppliers depend on.
Risk Ledger vs Panorays
How the two models handle each stage of supplier assurance
Based on Panorays' own product pages and Risk Ledger's platform, checked on 27 October 2026.
PanoraysOne-to-one assessments and scanning
VS
Risk LedgerSupplier network with maintained profiles
Risk Ledger and Panorays compared across six stages of supplier assurance
Stage
Panorays
Risk Ledger
Starting point
A questionnaire your team sends to each supplier, alongside a scan of its external attack surface.
A security profile the supplier already maintains, which you connect to.
Adding a supplier assessed by someone else
A new questionnaire for your relationship, though the supplier may share a Security Passport self-assessment.
A connection request to the existing profile, with no new assessment to start from scratch.
Judging the evidence
Answers checked against the supplier's external documents and cyber posture, with gaps highlighted.
Your policies overlaid on the supplier's controls and evidence, so gaps reflect your requirements for that relationship.
Fixing gaps
Responses turned into tasks with due dates, reminders and in-app chat.
Discussions and formal remediation requests with the supplier's security team, ending in your approval decision.
Keeping it current
Continuous monitoring of each supplier's external security posture.
Reassessment requests in the background, and profile updates visible to every connected customer.
Seeing beyond direct suppliers
Supply chain discovery of third to nth parties, with concentration risk flagged.
Dependencies declared by suppliers across the network, mapped at fourth and fifth party.
Practical test
Take five suppliers you assessed last year. Ask each platform how many already have current, usable information, and what your team would have to do to get the rest to a decision.
A shared profile changes who collects the evidence, it doesn’t change who owns the decision.
One public sector security lead put the worry plainly to us: “the second I share my validation, I’m accepting that risk”. On Risk Ledger, the supplier’s profile is the same for every customer, but the judgement isn’t. Your policies sit on top of it, so a control that’s acceptable for a low-risk supplier can show as a gap for one that handles your customer data. You decide what’s acceptable, record the decision and raise remediation where you need it. What you stop doing is collecting the same answers again for each supplier. We built the platform around that trade, so less of your team’s time goes on gathering information and more goes on the judgement only your team can make.
Where Risk Ledger is clearly ahead is in what happens after the first assessment. When a supplier is already on the network, adding them is a connection request rather than a new questionnaire, so your team starts from evidence instead of a blank form. When that supplier updates a control, the change reaches every connected customer without anyone sending a reassessment. Because suppliers declare their own dependencies, the network shows relationships that external discovery can miss, such as an outsourced service provider with no visible link to the supplier’s domains. That’s how you find out that three of your critical suppliers rely on the same provider. Panorays has the edge if built-in attack-surface scanning or a ready-made DORA Register of Information report is a hard requirement. If either is, make it part of your evaluation and ask us to show how we’d cover it.
The network saves the most where your suppliers are already on it, and the pull often comes from suppliers themselves. A UK construction group we spoke to was revisiting the market after years with one provider. Part of the reason was that its own suppliers were asking to share their security information through Risk Ledger instead of completing another portal. If you’re mid-contract, we can run alongside Panorays on a sample of your suppliers, so you can compare the two on real relationships before renewal.
Where does the evidence come from?
Supplier security evidence comes from three sources. Some is observed from outside, through scans of internet-facing assets. Some is provided by the supplier, through questionnaires, documents and maintained profiles. Some is independently assessed, through certifications, audit reports and penetration tests. Each covers different ground and ages at a different rate, so the useful question is which combination a platform gives you and how current each part is.
Evidence sources
Where supplier security evidence comes from
Most platforms combine more than one source. What matters is what each covers and how quickly it goes out of date.
Observed from outside
Open ports
Certificates
Email security
Leaked credentials
What it shows
Internet-facing security hygiene, gathered without any effort from the supplier.
What it misses
Internal controls, processes and how the supplier delivers the service you rely on. Findings also depend on assets being attributed correctly.
How it ages
Refreshed continuously, but only for what is visible from outside.
Provided by the supplier
Questionnaire answers
Policies
Maintained profiles
Declared dependencies
What it shows
Internal controls, processes, the providers the supplier depends on and context only the supplier knows.
What it misses
Proof that a control works. A declaration needs supporting evidence before it carries weight.
How it ages
A completed questionnaire is frozen at submission. A maintained profile changes when the supplier changes it.
Independently assessed
ISO 27001
SOC 2 reports
Penetration tests
What it shows
A third party's verification of controls against a recognised standard.
What it misses
Anything outside the audit scope, which may not include the service you actually use.
How it ages
Tied to the audit period and certificate dates, so check both before relying on it.
Practical test
For any finding a platform shows you, ask three things. Who produced it, what does it cover, and when was it last true?
External scanning is the fastest of the three sources and needs nothing from the supplier, which is why it suits large portfolios. It’s also the narrowest. A scan sees what a supplier exposes to the internet, not how it controls access internally or how it would recover the service it provides to you. For more on where scanning fits, see the limits of external scanning evidence.
How much of the questionnaire work can AI do?
AI can take on most of the reading and drafting in a supplier assessment, but not the judgement. It can draft answers from existing documents, pull evidence out of long reports, summarise a supplier’s profile and flag where answers look thin. Deciding whether a control is adequate for your relationship, and accepting a risk, still need a person. So does checking an answer against how the supplier actually operates.
AI is already speeding up both sides of the questionnaire. Suppliers use autofill tools that draft answers from their policies and past responses, and UpGuard reports that 39% of questionnaires completed with its autofill are submitted within two days, against a typical three weeks. Customers use AI to read those answers back and summarise them.
That makes the process faster, but it raises a harder question. When AI fills in the questionnaire on one side and reads it on the other, what evidence still counts? An answer drafted from the same policy documents the supplier sent last year isn’t new information, however quickly it arrives. What still carries weight is evidence that can be traced to a source, is dated, and is specific to the service you use. A reviewer also has to have actually looked at it. Speed helps most when it frees time for that review rather than replacing it.
Where AI helps most
Drafting answers from a supplier’s existing policies and past responses.
Extracting evidence from long documents such as SOC 2 reports.
Summarising a supplier’s profile so a reviewer knows where to look first.
Flagging answers that are missing, contradictory or unsupported.
Where a person still decides
Whether a control is good enough for this supplier and this service.
Whether to accept, remediate or escalate a risk.
Whether an answer matches how the supplier actually works.
We built our AI around that split. Smart Assessment Reviews gives reviewers a short summary of a supplier’s profile, so they know where to look before they open the full assessment. Domain Review Agent flags gaps, explains why they matter and suggests next steps. Every output traces back to the supplier information it came from, and the decision stays with your team. AI summaries can still be wrong, which is why traceability matters more than speed.
What “continuous” should actually mean
In supplier assurance, “continuous” should mean three things stay current: the signals you see about a supplier, the evidence behind its answers, and your own decision about whether the risk is acceptable. Most platforms keep one of these fresh automatically. Ask which one, how quickly, and what still needs someone on your team to act.
Each of the three needs its own definition before it can be tested.
Signal freshness is how recently a finding about the supplier was updated. An external scan that refreshes daily is fresh on signals.
Evidence freshness is when the supporting document was issued and what period it covers. A SOC 2 report whose audit period ended eleven months ago is stale on evidence, however recently it was uploaded.
Decision freshness is whether your team has reconsidered its judgement since something material changed. A supplier approved last spring that has since moved its hosting provider is stale on decision, even if every signal and document is up to date.
A platform can be continuous on signals and still leave every decision a year old. That’s the pattern behind most “continuous monitoring” claims. Scores refresh daily, alerts fire when they move, and the approval behind each supplier still dates from the original assessment, because nothing connects the change to a review. The reverse also happens. A team re-reviews every supplier on schedule, but works from evidence that hasn’t been refreshed since the last cycle. When you evaluate a platform, ask it to show four things on a real supplier. Does it detect an external change? Does it tell you when the supplier updates an answer? Does it flag evidence that is about to expire? Does it trigger a review when any of these happens? Then ask how quickly each one happens, and which steps still depend on a person noticing.
We built Risk Ledger to keep evidence current at the source. Suppliers maintain their own profile, so when they change a control, the update reaches every connected customer without a new questionnaire. Reassessment requests run in the background, and when an emerging threat affects suppliers in your network, we tell you which ones so you can review them. Your decision is still yours to revisit. What changes is that you hear when something has moved.
Which tools show who your suppliers depend on?
Most platforms build their view beyond direct suppliers through discovery, inferring fourth parties from external data. Panorays, UpGuard, SecurityScorecard, Bitsight and Black Kite all do this, often in higher pricing tiers. Risk Ledger uses dependencies that suppliers declare themselves. Discovered links need nothing from the supplier, and declared links can include services with no visible technical footprint.
The MOVEit breach in 2023 shows why the distinction matters. Attackers exploited a vulnerability in MOVEit Transfer, a file transfer tool made by Progress Software. One organisation using it was Zellis, a UK payroll provider, and staff data at British Airways, the BBC and Boots was exposed as a result. British Airways described the incident as occurring via one of Zellis’s own third-party suppliers. For those organisations, MOVEit was a fourth party. Each had a direct relationship with Zellis, but the exposure came from a supplier’s supplier that a standard third-party review would not have named. Zellis used its MOVEit instance to exchange files with dozens of companies, so the same weakness reached many customers at once. The question security teams were left asking was which of their suppliers used MOVEit, and for what. That’s the question a fourth-party view has to answer in hours rather than weeks.
Fourth-party visibility
Three suppliers, one shared provider
Each supplier can pass its own assessment while all three depend on the same provider. The questions underneath decide whether that matters.
Illustrative example
You
Your organisation
Third parties: your direct suppliers
Payroll provider
Assessed and approved
HR platform
Assessed and approved
Benefits administrator
Assessed and approved
Fourth party: shared by all three
File transfer software
Not named in any of the three assessments
1How is the link known? Discovered from external data, or declared by the supplier.
2When was it confirmed? A link that was true last year may not be true now.
3What does it support? Whether it touches the service you rely on, or something unrelated.
4What is still unknown? Gaps and confidence levels are part of a useful answer.
Practical test
Ask each platform to show the path from one of your suppliers to a provider it depends on. What establishes that relationship, when was it confirmed, and what would you still need to investigate?
Finding a shared provider is a starting point. If three of your critical suppliers use the same provider, the next questions are what each uses it for, whether it supports the services you depend on, and what recovery arrangements exist if it fails. A shared provider only becomes a shared point of failure when those answers line up badly.
Discovered and declared links have different blind spots. Discovery sees technical relationships visible from outside, such as hosting, email and DNS providers, without asking the supplier anything. It can’t see a service with no external footprint, though, and it can attribute assets to the wrong organisation. Declared links can cover any provider a supplier names, outsourced services included. But they’re only as complete and accurate as the supplier makes them. One buyer told us they were sceptical of mapping that relies on suppliers’ own declarations, and it’s a fair concern.
On Risk Ledger, suppliers declare the providers they depend on as part of their profile. Because each organisation on the network has one profile, those declarations join up into a map showing where several of your suppliers rely on the same provider, at fourth and fifth party. When an emerging threat hits a provider, we tell you which of your suppliers depend on it. We did this during MOVEit, helping customers identify which suppliers were exposed.
Most Panorays alternatives price on quote, so headline figures are hard to compare. The bigger differences are what the core quote includes, and how much of your team’s time each platform still needs for every supplier. Visibility beyond direct suppliers, for example, sits outside the entry packages of some ratings platforms.
Check what the quote covers before comparing it
Tier-gating is where like-for-like quotes come apart. Fourth-party risk sits in UpGuard’s upper tiers and in SecurityScorecard’s Premium package, not in their entry offers. If seeing beyond direct suppliers is part of why you chose Panorays, a lower quote from an alternative may not include it. Before comparing any two proposals, line up the same items in each: suppliers covered, users, fourth-party visibility, custom questionnaires and integrations. Ask every vendor, us included, which of these are in the core price and which are add-ons.
Count the team time, not just the licence
Every platform that collects evidence relationship by relationship carries a workload for each supplier. Someone has to send the assessment, chase it, review it and repeat it at reassessment. A cheaper licence that leaves that workload untouched can cost more over a contract than one that removes part of it. You can estimate this without a vendor’s help. Multiply the number of suppliers you assess each year by the hours each one takes from request to decision, then by your team’s cost per hour. Then ask each vendor which of those hours its platform removes, rather than speeds up, and for which suppliers. On a network, the hours removed are the collection hours for suppliers who already maintain a profile. That makes the answer specific to your supplier base rather than a generic efficiency claim.
Check who pays on the supplier side
If suppliers face a cost or a limit to respond, some won’t, and the chasing lands back on your team. Several platforms offer suppliers a free way to respond or share information. Risk Ledger is free for suppliers, whichever customers they connect with.
Which alternatives fit UK public sector and regulated buyers?
For UK public sector and regulated buyers, the right alternative is the one that can evidence ongoing oversight of suppliers, not just a completed assessment at contract signature. The NCSC’s Cyber Assessment Framework expects you to know your supply chain, sub-contractors included. Financial services firms face new third-party register requirements from March 2027. Those expectations favour platforms that keep evidence current and show dependencies beyond direct suppliers.
The gap regulators are closing is the one buyers describe most often. One public sector security lead told us their supplier assurance “was really strong up until they signed the contract. And then we just walked away and forgot about it completely.” That pattern is now harder to defend. Version 4.0 of the CAF, published by the NCSC in August 2025, puts more emphasis on whether supply chain controls are effective rather than simply present. Its indicators of good practice for supply chain (A4.a) include knowing the extent of the supply chain behind your essential functions, sub-contractors included. Having elements subcontracted with little or no visibility of the sub-contractors sits on the “not achieved” side. The Cyber Security and Resilience Bill, at report stage in the House of Lords since 26 October 2026, would extend the NIS Regulations to managed service providers and data centres, bringing more of the supply chain into regulated scope. For a security team, the practical test is whether, months after approval, you can show what changed at a critical supplier and what you did about it.
Security owns the risk, but procurement often owns the supplier relationship. As another public sector lead put it, “two thirds of digital procurement happens outside of our area of responsibility”. Platforms that suppliers can join and maintain themselves make it easier for security teams to apply the same standard to suppliers procured elsewhere in the organisation, because the evidence doesn’t depend on security running every assessment.
Risk Ledger supports CAF assessments directly. Customers can assess suppliers against CAF, use supplier answers and supporting documents as evidence for supply chain contributing outcomes, and use the network map to show visibility of dependencies. Risk Ledger is also available to public sector buyers through G-Cloud 14 on the Digital Marketplace. If G-Cloud matters to your procurement route, check the Digital Marketplace listing for every platform you shortlist.
Regulatory checklist
What each requirement asks, and what to check in a platform
Status checked on 27 October 2026. Confirm scope for your organisation with your own compliance team.
NCSC Cyber Assessment Framework 4.0, Principle A4
In use
What it asks
That you know the extent of the supply chain supporting your essential functions, including sub-contractors, and manage the risks it creates.
Check in a platform
Can it show the sub-contractors behind your critical suppliers, and produce evidence against A4 for an assessor?
Cyber Security and Resilience Bill
Lords report stage
What it asks
As passed by the Commons, it extends the NIS Regulations to managed service providers, data centres and large load controllers.
Check in a platform
Can you identify which of your suppliers fall into the newly regulated categories, and evidence how you oversee them?
G-Cloud on the Digital Marketplace
Procurement route
What it means
Public sector bodies can buy listed cloud services through a pre-agreed framework rather than running a full tender.
Check in a platform
Search the Digital Marketplace for each shortlisted vendor before you plan your procurement route.
DORA (EU Digital Operational Resilience Act)
Applies since January 2025
What it asks
EU financial entities must keep a Register of Information on their ICT third-party arrangements. UK firms are affected if they have EU-regulated entities or serve them.
Check in a platform
Can it produce register data in the required format, and keep it current as arrangements change?
FCA PS26/2 and PRA PS7/26
From 18 March 2027
What it asks
A register of material third-party arrangements, submitted annually, with notification of new or significantly changed arrangements. Sub-contracting chains are in scope.
Check in a platform
Can it record the providers behind each material arrangement and tell you when something significant changes between submissions?
Financial services: DORA and the UK third-party register
UK financial services firms are dealing with two regimes. DORA, the EU Digital Operational Resilience Act, has applied to EU financial entities since 17 January 2025, and requires a Register of Information covering ICT third-party arrangements. It’s EU law, so a UK firm needs it if it has EU-regulated entities or serves them. Panorays builds a one-click DORA Register of Information report into its product, which matters if DORA applies to you.
For UK-regulated firms, the bigger change is closer to home. From 18 March 2027, FCA PS26/2 and the PRA’s PS7/26 require firms to keep a register of material third-party arrangements, submit it annually and notify the regulator of new or significantly changed arrangements. Materiality extends to sub-contracting chains, so a register built only from direct contracts may fall short. When you evaluate a platform, ask how it would help you identify which arrangements are material, record the providers behind them, and spot a significant change between annual submissions. Supplier-declared dependencies and profiles that update when suppliers change them are directly relevant to the last two.
Which alternative fits which team?
The right Panorays alternative depends on what your team is short of. Teams short of time for chasing suppliers get most from a supplier network. Teams that need signals across a large portfolio without supplier effort get most from a ratings platform. Teams running complex, multi-domain programmes get most from a configurable workflow tool or GRC suite.
Find your fit
If this sounds like your team
Statements in quotation marks are things security teams have said to us. The rest describe pains we hear often.
We all have to do our own due diligence and it's like, well. But why?
Look atRisk Ledger
Suppliers maintain one profile that each customer reviews against its own policies, so you stop collecting what someone else already has.
There are not three of me.
Look atRisk Ledger
Policies flag non-compliant controls automatically, so a small team reviews by exception instead of reading every answer.
Do we know who our suppliers depend on?
Look atRisk LedgerBlack Kite
Risk Ledger maps dependencies suppliers declare. Black Kite traces exposure from external data. Each sees links the other can miss.
A score per supplier, automatically, without bothering anyone.
Look atBitsightSecurityScorecard
Ratings need no supplier effort and scale to large portfolios. They infer risk, so plan how you'll confirm findings on critical suppliers.
We want questionnaires and scanning in one place
Look atUpGuardStay with Panorays
The closest like-for-like option. Worth it when the problem is a specific feature rather than the collection workload.
We want someone else to run the assessments
Look atMitratech Prevalent
Managed services can take on onboarding, assessments and remediation tracking, and you can move between managed and self-run.
Our policies differ across business units and regulators
Look atProcessUnity
No-code configuration models complex requirements, if you have the resource to administer it.
Third-party risk has to sit with privacy and compliance
Look atOneTrust
One system for vendor risk, privacy and enterprise risk, with external ratings brought in from partners.
Platform fit is based on each vendor's own documentation, checked on 27 October 2026.
Small teams feel the difference between these models most. A team of one or two people can’t run a full assessment for every supplier, so the useful question is which platform lets them review by exception. That means looking first at the suppliers and controls that fall short, and leaving the rest. On Risk Ledger, your policies are applied to each supplier’s profile automatically, so non-compliant controls are flagged before anyone opens the assessment. Supplier Summaries gives a short overview of where attention is needed. For a supplier already on the network, the work starts at the review rather than at the request. There is a limit. For a small team whose priority is triaging hundreds of suppliers it will never assess in depth, a ratings platform gives a faster first signal, because it needs nothing from the supplier at all. Many small teams end up using external signals to decide where to look, and assured evidence to decide what to accept.
Enterprise GRC programme or lightweight monitoring?
Most teams fall into one of three operating models. They differ in how much effort sits with your team, with the supplier and with the platform.
Lightweight monitoring suits large supplier portfolios where the first need is a signal. Ratings platforms such as Bitsight, SecurityScorecard, Black Kite and UpGuard give continuous outside-in scores with little setup and no supplier effort. Depth comes later, through a separate assessment step.
Assurance with less collection suits security-led teams that need assured evidence on their critical suppliers but can’t keep running one-to-one questionnaires. A supplier network such as Risk Ledger moves the collection work to a profile the supplier maintains, so your team’s time goes on review and remediation.
An enterprise GRC programme suits organisations where third-party risk must sit alongside privacy, compliance and enterprise risk, with configurable workflows across business units. OneTrust, ProcessUnity and Mitratech Prevalent fit here, at the cost of more configuration and administration.
Switching at renewal: test with your own suppliers
Plan a move away from Panorays at least one notice period before your renewal date, and test any alternative on your own suppliers rather than in a demo. Export your records first. Then run a short pilot on a representative sample, and judge it on how quickly you reach a decision you could defend, not on how many features you saw.
Start with the contract, not the shortlist: Check your notice period and renewal date, and work back from them. A pilot, a business case and procurement all need time, and a notice period missed by a week usually means another year. Confirm what data you can export and in what format, because that shapes how much history you carry across.
Export before you need it: Take your supplier list and tiering, completed assessments with their supporting evidence, the risk register including any accepted risks, remediation history, and the decision records showing who approved what and why. The last of these is the one teams most often lose, and the one an auditor is most likely to ask for after a switch.
Pilot plan
Seven tests to run on every shortlisted platform
Use the same suppliers for each platform, and agree what a good result looks like before you start.
Seven pilot tests for comparing third-party risk platforms, with what each tests and what to record
Test
What it shows
What to record
A supplier already on the platform
How much existing evidence you can use straight away.
Time until relevant evidence is shared and ready for review.
A supplier new to the platform
What onboarding asks of the supplier and of your team.
Supplier effort, elapsed onboarding time and how much chasing you did.
A slow or unwilling supplier
What the platform does when engagement fails.
How non-response is handled and which evidence gaps remain.
A material control gap
Whether a finding turns into action.
Time from identifying the gap to an agreed action with an owner.
A known shared dependency
How far the platform sees beyond direct suppliers.
Where the link came from, which services it touches and what is still unknown.
An evidence update
Whether change reaches the right person.
Whether the update reached the reviewer and prompted the right follow-up.
An audit handoff
Whether decisions can be defended later.
Whether a colleague can reconstruct the decision and its rationale without asking you.
Practical decision rule
Choose the platform that gets your sample to defensible decisions with the least combined effort, and that is honest about what it still doesn't know.
A pilot only tells you something if it uses suppliers that make the platform work hard. Pick a small sample that mirrors your real supplier base: one supplier that may already be on the platform, one that will need onboarding, one that has been slow or unwilling to engage, a critical supplier delivering several services, and two or three suppliers you know share a provider. Run the same sample through every shortlisted platform, and agree before you start what a good result looks like for each test. Record three things each time. How long did it take to reach evidence ready for review? How much effort did it take from your team and from the supplier? What remained unknown at the end? That last measure matters most and is the easiest to skip. A platform that produces a confident score quickly but hides what it doesn’t know will look better in a pilot than one that shows its gaps, and worse six months later.
Questions to ask every vendor, us included
Which capabilities in your proposal are in the core price, and which are add-ons or higher tiers?
What does a supplier have to do, and does it cost them anything?
What happens when a critical supplier doesn’t respond, and how is the remaining gap recorded?
How do your own policies change what a reviewer sees for each supplier?
How are disputed findings handled, and who resolves them?
Can historical decisions and evidence be migrated, and can you run alongside your current platform during the pilot?
You don’t have to finish your Panorays contract before testing us. We can run alongside it on a sample of your suppliers, so you can compare the two on real relationships before renewal. To see where you’d start, the Supplier Coverage Check matches your top suppliers against the Risk Ledger network and sends you a coverage report, without contacting any of your suppliers.
Why organisations choose Risk Ledger
Every platform in this comparison treats vendor risk as one-to-one: your team assesses a supplier, that supplier gets scored or scanned, then the process resets for the next supplier and the next customer who asks.
We built Risk Ledger around a different starting point: the same supplier is often being assessed by dozens of other companies at the same time, using slightly different questionnaires, for largely the same information.
A supplier builds one profile on Risk Ledger, once. That profile gets reused across every connected customer relationship instead of being rebuilt from scratch each time someone new asks. When a supplier fixes a flagged issue or updates their evidence, every client they're connected to sees that update, not just the one who happened to ask.
Suppliers also declare their own critical dependencies as part of that profile. That's what feeds nth-party visibility into the network map: dependencies you can see because the supplier told you about them, not because a scan guessed at them from public data.
The network structure surfaces one more thing individual assessments can't. If several of your suppliers all depend on the same underlying provider, or a security issue hits a widely-used supplier, the network view shows that exposure across your whole supply chain, not as scattered, disconnected findings.
We're not the right fit for every team. If your priority is consolidating privacy, audit and enterprise risk into one governance platform, a broader GRC suite will serve you better. Risk Ledger is best suited to teams that want suppliers to actively participate, evidence that doesn't need rebuilding for every customer, and visibility into risk that sits beyond the direct supplier relationship.
How we help teams moving on from Panorays
Teams that move from Panorays to Risk Ledger usually do it to stop collecting the same evidence one supplier at a time. They start instead from profiles suppliers already keep current, judged against their own policies, with a view of the providers those suppliers depend on.
We call the complete model Active Supply Chain Security. Suppliers maintain their own security evidence. Each customer reviews it against its own requirements and works through gaps with the supplier directly. Dependencies are declared across the network, so shared providers show up before an incident rather than during one. When a new threat emerges, you hear which of your suppliers are affected without sending a single questionnaire.
There are two ways to see whether it fits your supplier base.
Check your coverage: The Supplier Coverage Check shows how many of your top suppliers are already on the network.
Panorays' main competitors fall into four groups. Security ratings platforms include UpGuard, SecurityScorecard, Bitsight and Black Kite. Vendor risk workflow tools include Mitratech Prevalent and ProcessUnity. OneTrust places third-party risk inside a broad GRC suite. Risk Ledger is a supplier network, where suppliers maintain one security profile that each connected customer reviews against its own policies.
Which Panorays alternative is closest on features?
UpGuard is the closest Panorays alternative on features, combining external scanning, questionnaires and remediation tracking in one product. A like-for-like swap makes most sense when your problem with Panorays is a specific feature. If the problem is the time spent collecting and chasing supplier evidence, compare how many of your suppliers already have usable, current information on each platform.
Why do security teams switch from Panorays?
Most teams switch for operational reasons. Reviewers raise setup effort, limited reporting customisation, coarse role controls and an API that updates whole supplier records. In our conversations with teams reviewing Panorays, the larger theme is the workload of assessing every supplier relationship one to one, along with suppliers that don't respond and costs that rise at renewal.
How is Risk Ledger different from Panorays?
Panorays sends each supplier a questionnaire and scans its external attack surface, relationship by relationship. Risk Ledger connects you to a security profile the supplier already maintains, which you review against your own policies. When the supplier updates a control, every connected customer sees the change, and suppliers declare the providers they depend on, which shows shared dependencies across your supply chain.
Which Panorays alternatives show fourth-party and nth-party dependencies?
Panorays, UpGuard, SecurityScorecard, Bitsight and Black Kite all discover fourth parties from external data, and some include it only in higher tiers or packages. Risk Ledger uses dependencies that suppliers declare themselves. Discovered links need nothing from the supplier. Declared links can include services with no visible technical footprint, but depend on suppliers keeping them complete and accurate.
Does reviewing a supplier's shared profile mean accepting their risk?
No. A shared profile changes who collects the evidence, not who owns the decision. You review the supplier's controls and evidence against your own policies, decide what is acceptable for that relationship, and raise remediation where you need it. The same profile can be acceptable for a low-risk supplier and fall short for one that handles your customer data.
Do Panorays alternatives support DORA and UK third-party reporting rules?
Panorays includes a one-click DORA Register of Information report, which matters for EU-regulated financial entities. UK firms also face FCA PS26/2 and PRA PS7/26, which require a register of material third-party arrangements, including sub-contracting chains, from 18 March 2027. Ask each vendor to show how it would help you identify material arrangements and spot significant changes between submissions.
Can I test an alternative before my Panorays contract ends?
Yes. Start at least one notice period before your renewal date, and run a short pilot on a representative sample of your own suppliers. Include one that may already be on the platform, one that needs onboarding, one that is slow to respond and a critical supplier. Risk Ledger can run alongside Panorays during that pilot.