Almost 8000 organisations are already using Risk Ledger's cutting-edge platform for real-time supply chain security, which enables organisations to Defend-as-One because every link matters in cyber security.Visualising client-supplier networks, Risk Ledger is able to map interdependencies and risks well beyond organisations' immediate third-parties, into 4th, 5th and nth parties. This allows the uncovering of hidden concentration and systemic risks that could pose a threat to the cyber security and operational resilience of organisations and entire industries.
In our recent data snapshot, we identified key concentrations risks for our existing investment fund and private equity clients on our platform.Do you know which concentration risks might be hiding in your extended supply chains?
If you want to learn more about concentration risks, and how Risk Ledger helps organisations uncover and mitigate them, then download our free data snapshot report.
Resources
Data Insights Report
Uncovering Concentration Risks in the Supply Chains of Private Equity Funds: Data Snapshot
In Risk Ledger's latest data snapshot report, we reveal the concentration risks we discovered in the supply chains of our investment fund and private equity clients.

Data Insights Report
More articles

Blog
CISO Briefing: The Illusion of Assurance - Exposing the Hidden Control Gaps in Your Supply Chain
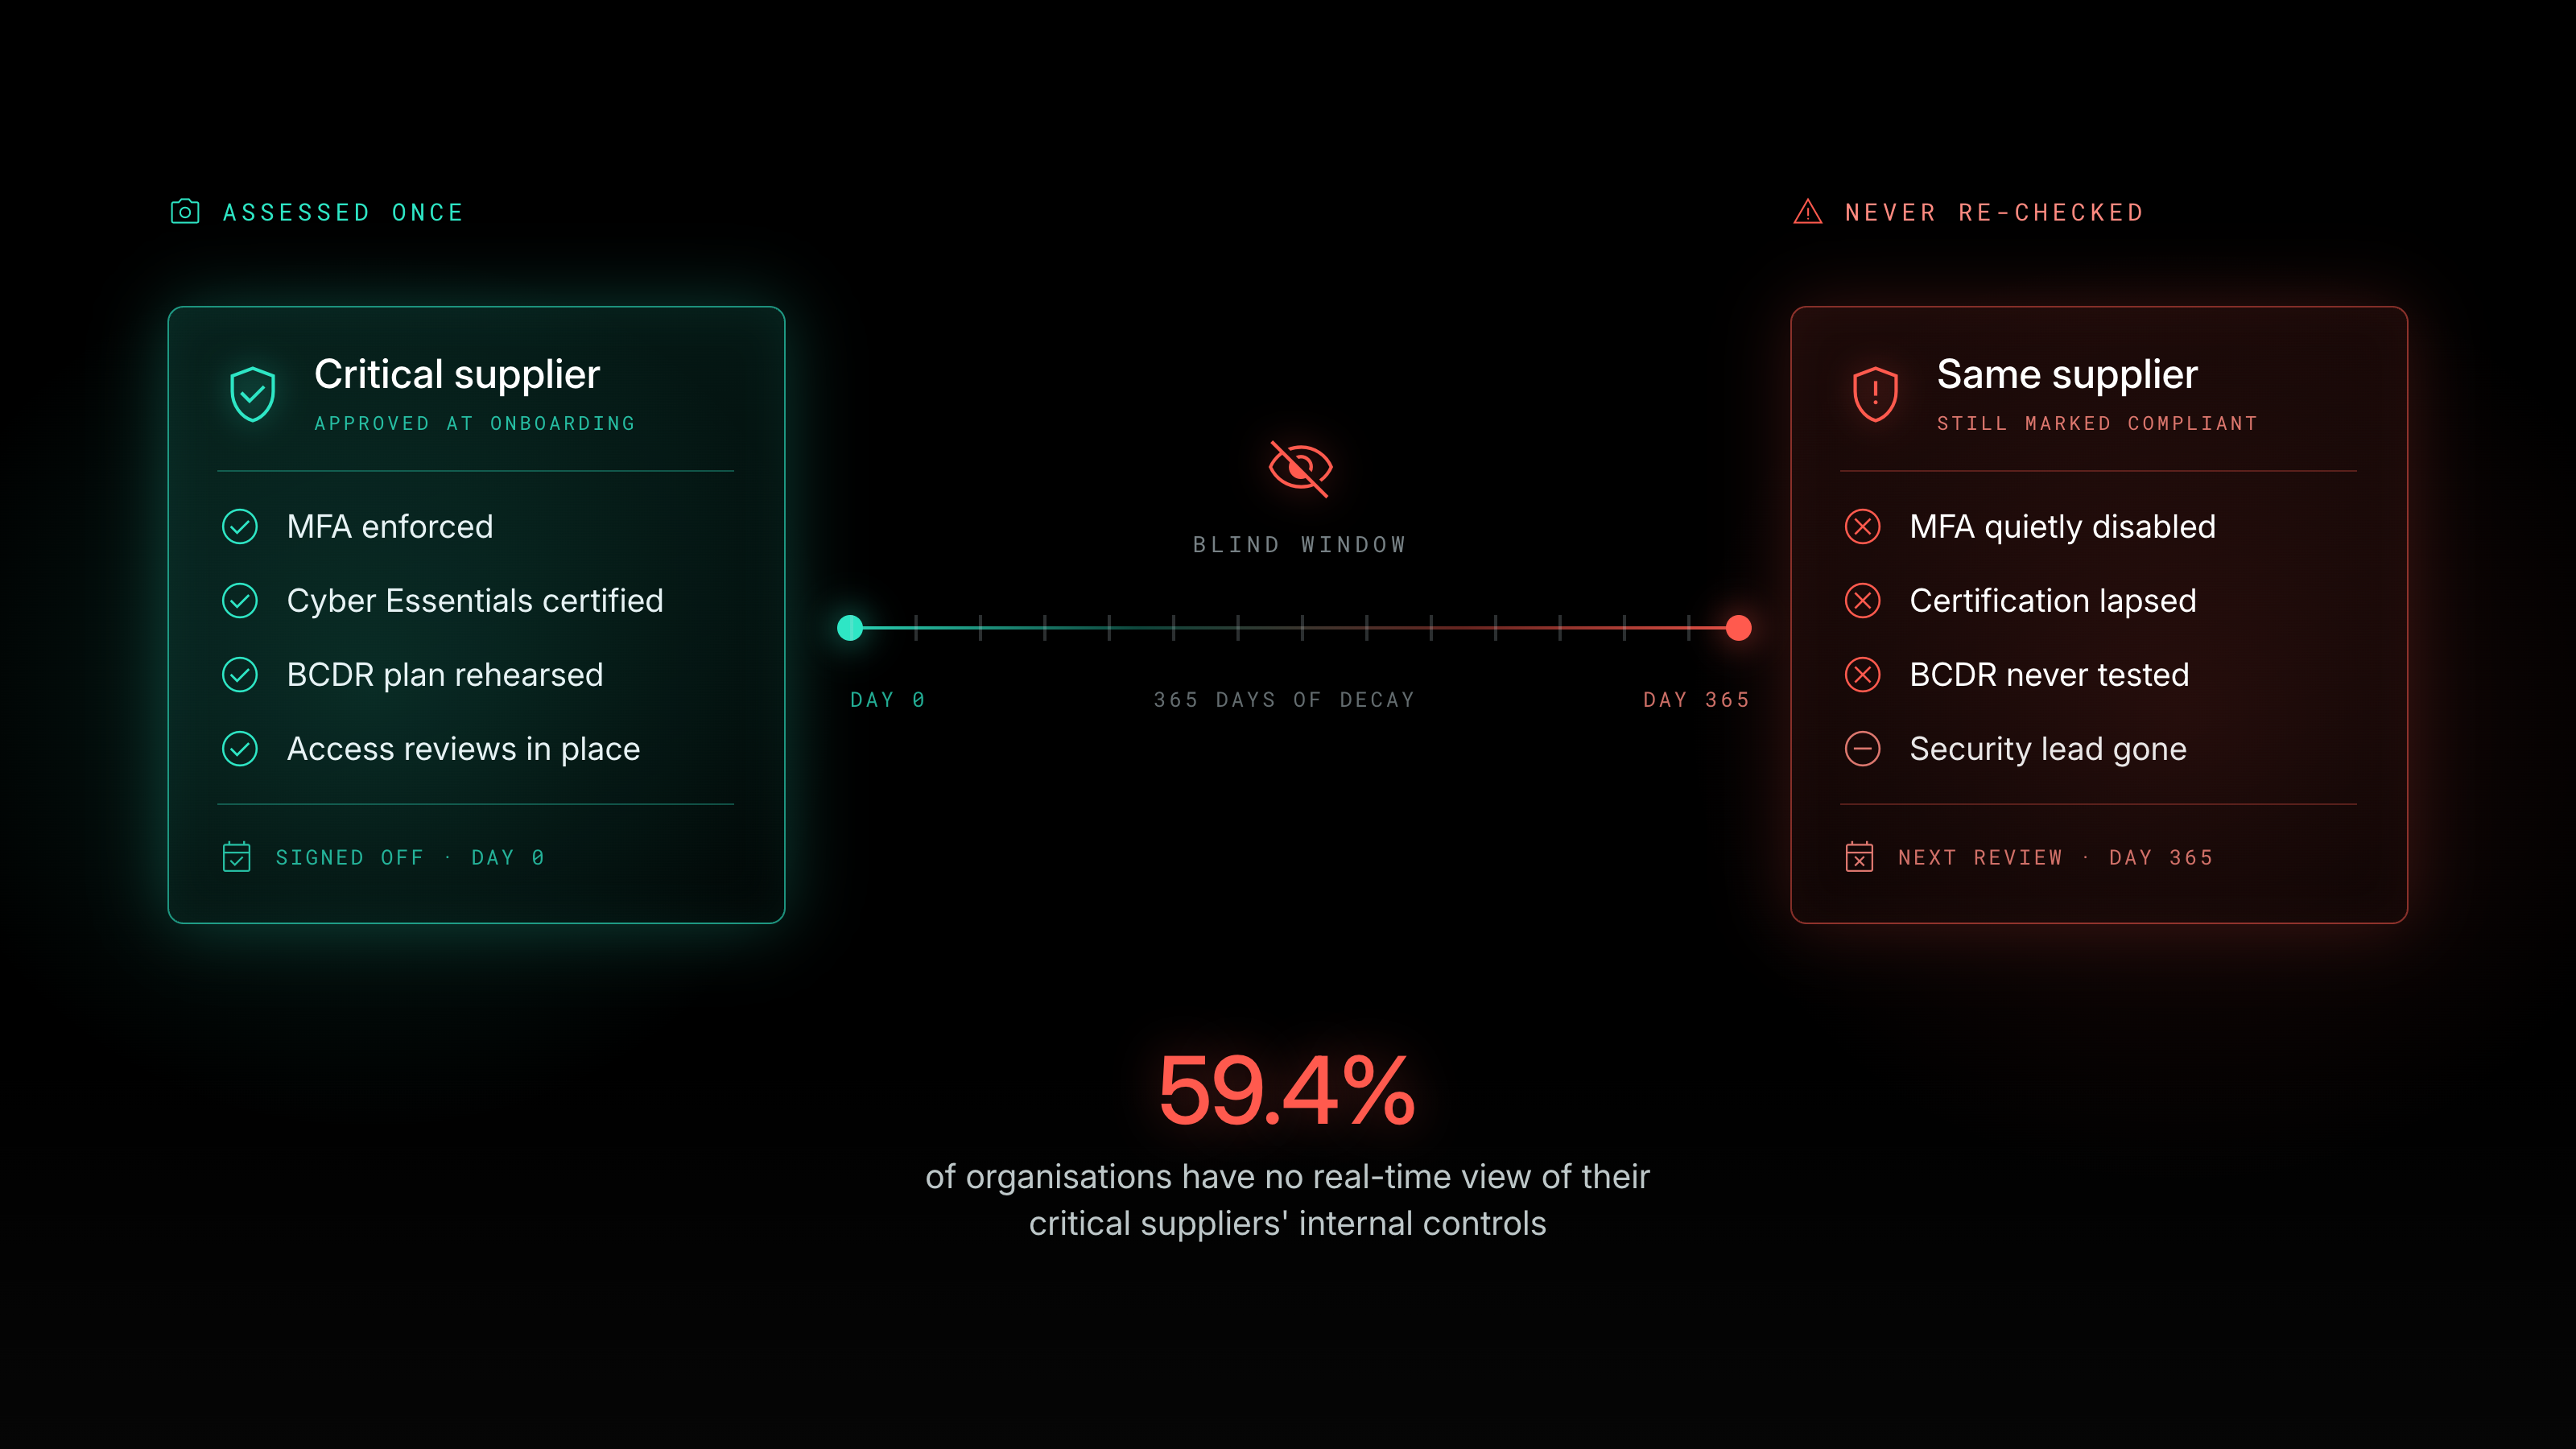
Point-in-time due diligence is creating a dangerous blind spot for security leaders. Despite strict new regulations, empirical data reveals that dozens of systemically vital UK suppliers actively lack foundational security controls — like MFA and regularly rehearsed disaster recovery plans. Read our executive summary to discover the operational reality of control erosion and learn why transitioning to continuous, Active Supply Chain Security (ASCS) is essential to protecting your organisation from systemic risk.
No items found.

Blog
CISO Briefing: Speed vs. Security - Eliminating the Commercial Bottleneck of Supplier Due Diligence
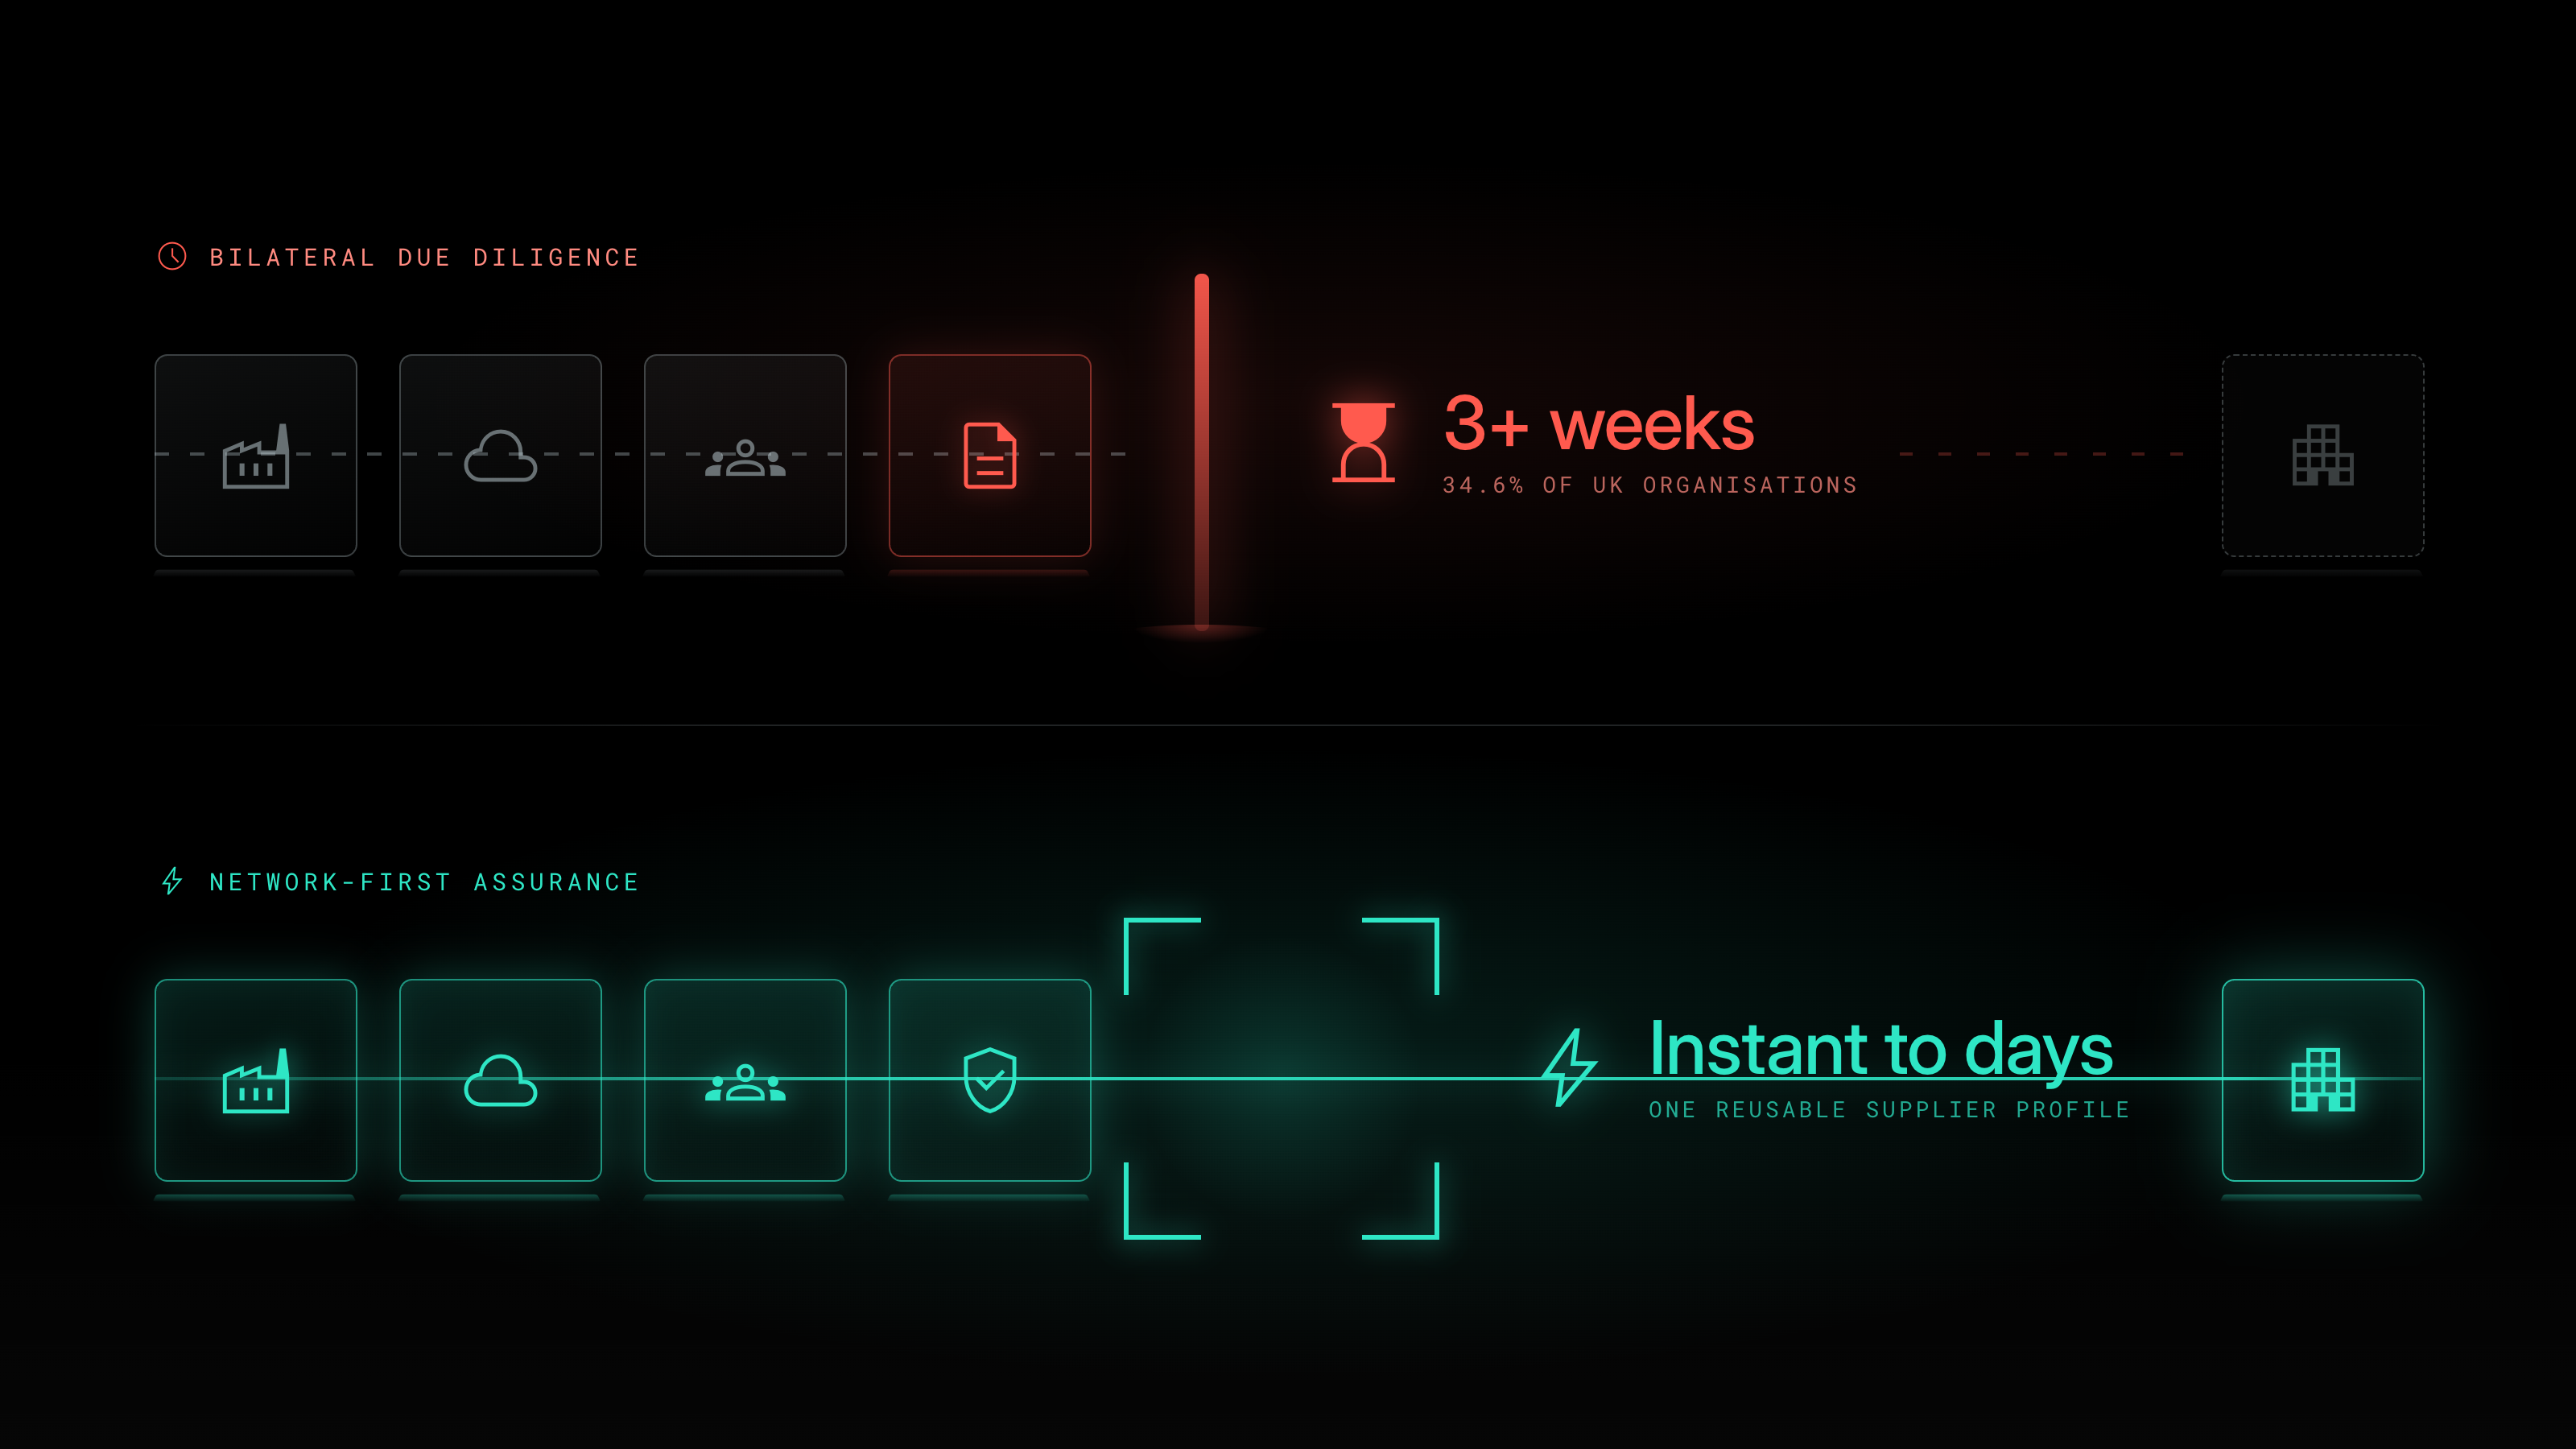
Traditional third-party risk management is creating a dangerous drag on business velocity. With over a third of UK organisations taking three weeks or more to clear new vendors, security teams are often viewed as commercial bottlenecks. Discover how CISOs can eliminate this friction and accelerate onboarding without sacrificing assurance by transitioning to a network-first Active Supply Chain Security (ASCS) model.
No items found.
Videos & Webinars
On Demand Webinar: Legal Supply Chains - From Third-Party Risk to Collective Resilience
Cyber threats don't stop at your direct suppliers. Catch up on our latest webinar featuring Justin Kuruvilla (Risk Ledger) and Ben Short (Blake Morgan) to learn how law firms are moving beyond traditional third-party risk assessments. Watch the full recording to discover why shared intelligence, improved visibility, and AI governance are the new foundations for collective resilience in the legal sector.
No items found.

Blog
CISO Briefing: The Illusion of Assurance - Exposing the Hidden Control Gaps in Your Supply Chain
Point-in-time due diligence is creating a dangerous blind spot for security leaders. Despite strict new regulations, empirical data reveals that dozens of systemically vital UK suppliers actively lack foundational security controls — like MFA and regularly rehearsed disaster recovery plans. Read our executive summary to discover the operational reality of control erosion and learn why transitioning to continuous, Active Supply Chain Security (ASCS) is essential to protecting your organisation from systemic risk.
No items found.

Blog
CISO Briefing: Speed vs. Security - Eliminating the Commercial Bottleneck of Supplier Due Diligence
Traditional third-party risk management is creating a dangerous drag on business velocity. With over a third of UK organisations taking three weeks or more to clear new vendors, security teams are often viewed as commercial bottlenecks. Discover how CISOs can eliminate this friction and accelerate onboarding without sacrificing assurance by transitioning to a network-first Active Supply Chain Security (ASCS) model.
No items found.