October 22, 2026
・
mins read


Updated 19 October 2026: restructured as a supplier assurance guide for public sector security leads, added CAF A4, GCAP and procurement context, a tiered supplier checklist, reassessment triggers, dependency mapping and supplier-failure guidance.
If you run security for a department, an arm’s-length body or a council, you will recognise the pattern. A supplier goes through careful checks at procurement, signs the contract, and then nobody looks at it again until renewal. Sometimes not even then. Public sector security leads describe this to us in almost the same words each time: assurance was strong right up to signature, then it stopped.
Two things make that hard to fix. The first is ownership. Security usually owns the risk, while commercial owns the supplier relationship, so suppliers get tiered by contract value rather than by what they could disrupt. The second is capacity. In many public bodies, supplier risk is one person’s job, or part of one person’s job, alongside everything else in the security function. A process built for annual questionnaires across hundreds of suppliers breaks under that load, and the suppliers that matter most end up reviewed no more often than the ones that barely touch your data.
You may call this supplier assurance, third-party risk management, vendor risk or supply chain cyber security. This guide works through three questions in order. Which suppliers matter? How do you keep their assurance current after signature? And how do you show a reviewer the decisions you have made? Where official guidance applies, it points to the NCSC Cyber Assessment Framework (CAF) Principle A4 and the Government Cyber Action Plan. Your assessor still decides how your CAF profile applies, so treat the steps here as a way to assemble evidence, not as a promised result.
A public-sector supply chain is the network of suppliers, service partners and the providers behind them that a public body relies on to run its services. Procurement teams judge it on value for money and transparency. For cyber assurance the question is narrower, and it is about which of those relationships could expose data, systems or service delivery if something went wrong.
The term gets used in two ways, and it helps to separate them. In procurement and logistics, a public-sector supply chain is how goods and services are bought and delivered, measured against value for money, transparency and social value. In security, it is a map of exposure, meaning every route by which a supplier’s failure or compromise could become your incident. This guide uses the second meaning. For the fundamentals of supply chain cyber security outside the public sector, see our guide to [supply chain security fundamentals].
The Government Cyber Action Plan, published in January 2026, makes the same point from the top down. It treats suppliers as holding some of government’s cyber risk simply because they deliver its services. It also places accountability for appropriate supplier assurance with each organisation’s Accounting Officer, extending, for lead departments, to their arm’s-length bodies.
Terms used in this guide
A supplier is in scope if its compromise, loss or misuse could expose people, stop an important service, undermine records or open a route into your systems. Contract value doesn’t decide it.
Scope test: Could compromise, loss or misuse of this relationship expose people, stop an important service, undermine records or create a route into our systems? If yes, it needs proportionate assurance.
Run that test across a typical council or department and the list grows quickly. Cloud and SaaS providers and managed service providers are obvious. So are software suppliers. Payroll bureaux, contact centres and shared services hold large volumes of personal data.
Charities delivering services, care providers and school transport operators often handle information about vulnerable people, sometimes on personal devices and consumer email accounts. Facilities and building-management contractors can have network access that nobody recorded at onboarding. A charity, a sole trader or an MOU-based arrangement is not out of scope because of what it is, and the most sensitive data in an estate can sit with its smallest suppliers. Being in scope does not mean a full assessment, though.
Most of these relationships need a handful of proportionate checks, and only the few that could stop a critical service need the full set.
An engagement is one specific thing a supplier does for you: a service, a system, a contract or an MOU. The distinction matters because the same company can do very different things for the same body.
Take a supplier that hosts a council’s public website and also runs the case-management system holding its safeguarding records. A single supplier-level rating treats those as one risk. The first exposes a marketing page. The second exposes vulnerable residents and the records social workers rely on every day. Security leads we work with describe assuring the engagement for exactly this reason, because the supplier’s name alone doesn’t tell them what’s at stake.
This also explains what can and can’t be shared between public bodies. A supplier’s profile, certifications and control evidence describe the company, so other organisations can reuse them. The risk decision depends on what that supplier does for you, so it stays local.
Engagement-level records take more upkeep than a single supplier list, and keeping them proportionate takes discipline. A basic record per critical engagement is enough to start. The record should name the service it supports, its owner, the data and access involved, and the date the evidence was last checked.
For most public bodies, supplier assurance is measured against Principle A4 of the NCSC Cyber Assessment Framework (CAF). Central government applies it through GovAssure. Councils in England apply it through the voluntary CAF for local government. The Government Cyber Action Plan sets out who is accountable. Procurement rules and data protection law sit alongside these as separate obligations.
It helps to sort the instruments into two groups before reading any of them. The first group sets the outcome you are assessed against: CAF A4, and the assurance routes that apply it to your systems. The second group shapes what you can require from suppliers and what you must do as a buyer, covering procurement law, policy notes and UK GDPR. Security leads tend to get pulled into the second group during tenders, while reviewers measure them on the first.
UK GDPR sits outside the table because it applies whatever your assurance route. Where a supplier processes personal data on your behalf, Article 28 requires specific contract terms and sufficient guarantees from that processor. A cyber questionnaire doesn’t replace those terms, and not every supplier is a processor, so confirm the actual processing relationship with your DPO.
CAF is outcomes-based. It describes what good looks like and leaves you to show how you achieve it, rather than listing controls to tick off. Principle A4 asks you to understand and manage the security risks to the systems behind your essential functions that come from depending on suppliers, including where third-party services are used. Version 4.0 splits this into two contributing outcomes. A4.a covers the supply chain itself. A4.b, new in v4.0, covers secure software development and support.
Security leads tell us supply chain is where their CAF reviews most often find shortfalls. That’s usually because the evidence was never assembled, not because nothing was done. At the basic level, A4.a’s indicators of good practice expect you to know the extent of the supply chain behind your essential functions, including subcontractors. They also expect your incident management to consider incidents that start in that supply chain. Higher profiles expect a deep understanding of the wider risks your supply chain faces, including subversion by capable, well-resourced attackers. Accountability stays with you even when a supplier runs the function.
In practice, reviewers tend to ask for evidence like this:
None of these is an official checklist. Your assessor decides how the outcomes apply to your profile, so agree the interpretation with them early. The same applies to “continuous”. NCSC guidance says a one-off assessment is not enough, but neither CAF nor GovAssure sets a reassessment frequency or requires a monitoring tool.
The route depends on what kind of body you are.
Central government departments and arm’s-length bodies use GovAssure. It assesses government critical systems at OFFICIAL against one of two government CAF profiles, Baseline or Enhanced. Lead government departments and government CNI organisations must also complete an independent assurance review. The GovAssure team now sits in the Government Cyber Unit at DSIT.
Councils in England use the CAF for local government. MHCLG adapted it from the NCSC framework, launched it in October 2024, and it is voluntary. By MHCLG’s own count, 90 councils had completed an assessment by early 2026.
NHS organisations have their own CAF-aligned route through the Data Security and Protection Toolkit.
Councils in Scotland, Wales and Northern Ireland have their own arrangements. Check which route your sponsor or regulator expects before you build evidence against the wrong profile.
The Cyber Security and Resilience Bill is still a Bill. It would update the NIS Regulations 2018, and its House of Lords Report stage is scheduled for 26 October 2026. It neither exempts public bodies wholesale nor puts a new duty on all of them, because scope depends on the activity and on regulations that haven’t been made yet.
What matters most to public bodies is the supply side. The Bill would bring managed service providers and data centres into regulation, and it would let government designate critical suppliers. Many public bodies depend on exactly those providers.
Procurement rules shape what you can ask suppliers for. They don’t decide what your reviewer measures.
PPN 014 is the policy note security leads need most. It applies to central government departments, executive agencies, non-departmental public bodies and NHS bodies, and other public bodies may choose to follow it.
Other procurement rules matter less to security leads:
Buyers often tell us contracts can’t name a particular assurance tool. Fair treatment of bidders is real, but it is a commercial judgement rather than a blanket legal ban. The safer route is to specify the outcomes you need and accept an agreed, proportionate way of evidencing them.
Gaining confidence in a supplier’s cyber security means checking its most important claims against evidence that covers the service it actually provides you. A questionnaire tells you what a supplier says it does. Certificates, test results and restore records tell you what has been checked, by whom and when. How deep you go should follow the harm the engagement could cause.
Questionnaires still earn their place. They are the quickest way to find out what a supplier says it has in place, spot where its answers don’t fit your service, and decide where to ask follow-up questions. The weakness is what happens next. An answer reads well, gets filed, and nobody tests whether the control behind it works. Security leads describe this as having a better questionnaire rather than real validation. The issue gets sharper now that suppliers can draft fluent answers with AI tools, though a well-written answer from a person proves no more than one from a model. Either way, the useful question for each answer that matters is what evidence sits behind it, whether that evidence covers the service you buy, and how recent it is. If those three questions come back empty, the answer is a claim, and your risk record should say so.
You don’t need to evidence every answer. Pick the claims that would hurt most if they were wrong, usually access control, backup and recovery, incident notification and the handling of your data, and test those.
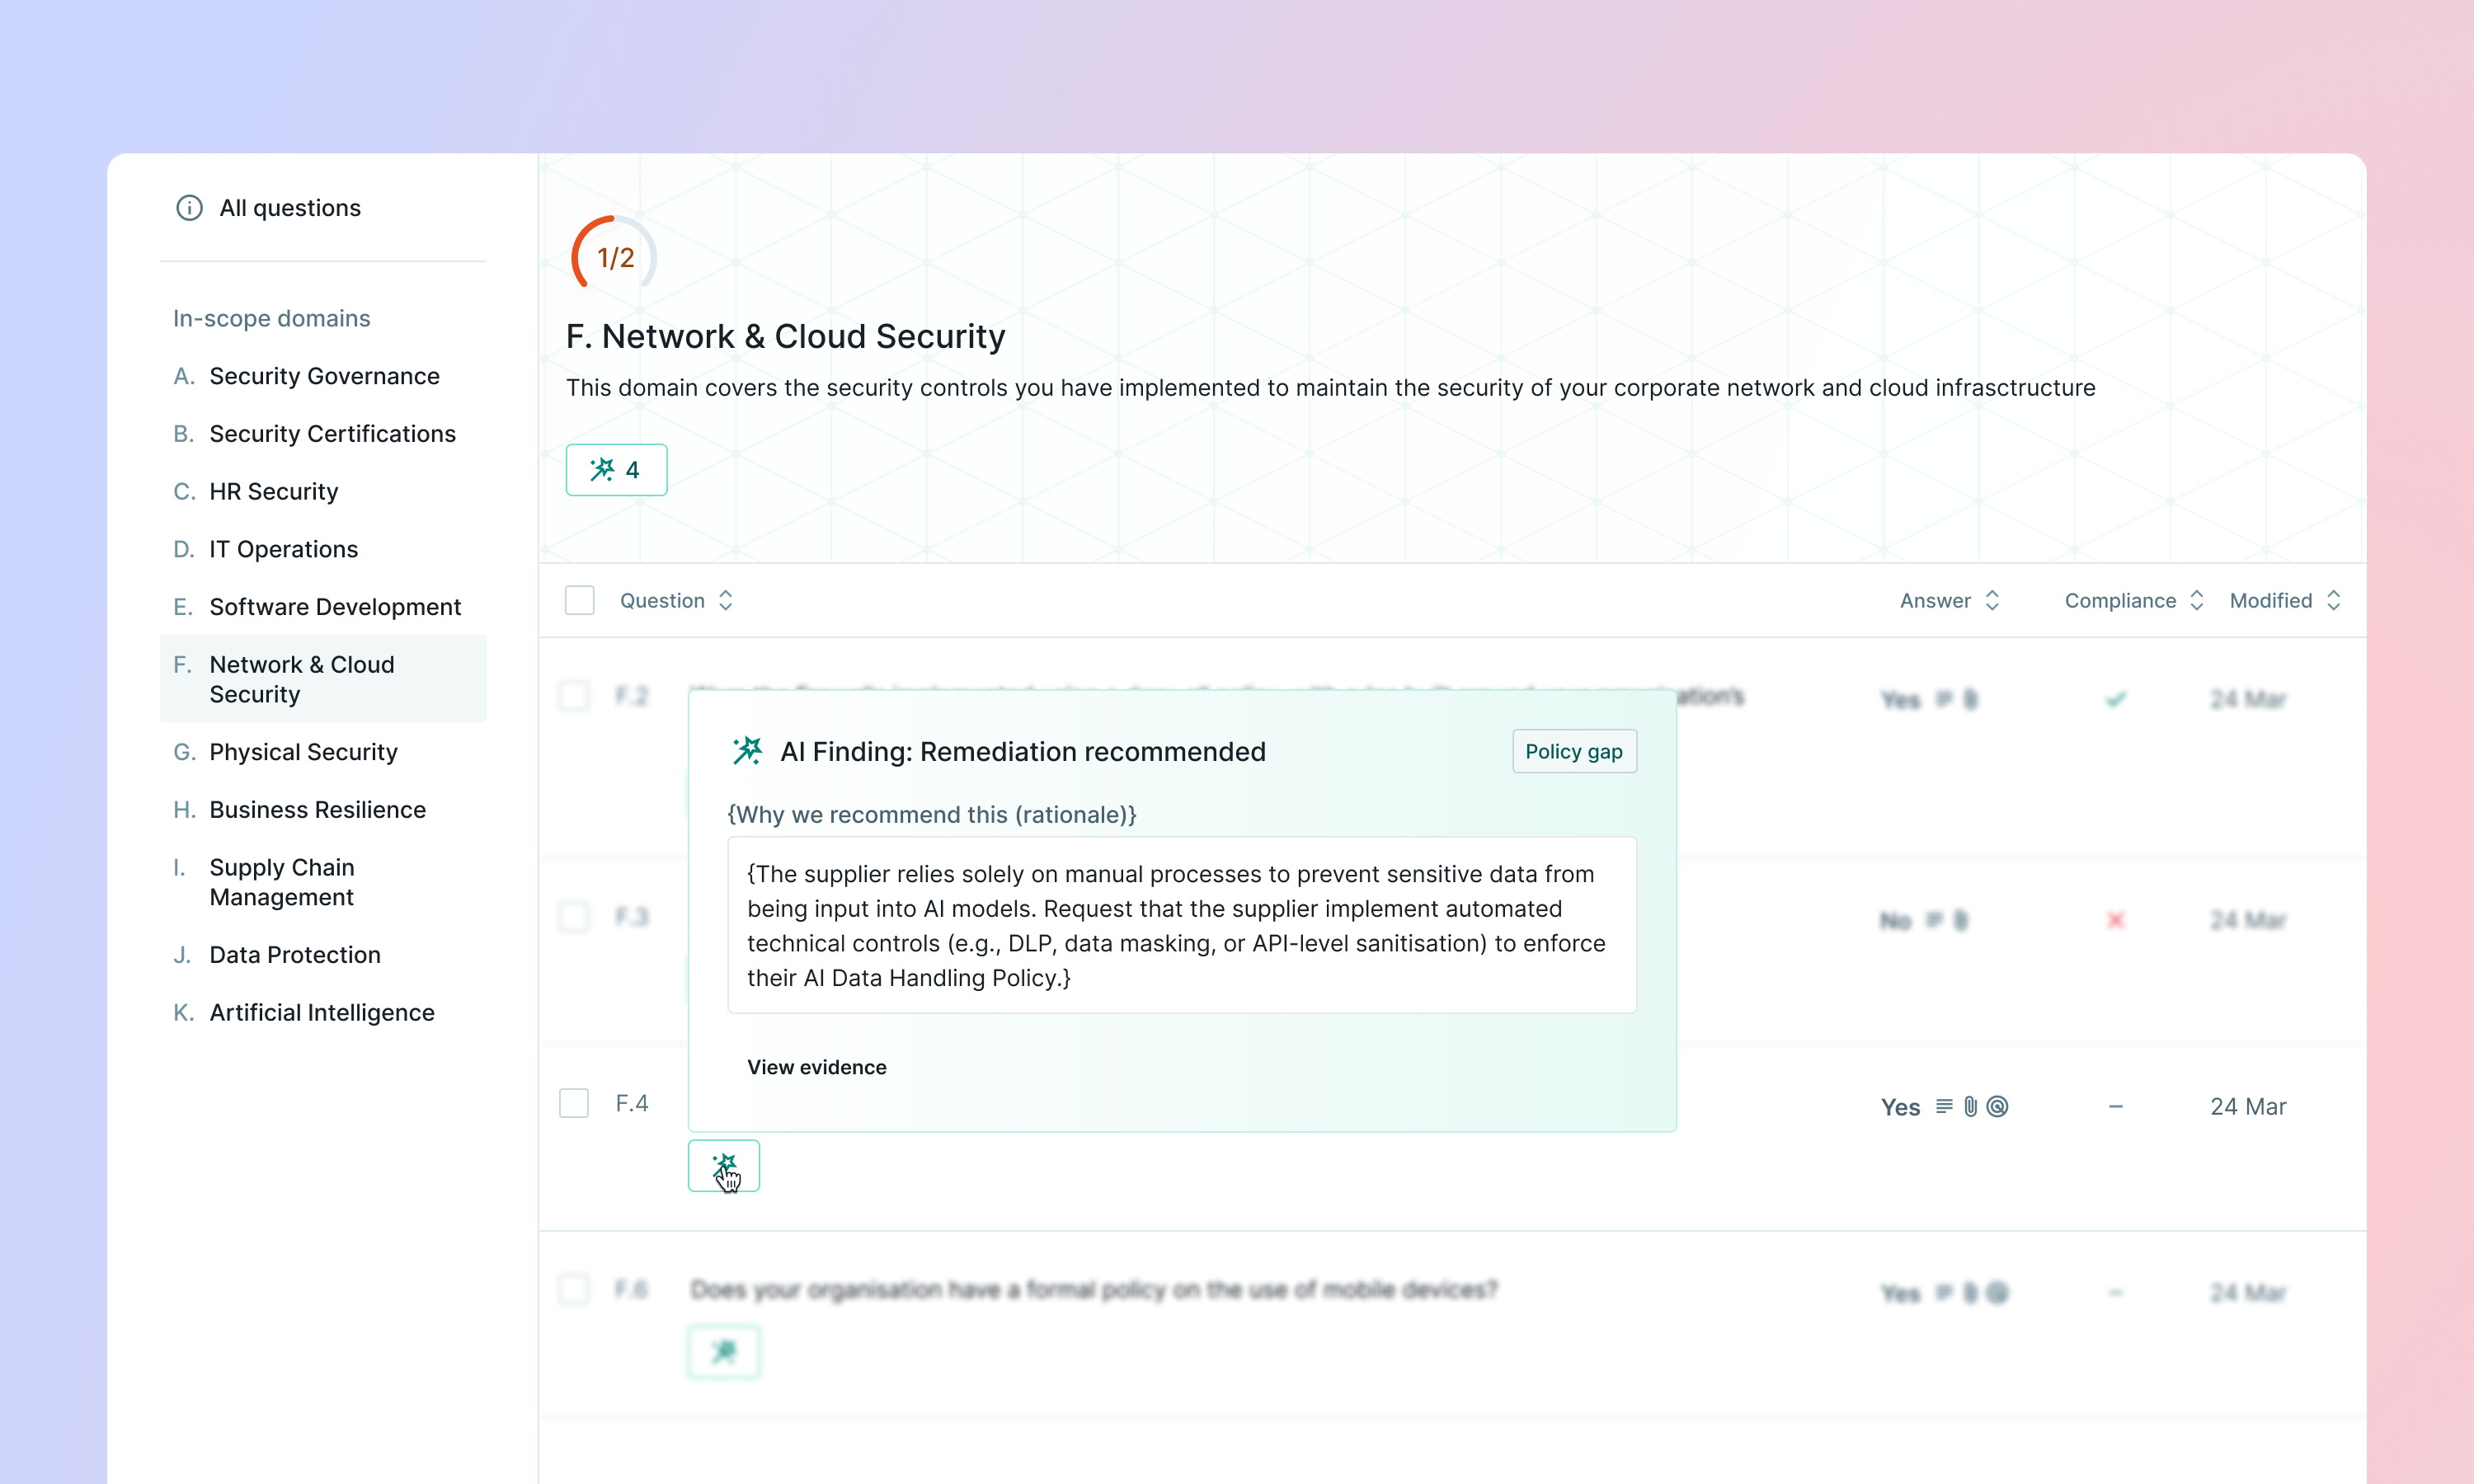
On Risk Ledger, suppliers keep one security profile that connected buyers can view, so you can start from evidence a supplier has already provided instead of sending a fresh questionnaire.
Every type of evidence answers some questions and leaves others open. A certificate tells you an assessor checked something within a defined scope. A penetration test tells you what was found in one system at one time. Neither tells you whether the supplier can restore your service after an incident. So judge each piece of evidence against the claim you’re testing and the service it supports, rather than ranking evidence types against each other.
Check the certificate, not the logo. A certificate covers a named legal entity, a defined scope and a date range. Ask which service it covers, when it expires and what it excludes. By PPN 014’s own wording, Cyber Essentials does not assure the specific product or service being supplied.
A supplier’s size tells you nothing about its risk tier. One council security lead described a painter and decorator who handled residents’ details through a personal Gmail account. Small providers like this are easy to leave off an assurance programme, and many of them hold sensitive information. Typical examples are sole traders, care providers, charities delivering services and school transport operators.
The answer is not a 200-question form. A small provider may not understand most of it, may abandon it, or may tick boxes to get through. Four plain questions usually tell you more, and a short call or an assisted walkthrough often works better than a document. PPN 014 supports this, warning buyers against cyber requirements that deter small businesses and voluntary organisations. It doesn’t exempt them, though. If a small provider holds highly sensitive data or supports a critical service, move it up to the important or critical checks below.
The checklist below is split by tier: five checks for critical engagements, three for important ones and four accessible checks for small or non-IT providers. Use the tier your engagement warrants, not the tier the supplier’s size suggests.
Keeping supplier assurance current means reviewing a supplier when something changes, not only when its contract comes up for renewal. NCSC guidance says a one-off assessment is not enough, and CAF A4 expects suppliers to be managed on an ongoing basis. Neither sets a review frequency, so set triggers for the events that change your risk and agree who acts on each one.
An annual questionnaire feels like ongoing assurance, but it describes a supplier as it was on the day it answered. Suppliers change hosting providers, add subcontractors, lose key staff and suffer incidents between reviews. Many public bodies can’t keep even the annual cycle going, so it slips to every two years, which leaves an even longer window of change. Triggers turn that around. A material change prompts a targeted review of the part that changed, and the full reassessment is saved for renewal or for critical engagements.
On Risk Ledger, suppliers maintain their own security profile, so connected buyers see updates between their own review cycles.
Security leads in departments, arm’s-length bodies and councils describe the same pattern. Checks are thorough during procurement because the tender process forces them. Once the contract is signed, nothing comparable forces them to happen again.
Three things keep it that way:
These aren't a technical fix. The fix is agreeing with commercial and service owners who notices each trigger, and recording it where both teams can see it.
A trigger is any event that could change how much you rely on a supplier or how much you can trust it. Each trigger needs three parts to work. Someone has to be in a position to notice it, there has to be a defined first action, and one person has to own the outcome. The table below gives a starting set.
Treat the timings as local decisions. Set triage and escalation times you can actually meet for each level of severity, and keep them separate from any legal reporting duties, which your legal and privacy teams decide case by case.
Most public bodies can’t add new rights to a contract after signature, so award and renewal are the moments that count. Discuss these topics with commercial and legal colleagues. They are areas to cover, not model clauses:
Some suppliers stop responding once the contract is signed. Below-threshold contracts and MOU-based arrangements often give you little leverage to begin with. A refusal still has to be handled, because silence from a supplier is not evidence that it’s safe. It isn’t proof of compromise either. What you can do is make the uncertainty visible and get the right person to decide on it.
A risk statement can be short:
“For [service], we cannot verify [control or dependency] at [supplier] despite [requests and dates]. If [event] occurs, [harm to the public service, data or people] may result. Current mitigations are [x], and residual uncertainty is [y]. [Authorised owner] decided to [action] until [review date], subject to [conditions].”
Showing an auditor the request, the refusal, the decision and the review date demonstrates that you followed a process. It does not automatically meet a CAF outcome, remove a legal duty or make an intolerable risk acceptable. If you cannot show that personal data is processed lawfully or that a service can be delivered safely, escalate through legal and service routes rather than relying on a signed risk entry.
Mapping fourth- and nth-party dependencies means identifying the providers your suppliers rely on, and the providers behind them, then finding where the same provider supports more than one of your services. In the public sector, start from one critical service rather than your whole supplier estate. Record where each link came from and how confident you are in it.
Your supplier list isn’t your risk map. A council can be breached through a company it never signed a contract with, because one of its suppliers depends on that company to host, authenticate or support the service. The contract register shows two independent suppliers. The dependency map can show that both rely on the same cloud host and the same identity provider, which means one outage could take down services that look separate on paper.
Government has made the same case at national level. The Government Cyber Security Strategy 2022 to 2030 called for central mapping of critical and common suppliers. The Government Cyber Action Plan now puts high-risk strategic suppliers under coordinated oversight, so their failures can be seen across government rather than one department at a time. A single public body can apply the same logic to its own critical services, on a much smaller scale.
Trying to map every supplier’s supplier across a whole estate is where most mapping efforts stall. A bounded map is smaller and more useful.
For the general method of mapping tier-two and tier-three suppliers across any organisation, see our guide to [supply chain visibility]. For why direct-supplier programmes miss this layer, see [the nth-party blind spot].
Every link on a dependency map comes from somewhere, and the source decides how much weight it can carry. Most links fall into one of three states. Supplier-declared links are ones the supplier has told you about. Independently evidenced links have been confirmed by a contract, an architecture record or a technical check. Inferred links are ones you or a tool have deduced without confirmation. Some links will also be unknown or out of date, and those should stay on the map. Leaving them off makes the map look complete when it isn’t. Treating a missing link as absence of risk is the most common way a dependency map misleads the people who rely on it.
Once a provider appears more than once, ask a second question: would the same event disable both paths? Two services on the same cloud provider may run in different regions with separate controls, so they aren’t automatically one failure point. Two different direct suppliers aren’t automatically independent either. Check regions, identity and management access, privileged support, backup access and network routes before calling either situation resilient.
Seeing a relationship on a map also doesn’t prove that data flows along it or that a compromise could spread through it. Some public sector teams also tell us they need the basics in place first. If your critical engagements don’t yet have owners and current evidence, start with the three steps at the top of this guide, and come back to mapping once that’s done.
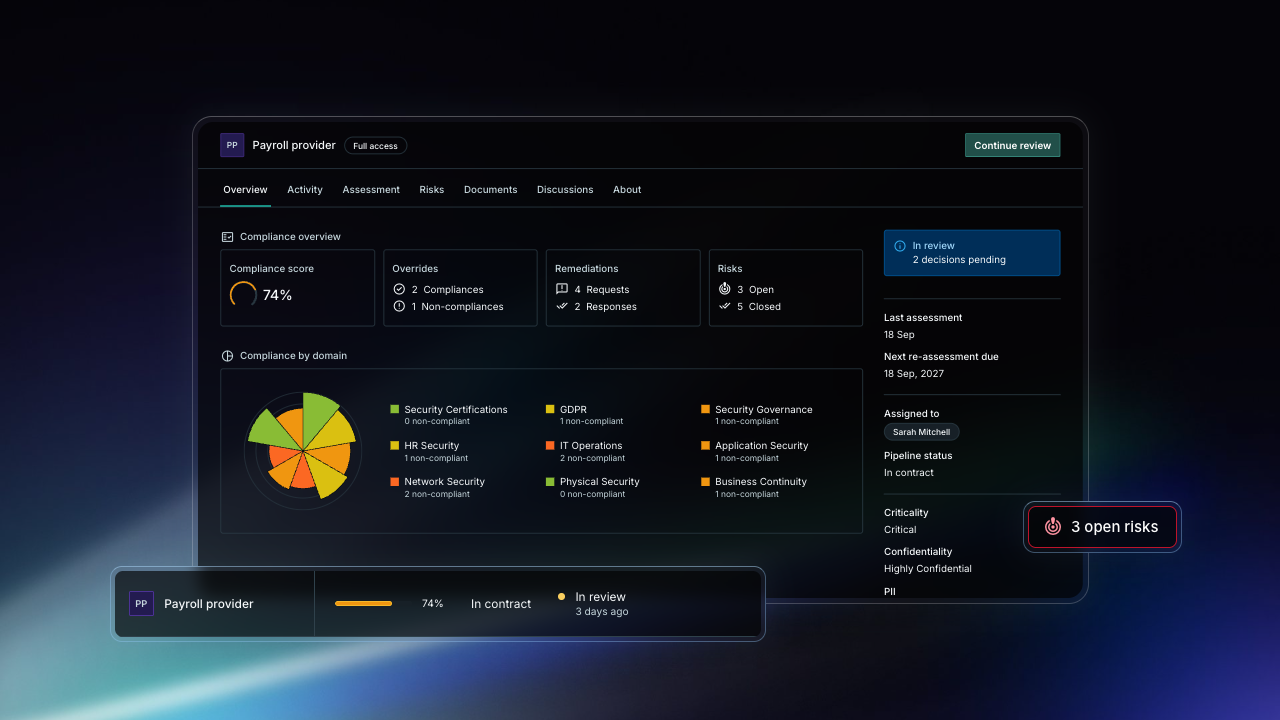
Risk Ledger maps the connections between suppliers on its network, so you can see where several of your suppliers rely on the same provider.
Run the Supply Chain Risk Exposure Assessment →
When a critical supplier fails, the service that depends on it fails too, unless you already know three things. You need to know which of your services rely on that supplier, what you would use instead, and whether that alternative shares the same dependencies. The supplier’s recovery plan covers its own systems. Keeping the public service running is still your job.
Security leads usually find out about this the hard way, during an incident. A supplier can have strong controls and still go down. Its cyber assessment can’t tell you how long your service could run without it, or whether you could switch to someone else at short notice. Those are resilience questions, and they need different evidence. For each critical supplier, that evidence covers a tested restore, a working manual process, a substitute that’s actually available, and a clear view of the backlog you’d face afterwards.
Two things make a supplier failure worse than it needs to be. The first is concentration. Several services quietly rely on the same provider, so one outage hits all of them at once. The second is low substitutability, where no realistic alternative exists in the time the service can tolerate. A [supplier criticality matrix] helps you rank suppliers on both before an incident forces the question.
The first hour of a supplier incident is mostly about answering one question: are we affected? These questions get you there faster:
Resist the instinct to disconnect everything. Cutting a supplier’s access can protect your systems, but it can also stop an essential service that people rely on that day. Make the call through your incident command structure, weighing both risks, and keep the evidence you’ll need later.
Answering the first question is far faster if you’ve already mapped which suppliers depend on which providers (see the previous section).
When a widely used provider reports an incident, Risk Ledger users can check which of their connected suppliers rely on it.
A recovery plan you haven’t tested is only an assumption. These questions show where the plan rests on hope rather than evidence:
The Synnovis attack showed that a cyber attack on a single supplier can disrupt public services for months, and that the data impact can reach far beyond the area where services stopped. Synnovis provides pathology testing to NHS organisations. A ransomware attack in June 2024 cut its capacity to process tests, and full restoration took until December 2024.
The detail that matters most for security leads is the difference in reach. According to NHS England, the appointment cancellations were confined to south-east London, where Synnovis’s partner trusts and their local boroughs are based. The stolen data, however, could relate to any of Synnovis’s service users, including some hospitals, GP practices and clinics across England.
Working out what was taken took more than a year, because the data was unstructured, incomplete and fragmented. So the availability impact and the confidentiality impact had different footprints and different timelines. Planning for only one of them would have left the other unmanaged. Synnovis is also co-owned by two of the NHS trusts it serves, which shows that a close ownership link doesn’t remove the need to plan for that supplier failing.
Three lessons follow. These are our inferences, not official findings about the cause:
Nothing in the public record shows how the attackers got in, so no lesson here depends on a particular entry point or missing control.
Reorganisation can hand a successor council a supplier estate it never assessed, made up of contracts, exceptions and dependencies from several predecessor bodies. To bring that estate under control:
Start with the services the new council can’t afford to lose, and work outwards from there.
Public bodies can reuse a supplier’s evidence, such as its security profile, certifications, independent reports and remediation status, provided they check its relevance and keep the risk decision for their own service. Reuse removes the duplicated questioning. It does not transfer accountability, which stays with each body under CAF and, for personal data, under UK GDPR.
Security leads raise this in two forms. The first is frustration. If another department or council has already assessed a supplier, why does every body ask the same questions again? The second is caution. If I accept another body’s review, have I just accepted their risk as well? Both concerns are fair, and they have the same answer. Evidence about the supplier can be shared. The judgement about what that supplier means for your service cannot.
Reused evidence still needs a quick check before you rely on it:
Sensitive reports shouldn’t circulate widely just because both organisations are public bodies. Reuse works when sharing is permissioned and recorded.
Lead departments face a version of this at group level. The Government Cyber Action Plan gives them accountability for cyber risk across their arm’s-length bodies, many of which have no specialist security staff. A federated model handles that without centralising every decision:
Central visibility shouldn’t be read as the department accepting an arm’s-length body’s risk, and it doesn’t remove that body’s own accountability. The operating design still needs approval through each organisation’s governance.
Editor’s note: Written by Haydn Brooks, Risk Ledger’s co-founder and CEO, an earlier version was published by techUK.
There is a vast amount of duplicated effort across public sector bodies when performing these reviews, especially given the often significant overlaps between their respective supply chains.
The NCSC issued a threat alert in April, warning of escalated threats emanating from cyber attacks by state-sponsored threat actors against UK Critical National Infrastructure. This coincided with a speech by Cabinet Office minister Oliver Dowden at CyberUK in Belfast, in which he stated that the UK was facing a new adversary, “the cyber equivalent of the Wagner group”. These Russian-aligned groups, he explained, initially “focused their attacks on Ukraine and the surrounding region. But recently, they have begun to turn their attention to the UK and its allies”.
But even beyond the rising threat from state-sponsored attacks against the UK, the public sector has long been a prime target of a wide range of threat actors. In fact, 40% of all incidents managed by the National Cyber Security Centre between September 2020 and August 2021 were aimed at the public sector, while a freedom of information request from last year revealed that local authorities faced as much as 10,000 cyber attacks every day.
Many of these take the form of attacks on the weakest possible link in an organisation’s cyber security posture, often its supply chains. Supply chain attacks have become one of the leading cyber threats facing organisations, and can be among the most devastating, as prominent examples such as the SolarWinds (2020), Log4J (2021) or the recent MOVEit Transfer (2023) supply chain attacks attest to.
The UK public sector has already found itself at the sharp end of these attacks, for example when the NHS was affected by a breach at one of its suppliers, Advanced, causing serious disruptions to its NHS 111 services.
The UK Government is very much aware of the scale of the threat, and has taken a determined leadership role in addressing it. This is evident in the new National Cyber Security Strategy 2022 and the subsequent Government Cyber Security Strategy 2022-2030, which is specifically aimed at strengthening the resilience of the public sector.
As part of this strategy, the Government provides public sector organisations with a range of best practice guidance and principles for enhanced supply chain risk management, including through GovAssure, which is underpinned by the NCSC’s Cyber Assessment Framework (CAF), and is a new cyber security assurance scheme for the public sector. This is all good news, and the guidance places the right emphasis on the need for:
The Strategy’s second pillar, ‘Defend-as-One’, meanwhile, sets out the vision for bolstering the public sectors’ collective cyber defences by harnessing “the value of sharing cyber security data, expertise and capabilities across its organisations to present a defensive force disproportionately more powerful than the sum of its parts.”
These Government efforts are vital and clearly set out what needs to be done. The next step, however, is to find ways to achieve the goal of hardening public sector supply chain cyber security. This is where organisations struggle to identify time- and cost-effective solutions that will actually make a difference.
The main problem is that traditional approaches to supply chain security are broken. They simply will not allow public sector organisations to achieve the goals set out in the Government Cyber Security Strategy, and to substantially reduce the risks from supply chain attacks. What is needed is nothing less than an entirely new approach to supply chain cyber security.
But let’s start with where the main problems lie with more traditional supplier risk assessment approaches. These approaches still rely, to a large extent, on highly manual and time-consuming risk assessments that provide at best a point in time insight into the security postures of individual suppliers.
Also, right now, each public sector organisation is performing their own assessment on each individual supplier’s security. Whilst there is a need for nuance based on the individual context, there is a vast amount of duplicated effort across public sector bodies when performing these reviews, especially given the often significant overlaps between their respective supply chains.
The time- and resource-demands of reviewing completed individual supplier assessments alone are great enough. This makes continuous monitoring of suppliers’ security postures, beyond occasional re-assessments, a distant dream. The same is true for efforts to map the entire supply chain ecosystem and achieve greater visibility into risks beyond immediate third party suppliers, in 4th, 5th, and n-th parties.
So what can public sector bodies do to overcome these challenges and constraints that more traditional approaches to third party risk management bring with them?
The answer is to, in the spirit of ‘Defend-as-One’, adopt a collective approach to supply chain cyber security that puts a premium on collaboration, between public sector organisations as well as between organisations and their suppliers.
Combining a Third-Party Risk Management platform with a secure social network offers a way forward. Similar to a social network like LinkedIn, each organisation has a profile on the same platform, which contains information about their business, their security controls and other relevant risk areas, including ESG and financial risk. This profile is then shared with their clients and customers. Clients can set requirements against the framework, so they can compare suppliers against criteria which matter most to them.
With clients and suppliers on the same platform, often in both capacities, meaning they can simultaneously show their security posture to their clients and monitor the security posture of their own suppliers, this uncovers the middle links in supply chains; it builds a map of relationships and interdependencies within the full ecosystem, including among 4th, 5th and nth parties, not just between one client and their third-parties. This offers a uniquely customised view of the entire network of connected organisations for different use cases, with analysis on the resilience of the ecosystem, detecting and measuring concentration and systemic risk.
This new approach lays the groundwork for a future of “Defend-as-One”, where network effects can be leveraged into a collective defence approach. When everyone is connected, an attack on one organisation is tantamount to an attack on every organisation, which means that looking out for each other can only be beneficial. And conversely, failing to collaborate can only be detrimental for everyone involved. When it comes to cyber security, organisations can only win when they play as a team.
If you are interested in finding out about how large public sector organisations such as NHS Test & Trace (now the UK Health Security Agency), another large public sector body and a large number of UK water companies have applied Risk Ledger’s social network approach to supply chain security, get in touch with us. We look forward to hearing from you.
This article was originally published by techUK.
We built Risk Ledger around the argument in Haydn’s piece. Instead of each buyer sending each supplier its own questionnaire, suppliers keep one security profile and share it with the organisations they work with. Buyers set their own requirements against that profile. They then spend their time on the gaps that matter for their service, not on collecting the same answers again. Because many organisations are both buyers and suppliers on the network, those connections also show the providers sitting behind direct suppliers, and where several organisations depend on the same one.
A small team should start with one critical service rather than its whole supplier estate. In the first 90 days, do three things for that service. Establish who owns each supplier engagement behind it, close the largest evidence gaps, and test what happens if a key supplier fails. Then repeat the process with the next service.
Most supplier assurance programmes in the public sector are run by one to three people alongside other security work. That rules out reassessing every supplier every year, and it should. Assurance built around a few services that matter, with named owners and current evidence, holds up better in a review than a complete supplier list where nobody has looked at most of the entries since onboarding.
A sustainable rhythm for a team of one usually has four parts:
If that rhythm doesn’t fit, reduce the scope of what you assess. Inventing a cadence you can’t keep is worse.
Avoid four things in the first 90 days:
Leadership needs to know whether the services the body can’t afford to lose are covered. They usually don’t need a count of how many suppliers were assessed. One question frames the whole report:
For the services we cannot afford to lose, do we know the supplier dependencies, the current evidence, the fallback and who accepted the remaining risk?
A small dashboard can answer that question if it measures decisions rather than activity:
Define your terms before you report. Say what counts as “current” and “critical”, and give the reporting date. Keep five states separate: not assessed, insufficient evidence, control gap, accepted residual risk and treated. A completed form is not the same as an assured service, and a dashboard that merges these states will tell leadership more than it knows.
Don’t invent a return-on-investment figure. Build a baseline from your own numbers. Count the time spent collecting and reviewing evidence, chasing suppliers, repeating assessments other bodies have done, preparing for audit and tracing dependencies during incidents. Then measure what changes after a pilot. Include governance, privacy and adoption effort in the cost, not just software.
If you are the Director or Head of who signs this off, the ask is a proportionate operating model, not a new team. It should close audit findings and keep critical services running. For lead departments, it should also give group visibility of arm’s-length bodies, which the Government Cyber Action Plan makes your responsibility. The effort should scale with the number of critical engagements, not with the size of the supplier list.
To see where your own exposure sits, run the free Supply Chain Risk Exposure Assessment.
Monthly research, case studies and practical guides you won't find anywhere else.
Join thousands of security managers turning their TPRM programmes into success stories.