November 17, 2026
・
4
mins read

A third-party risk management (TPRM) framework is the structured set of policies, controls and processes you use to manage supplier risk from selection to exit. Most organisations build one by combining a binding obligation, such as DORA, with a control standard, such as NIST CSF 2.0 or ISO/IEC 27001.
Most programmes can answer “did we assess this supplier?” The harder question is “can we still trust them?”, and a framework only helps with that if someone keeps working it after the contract is signed.
This is a starting order of work, and an auditor will still expect the full framework behind it.
A third-party risk management framework is the agreed structure your organisation uses to identify, assess and reduce risk from suppliers, vendors and service providers. It sets out the security, compliance and operational standards you expect, how deeply you assess each supplier, and when you look again. That gives security teams one consistent method, so suppliers don’t fall through the cracks.
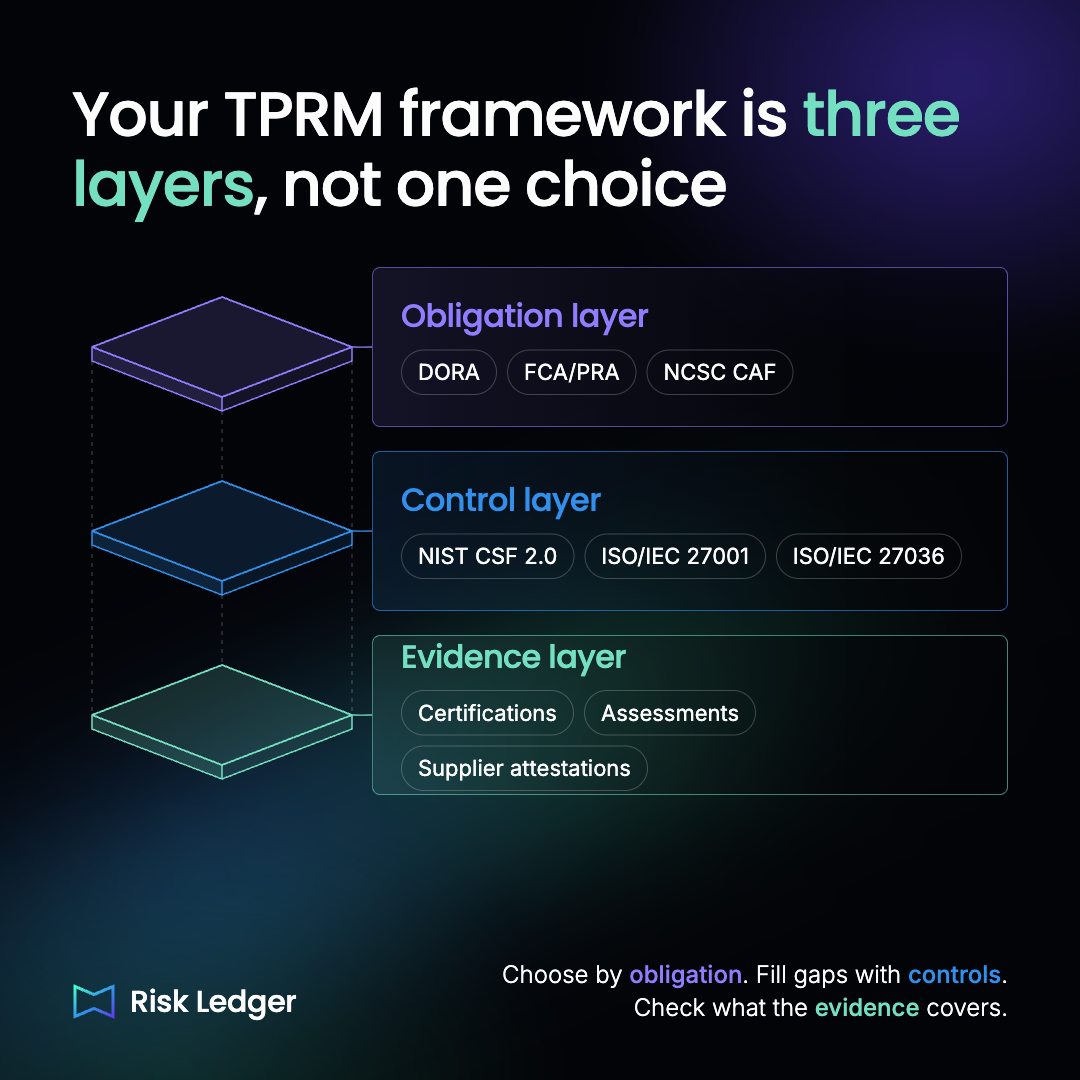
Most programmes draw on three kinds of source:
A framework matters because supplier risk rarely fails at the first assessment. It fails later, when nobody owns the relationship. Security teams consistently describe the same pattern: a thorough review before signature, then little or nothing until renewal, with annual reviews quietly slipping to every two years.
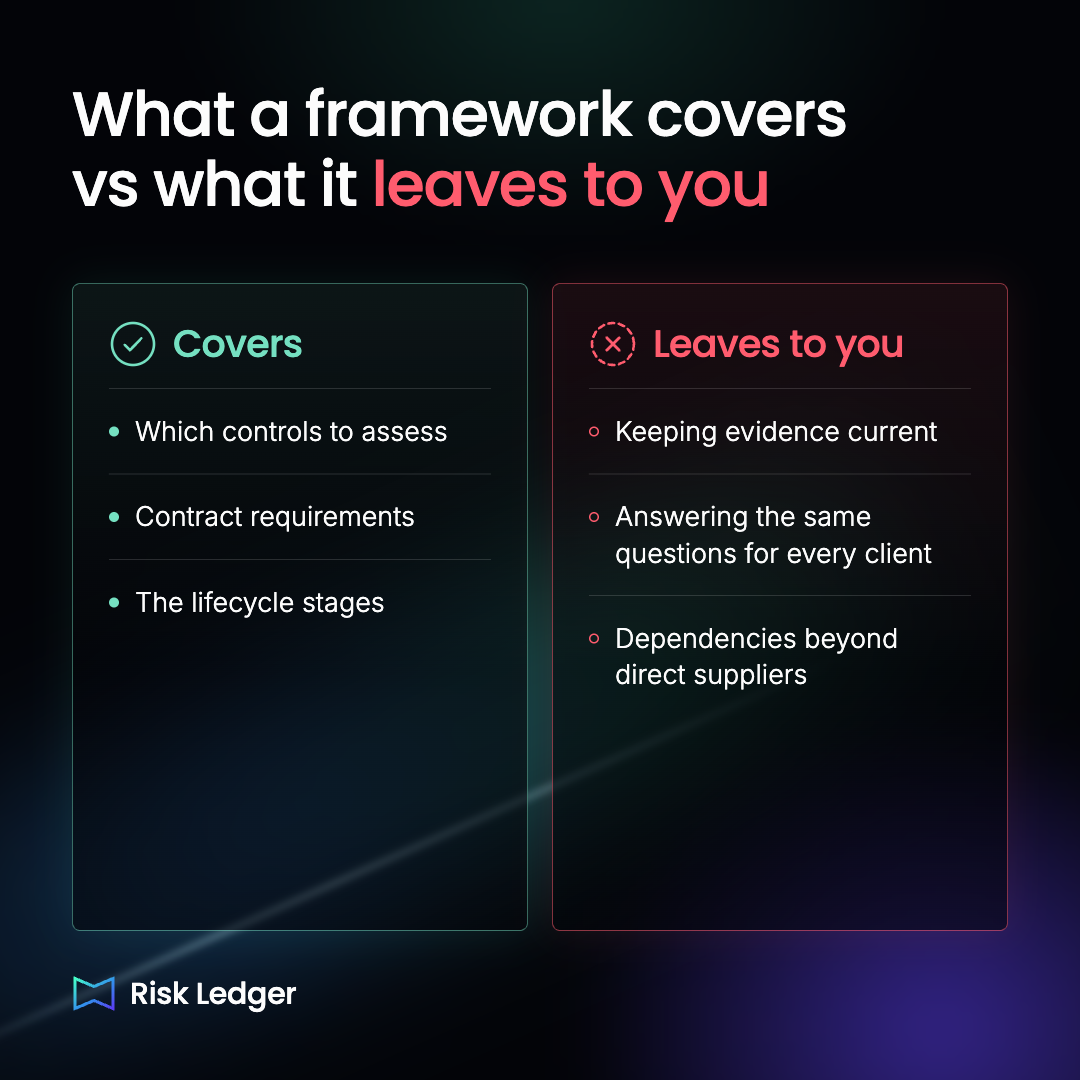
A framework counters that by deciding in advance who owns each supplier, what evidence counts and what triggers a fresh look. It also lets you show an auditor or regulator that supplier decisions follow a consistent method, which DORA and UK GDPR both expect you to demonstrate. The limit is that a framework describes the work. It doesn’t keep evidence current or tell you which suppliers depend on the same providers, and those are the points where programmes tend to drift.
Choose by obligation first, then fill gaps. DORA is a binding regulation for in-scope EU financial entities. NIST CSF 2.0 and ISO/IEC 27001 are voluntary standards, with ISO/IEC 27036 covering supplier relationships specifically. NCSC supply chain guidance suits UK organisations. Most organisations combine one regulatory or primary framework with another for control detail.
Most TPRM frameworks lean one of three ways. Risk-based frameworks direct effort to the suppliers that could hurt you most. Compliance-driven frameworks start from what a regulator or customer requires. Operational frameworks focus on keeping critical services running when a supplier fails. The third party risk management frameworks most UK and EU teams work with each cover part of that ground, which is why combining them usually beats choosing one.
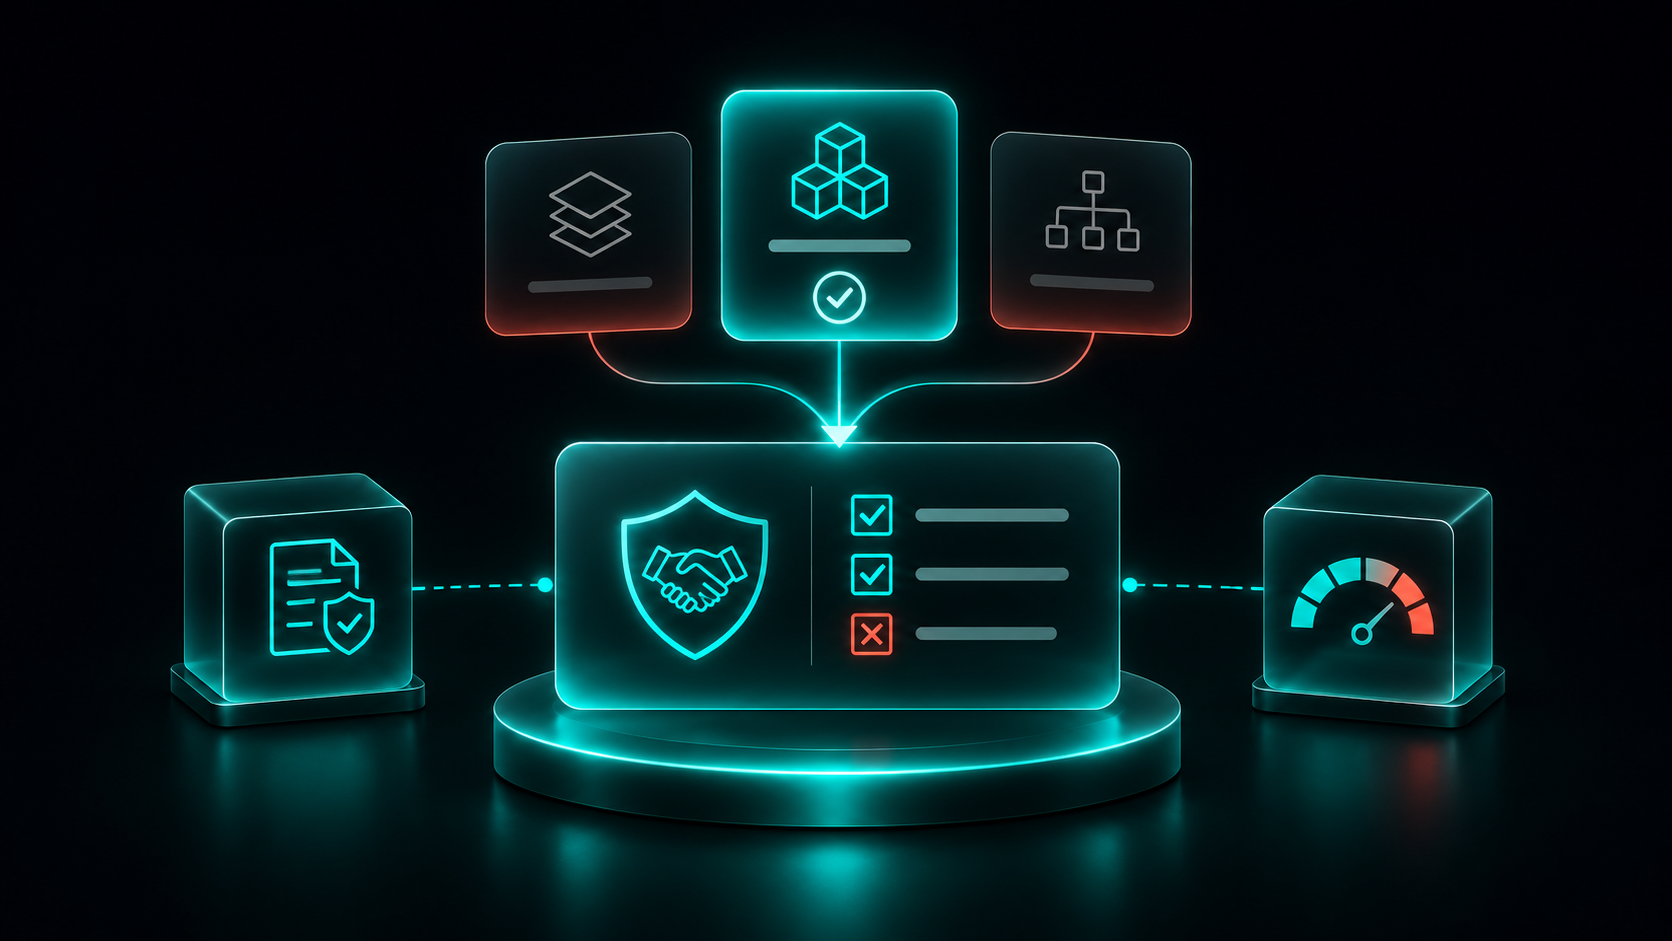
[Graphic: “Your TPRM framework is three layers, not one choice”. Alt text: “Three-layer diagram showing obligations such as DORA and NCSC CAF, control standards such as NIST CSF 2.0 and ISO 27001, and evidence such as certifications and supplier assessments.”]
Combining frameworks is less work than it sounds, because they ask about many of the same things. As our CEO Haydn Brooks puts it, “most companies need a firewall, most companies need an IDS... the actual controls people implement, regardless of the standards they adopt, tend to be the same.” Map one set of controls once, then report against whichever framework each audience asks for.
NIST CSF 2.0 is a voluntary, cross-sector framework with six functions, including a new Govern function. Its supply chain category, GV.SC, sets out ten outcomes covering supplier prioritisation, contract requirements, due diligence, ongoing monitoring, incident participation and what happens after a relationship ends. NIST SP 1305 explains how to use GV.SC to build a supply chain risk management capability.
ISO/IEC 27001:2022 is the current edition, amended in 2024, and it includes controls for supplier relationships within a certifiable information security management system. ISO/IEC 27036-2:2022 goes further, specifying requirements for managing the supplier and acquirer relationship itself. A 27001 certificate tells you about the supplier’s own management system, within its stated scope.
The NCSC’s supply chain security guidance sets out 12 principles for gaining and keeping control of your supply chain. Later NCSC guidance turns them into practical steps for assessing suppliers. Any UK organisation can use it.
The Cyber Assessment Framework is different in purpose. It’s an outcomes-based framework used to assess organisations responsible for essential functions, including operators regulated under NIS and UK government bodies through GovAssure. Its principle A4 covers supply chain, including secure software development and support. Treat CAF as a requirement only where your regulator or assurance route applies it.
DORA, the EU Digital Operational Resilience Act, requires in-scope financial entities to manage risk from ICT third-party providers. That includes keeping a register of information on contractual arrangements, assessing providers before contracting, including required terms in contracts, monitoring them and planning exits. Financial services firms with EU operations should check scope against the official regulation text.
DORA has applied since 17 January 2025, and Articles 28 to 30 hold its core third-party provisions. ICT providers to in-scope firms usually meet DORA through contract terms rather than as regulated entities themselves.
Requirements depend on sector and location. Financial services firms in the EU fall under DORA, and UK firms face FCA and PRA expectations on outsourcing and material third parties. UK public sector bodies and operators of essential services are guided by the NCSC Cyber Assessment Framework, and NIS rules apply to some sectors.
For many teams, the trigger is an audit finding or a regulatory deadline, and supply chain is often where the finding lands. The main regimes today:
It’s tempting to rely on supplier certifications such as Cyber Essentials Plus, ISO 27001:2022, alignment with the NIST Cybersecurity Framework, PCI DSS compliance or SOC 2 reports. They’re useful evidence, but each covers a defined scope, and none gives you the full picture of what a supplier means for your service, your data and your dependencies. Check what each certificate covers before relying on it for a specific relationship. Our assessment framework asks suppliers about their certifications and the wider controls around them.
Bring procurement, legal and the business owners of critical services into those answers early, because the framework only works if it fits how suppliers actually arrive. Design the process before choosing a tool, then automate the parts that stop scaling.
For a quick view of where you stand today, run the Supply Chain Risk Exposure Assessment.
A TPRM framework sets what to cover, and leaves the method to you. NIST CSF 2.0 expects supplier risk to be managed throughout the relationship, and the NCSC’s CAF expects ongoing supply chain management, but neither prescribes a cadence, a tool or a method. Three operating problems sit outside what any framework solves on its own.
Evidence currency is how recently a supplier’s answers and documents were confirmed as true. Most programmes capture it at onboarding and again at the annual review. Between those points, a supplier can move hosting provider, add a subprocessor or suffer an incident without your record changing.
Security teams in financial services put it plainly: if the process is manual, it will be annual at best. An annual review is reasonable for a low-risk supplier. The problem is when it is the only cadence for the suppliers you most depend on.
One-to-one collection means every customer sends its own questionnaire to every supplier, in its own format. Questionnaires are useful evidence. The cost comes from repetition. A supplier with 200 customers answers near-identical questions about encryption, access control and incident response in dozens of spreadsheets, and every answer is out of date as soon as it’s sent.
Both sides feel it. Suppliers slow down or stop responding, and the security team spends its week chasing. In public sector supply chains, smaller suppliers can be overwhelmed by the sheer volume of questions, even when their controls are sound. Practitioners regularly ask why every organisation runs its own due diligence on the same supplier. As supplier lists grow, the overhead grows with them, while team headcount usually doesn’t.
Sharing evidence across customers removes much of that repetition, but it doesn’t move accountability. You still decide what a supplier’s answers mean for your service, your data and your risk appetite.
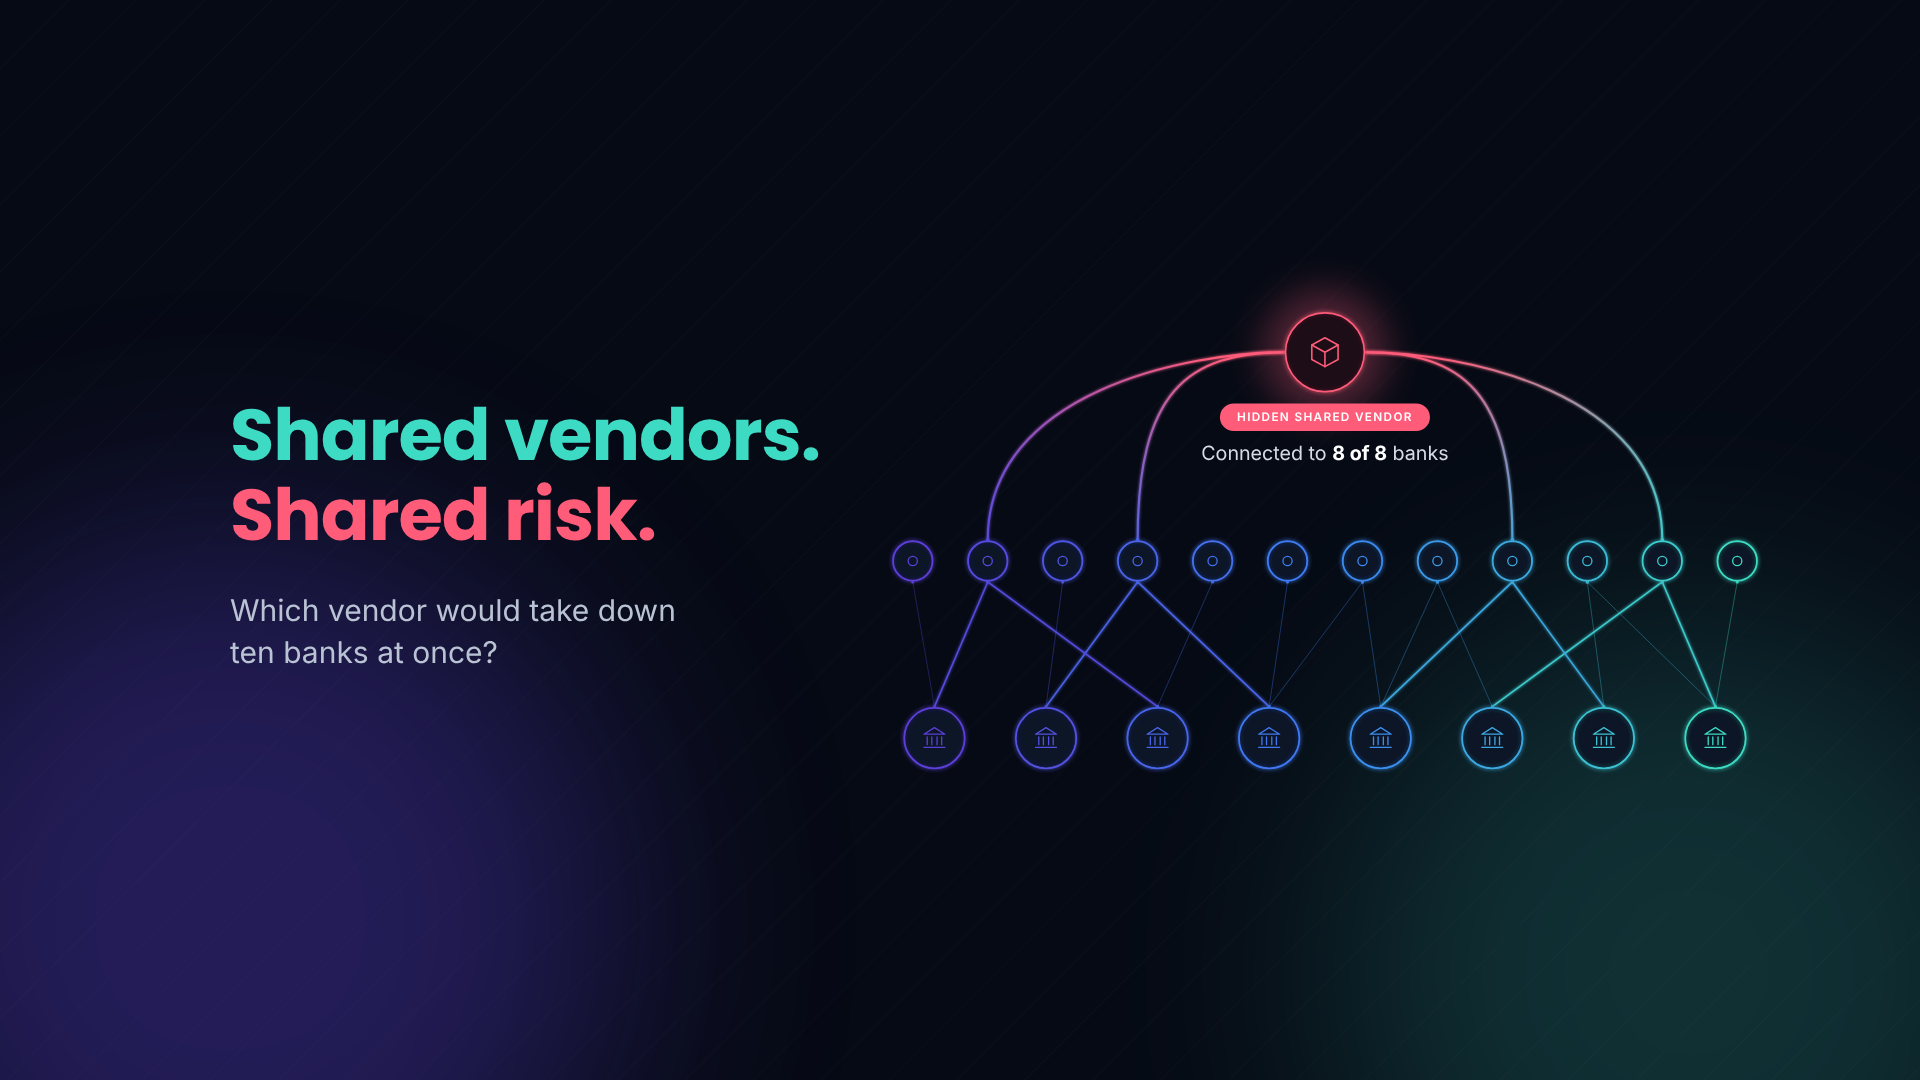
A fourth party is your supplier’s supplier. Concentration risk is what happens when many of your suppliers, or many organisations in your sector, depend on the same provider. Frameworks ask you to know and prioritise your suppliers, but a questionnaire sent to one supplier tells you little about the providers it shares with everyone else. Shared dependencies therefore tend to surface during an incident, when several suppliers report the same problem at once.
Full mapping of every fourth and fifth party isn’t realistic, or necessary, for every supplier. Start with the providers behind your top tier.
Fixing all three is an operating choice. It means assessing once and reusing evidence, triggering reviews when something changes, and seeing shared dependencies across organisations rather than inside one.
The TPRM lifecycle runs from planning and supplier identification, through due diligence and assessment, then contracting and onboarding, continuous monitoring, and finally offboarding and termination. Many programmes are strong until the contract is signed, then lose sight of the supplier. Monitoring is therefore the stage that most often decides whether the lifecycle works.
A crosswalk maps one framework’s requirements against another’s, so you can see where they overlap. The table below lines up each lifecycle stage with the relevant NIST CSF 2.0 outcome and DORA article. A shared stage shows where to look. It doesn’t mean the two impose identical requirements.
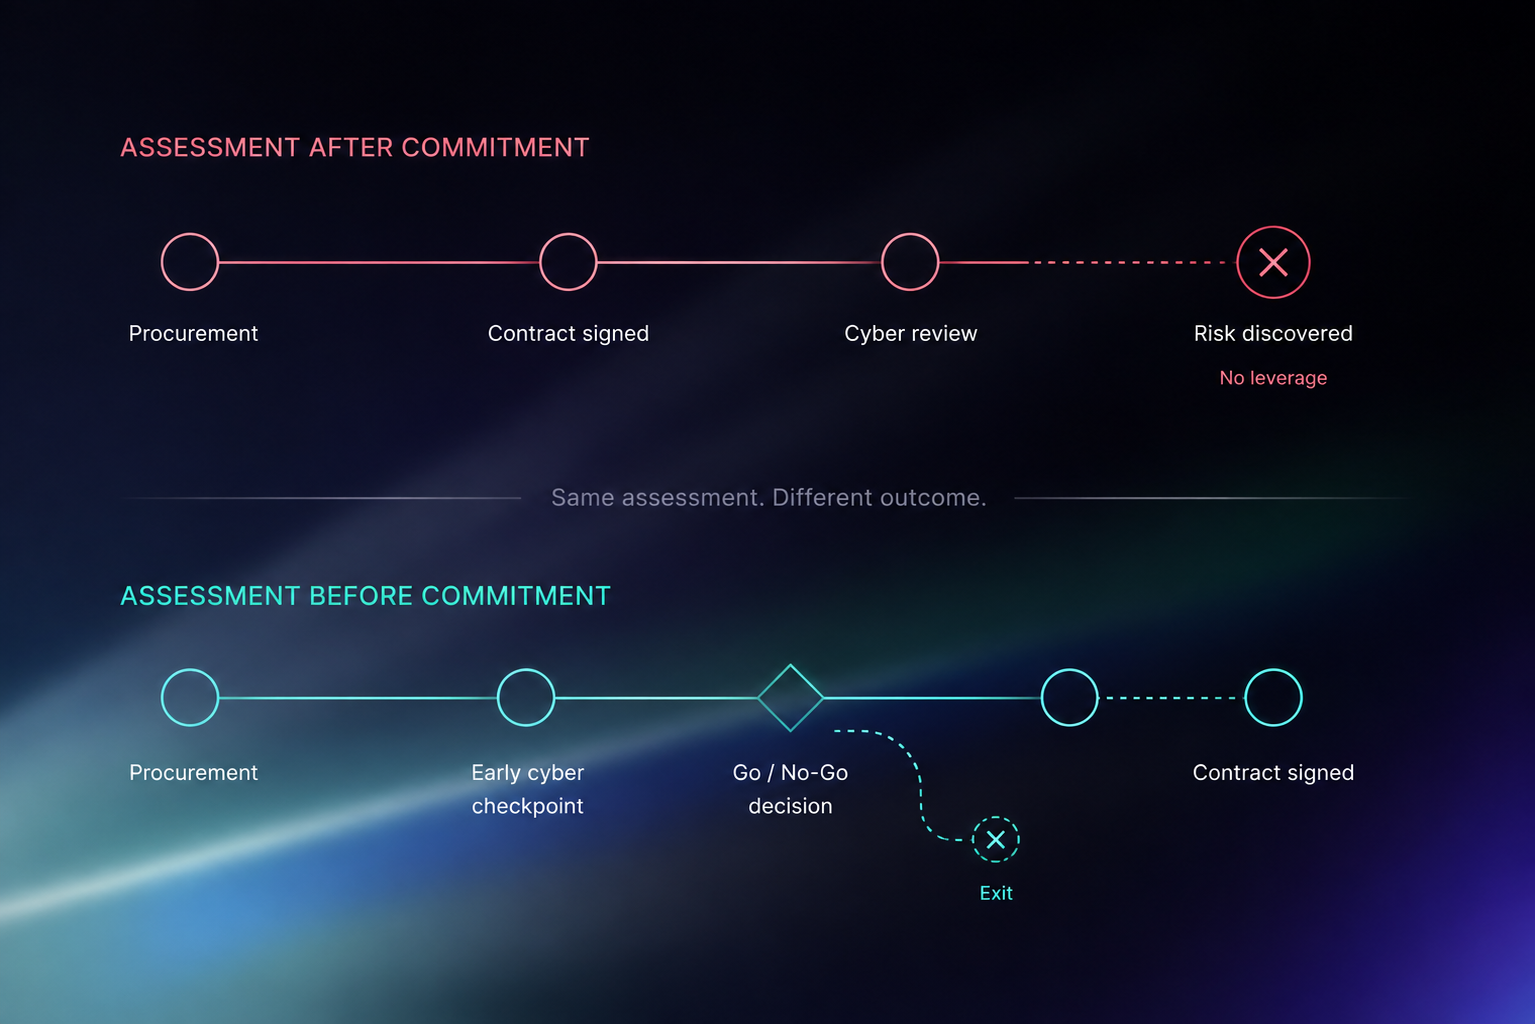
Timing matters as much as depth. A cyber review that happens after signature finds the same risks as one before it, but by then you’ve lost the leverage to require fixes or walk away. Placing a security checkpoint inside procurement, before a go/no-go decision, turns the same assessment into a real choice.
Contracts are where assessment findings become enforceable. Review these with your legal and commercial teams, scaled to the supplier’s tier:
The NCSC’s supply chain guidance covers building security into contracts. In-scope financial entities should check the key contractual provisions in Article 30 of DORA.
Offboarding is the stage programmes most often skip. A supplier that has left can still hold your data and credentials. When a relationship ends:
For critical services, plan the exit before you need it. NIST CSF 2.0 includes post-relationship planning as its own outcome (GV.SC-10), and DORA requires in-scope firms to hold exit strategies for ICT services supporting critical or important functions.
Tier suppliers by two questions: how badly would losing this supplier hurt operations, and how much damage could a compromise of its access do? Score criticality and inherent risk separately, then combine them into a small number of tiers. Base tiers on security impact, not contract value, so assessment depth follows real exposure. Our supplier criticality matrix supports this approach.
Criticality is the harm caused if a supplier’s service stops. Inherent risk is the exposure created by the access and data you give a supplier, before you consider its controls. A supplier can be high on one and low on the other. A facilities contractor might be critical to keeping a site open while holding no data at all.
Two failure patterns come up again and again:
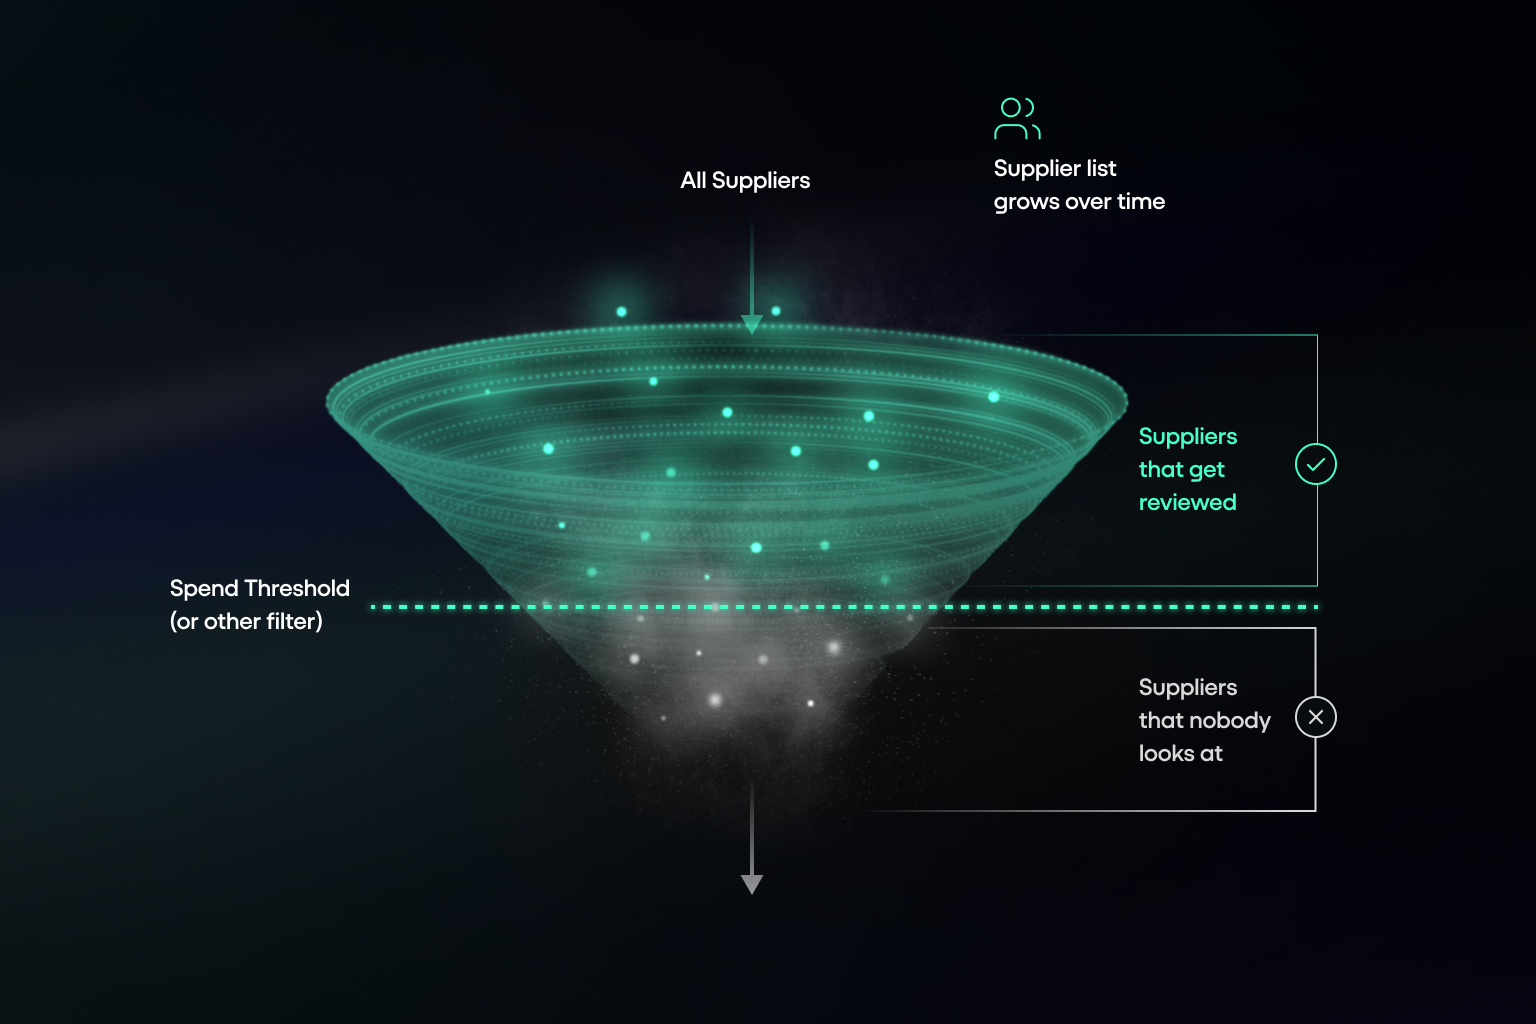
The spend filter is the more dangerous of the two, because the suppliers it hides are often the ones with the most access. In one case we’ve seen directly, an organisation held no central contracts at all for suppliers it spent less than £20,000 a year with. Many of the suppliers with the greatest security exposure sat in exactly that band, as low-cost SaaS tools connected to core systems and data.
Build a supplier inventory by recording, for each supplier, the service provided, the data it can access, the systems it connects to, the business owner and the contract. Add subcontractors and shared infrastructure where known. Spreadsheets go stale quickly, so assign owners and refresh triggers. Procurement records often lack security detail, so combine them with input from security teams.
If you are in scope for DORA, your register of information covers similar ground in a prescribed format. Treat it as a separate output drawn from the same inventory, not a replacement for it.
Depth should follow the tier:
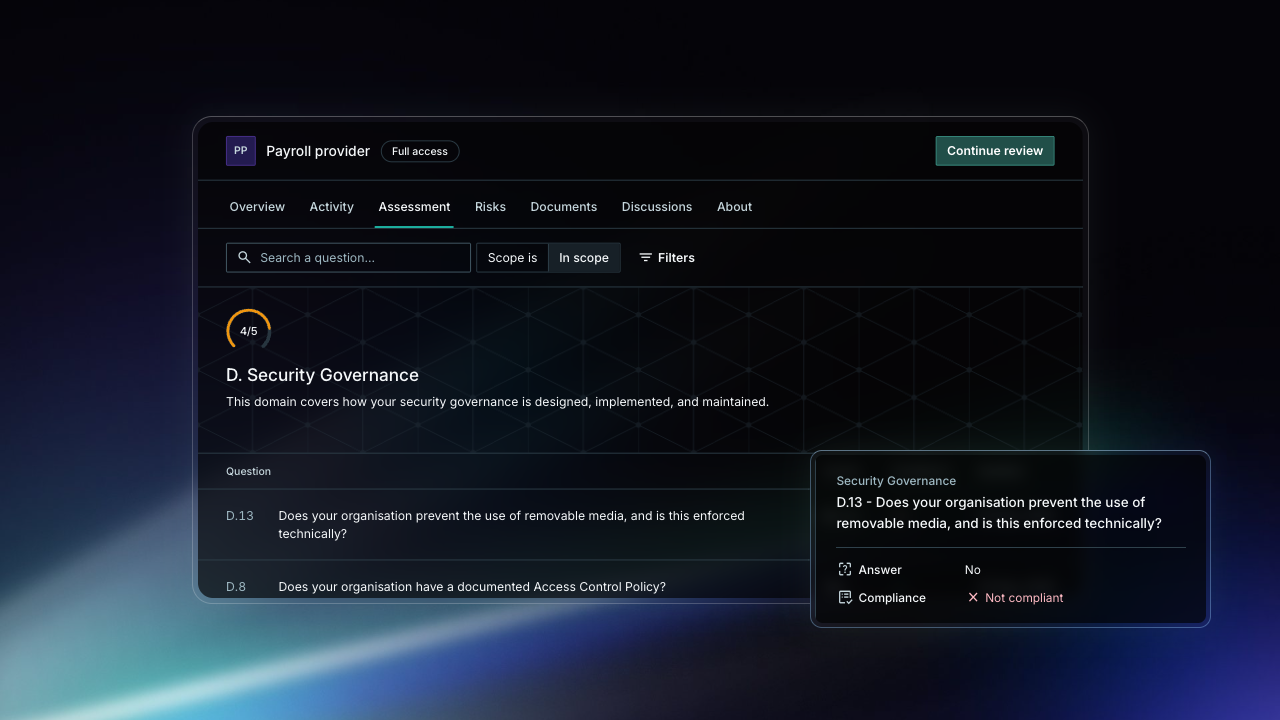
A full assessment usually covers security certifications, data protection, security governance, HR security, IT operations, software development, network and cloud security, physical security, business resilience, supply chain management, financial risk and ESG. For your top tier, self-assessment answers need independent evidence behind them, such as certificate scopes, test results or policy documents.
Asking a small supplier the full set wastes everyone’s time and lowers the quality of the answers you get back.
Continuous supplier monitoring means tracking supplier risk between assessments, not only at onboarding or annual review. It combines current assurance evidence, incident and change alerts, and visibility of fourth parties and shared providers. Risk Ledger’s collaborative network gives visibility beyond direct suppliers, which helps surface shared providers and concentration risk earlier. Manual questionnaires alone rarely get beyond annual cadence.
Continuous monitoring is risk-led assurance between scheduled assessments. It doesn’t mean a live feed on every supplier. Financial services security teams have rightly challenged the idea that six-monthly reattestation counts as continuous, because it is still a check at a single point in time.
What makes monitoring continuous is what happens between scheduled reviews:
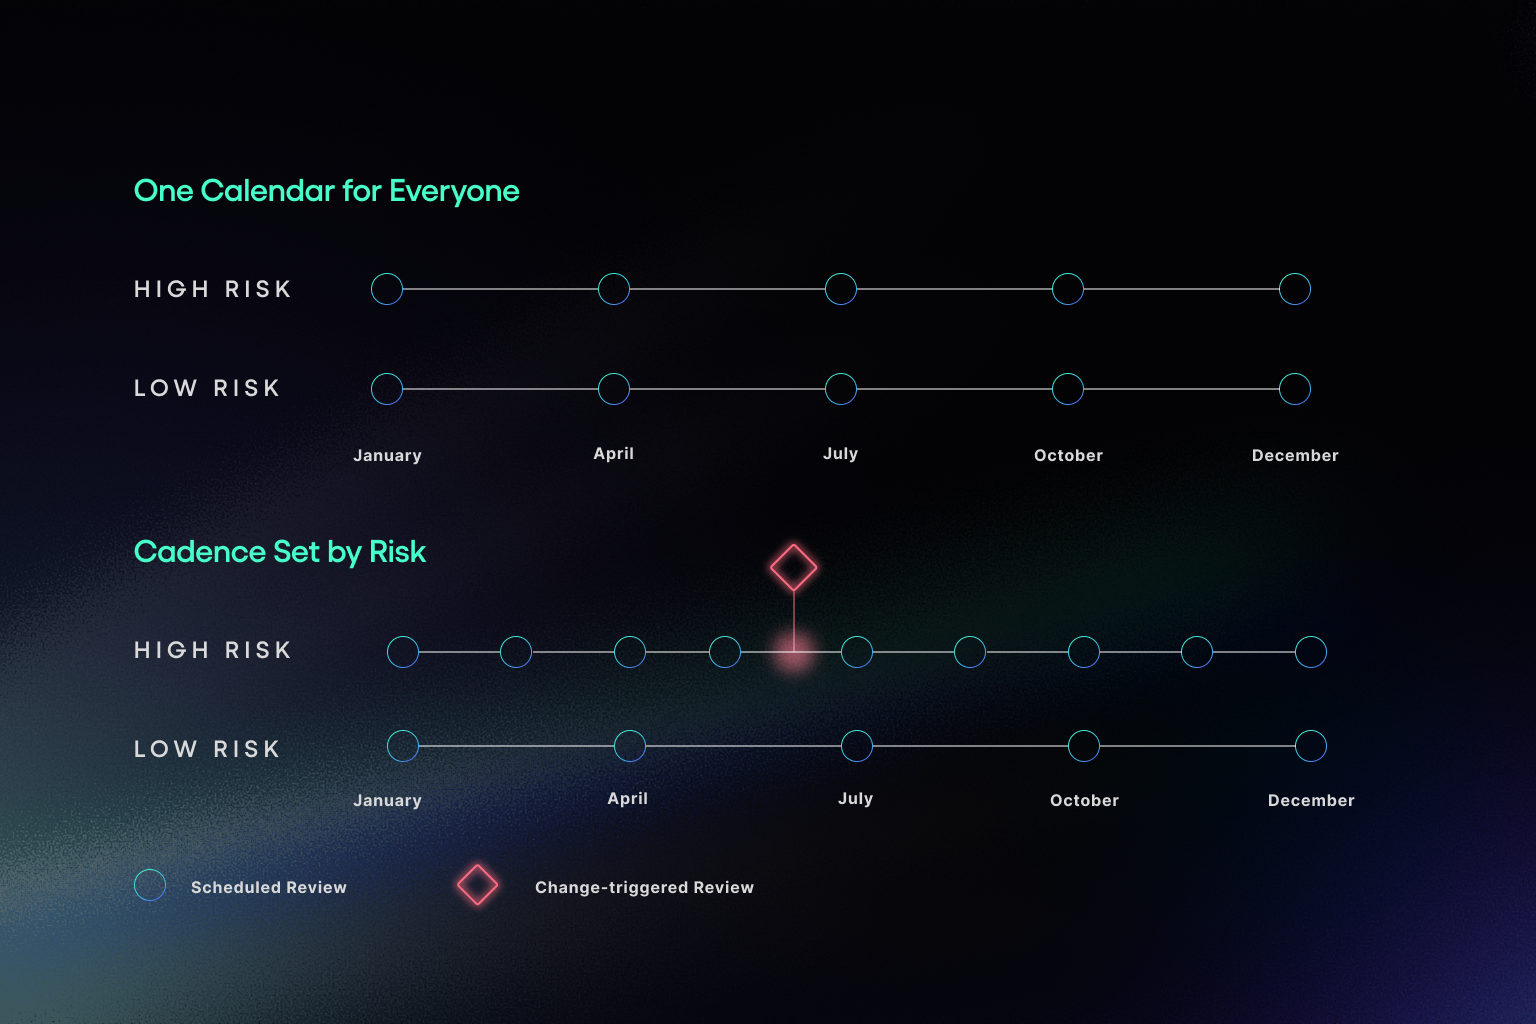
Neither NIST CSF 2.0 nor CAF sets a monitoring cadence. Both expect supplier risk to be managed throughout the relationship and leave the method to you. The practical risk is noise. An alert that doesn’t reach the supplier’s owner with a clear decision attached just adds to someone’s inbox.
In 2023, the Cl0p ransomware group exploited a vulnerability in MOVEit Transfer, a widely used file transfer tool. In the UK, staff data at British Airways, the BBC and Boots was exposed through their payroll provider, Zellis, which used MOVEit. None of the three had been breached directly, and MOVEit was their supplier’s supplier.
In 2020, attackers inserted malicious code into SolarWinds Orion software updates, reaching organisations that trusted the product they had bought.
The lesson is narrow. In both cases, the exposure came through software and dependencies that a direct supplier assessment didn’t show. The first question every security team faced was “which of our suppliers use this?”, and teams without a dependency map had to answer it by emailing suppliers one at a time. The same pattern is now emerging around AI tooling, as our analysis of the October 2026 AI supply chain attacks shows.
Data and maps only go so far in an incident. Relationships with the people at critical suppliers matter as much.
"The best supply chain teams I'd ever worked in were ones where I knew the security teams at my critical suppliers, so that if something did go wrong, I could call them up and say, 'What's going on? How can we help? What's the impact on us?'"
Measure a TPRM programme by whether it reduces uncertainty about the suppliers you depend on. Report to the board on coverage of critical suppliers, currency of assurance, open findings and remediation, and visibility of fourth-party dependencies. Add incident readiness, such as how quickly you can identify exposure. Show trends against your stated risk appetite.
Measurement splits into two jobs. Activity measures tell the team whether the process is running. Decision measures tell the board whether risk is actually going down.
Activity measures are useful week to week:
Decision measures belong in board reporting:
Activity measures can be gamed. A programme that sends more questionnaires every quarter looks busy without becoming safer, so set targets on the decision measures and use the activity ones to explain movement.
For directors: The question boards ask in an incident is “are we exposed?” A programme that can answer it from its own records within hours, naming the suppliers and services affected, is in a different position from one that starts by emailing suppliers. Ask your team which of those you have today.
Security owns the risk decision. Governance has to cover every route a supplier comes in by, including purchases made without security involved. One public sector security lead estimated that around two thirds of digital procurement in their organisation happened outside their area of responsibility, mostly as departmental purchases, renewals and free trials.
Procurement process security closes that route. Add a security checkpoint to procurement before contract award, scaled to the supplier’s tier, and make the business owner accountable for flagging new data flows. Tier by harm rather than contract value, so low-spend tools with high access still trigger a review. Write the thresholds into a risk appetite statement and a supplier security policy, so decisions don’t depend on who happens to be asked.
For who does what before, at and after contract award, see Procurement and Security in the Public Sector: Who Does What Before, at and After Contract Award.
We built Risk Ledger around one standardised assessment framework that suppliers complete once and share with every customer they work with. Our control framework covers ISO 27002, the NIST Cybersecurity Framework, the NCSC Cyber Assessment Framework and Cyber Essentials. Customers then apply their own policies on top, reflecting their risk appetite, without sending a new questionnaire.
We designed it to fix the three problems a framework leaves to you.
This is a collaborative model. Organisations and their suppliers manage and reduce risk on a shared platform, rather than each running a private version of the same exercise.
The trade-off is real, and our CEO is open about it.
"`Risk Ledger gives you a common framework, so you're getting a much broader data set against a much broader number of suppliers."
Shared evidence changes the workload. It doesn’t change who owns the risk. You still decide what a supplier’s answers mean for your services, and using our framework doesn’t make you compliant with DORA or any other regulation on its own.
Explore the assessment framework domain by domain, or see how one standardised framework replaces supplier spreadsheets.
Design the process first, then automate the parts that stop scaling beyond a few dozen suppliers. Whichever platform you choose, check that it supports:
For a fuller buyer’s guide, see TPRM tooling and the capabilities to look for.


Monthly research, case studies and practical guides you won't find anywhere else.
Join thousands of security managers turning their TPRM programmes into success stories.